Digital Operational Resiliency Act (DORA)

Ensure compliance and reduce risks with adversarial exposure validation.
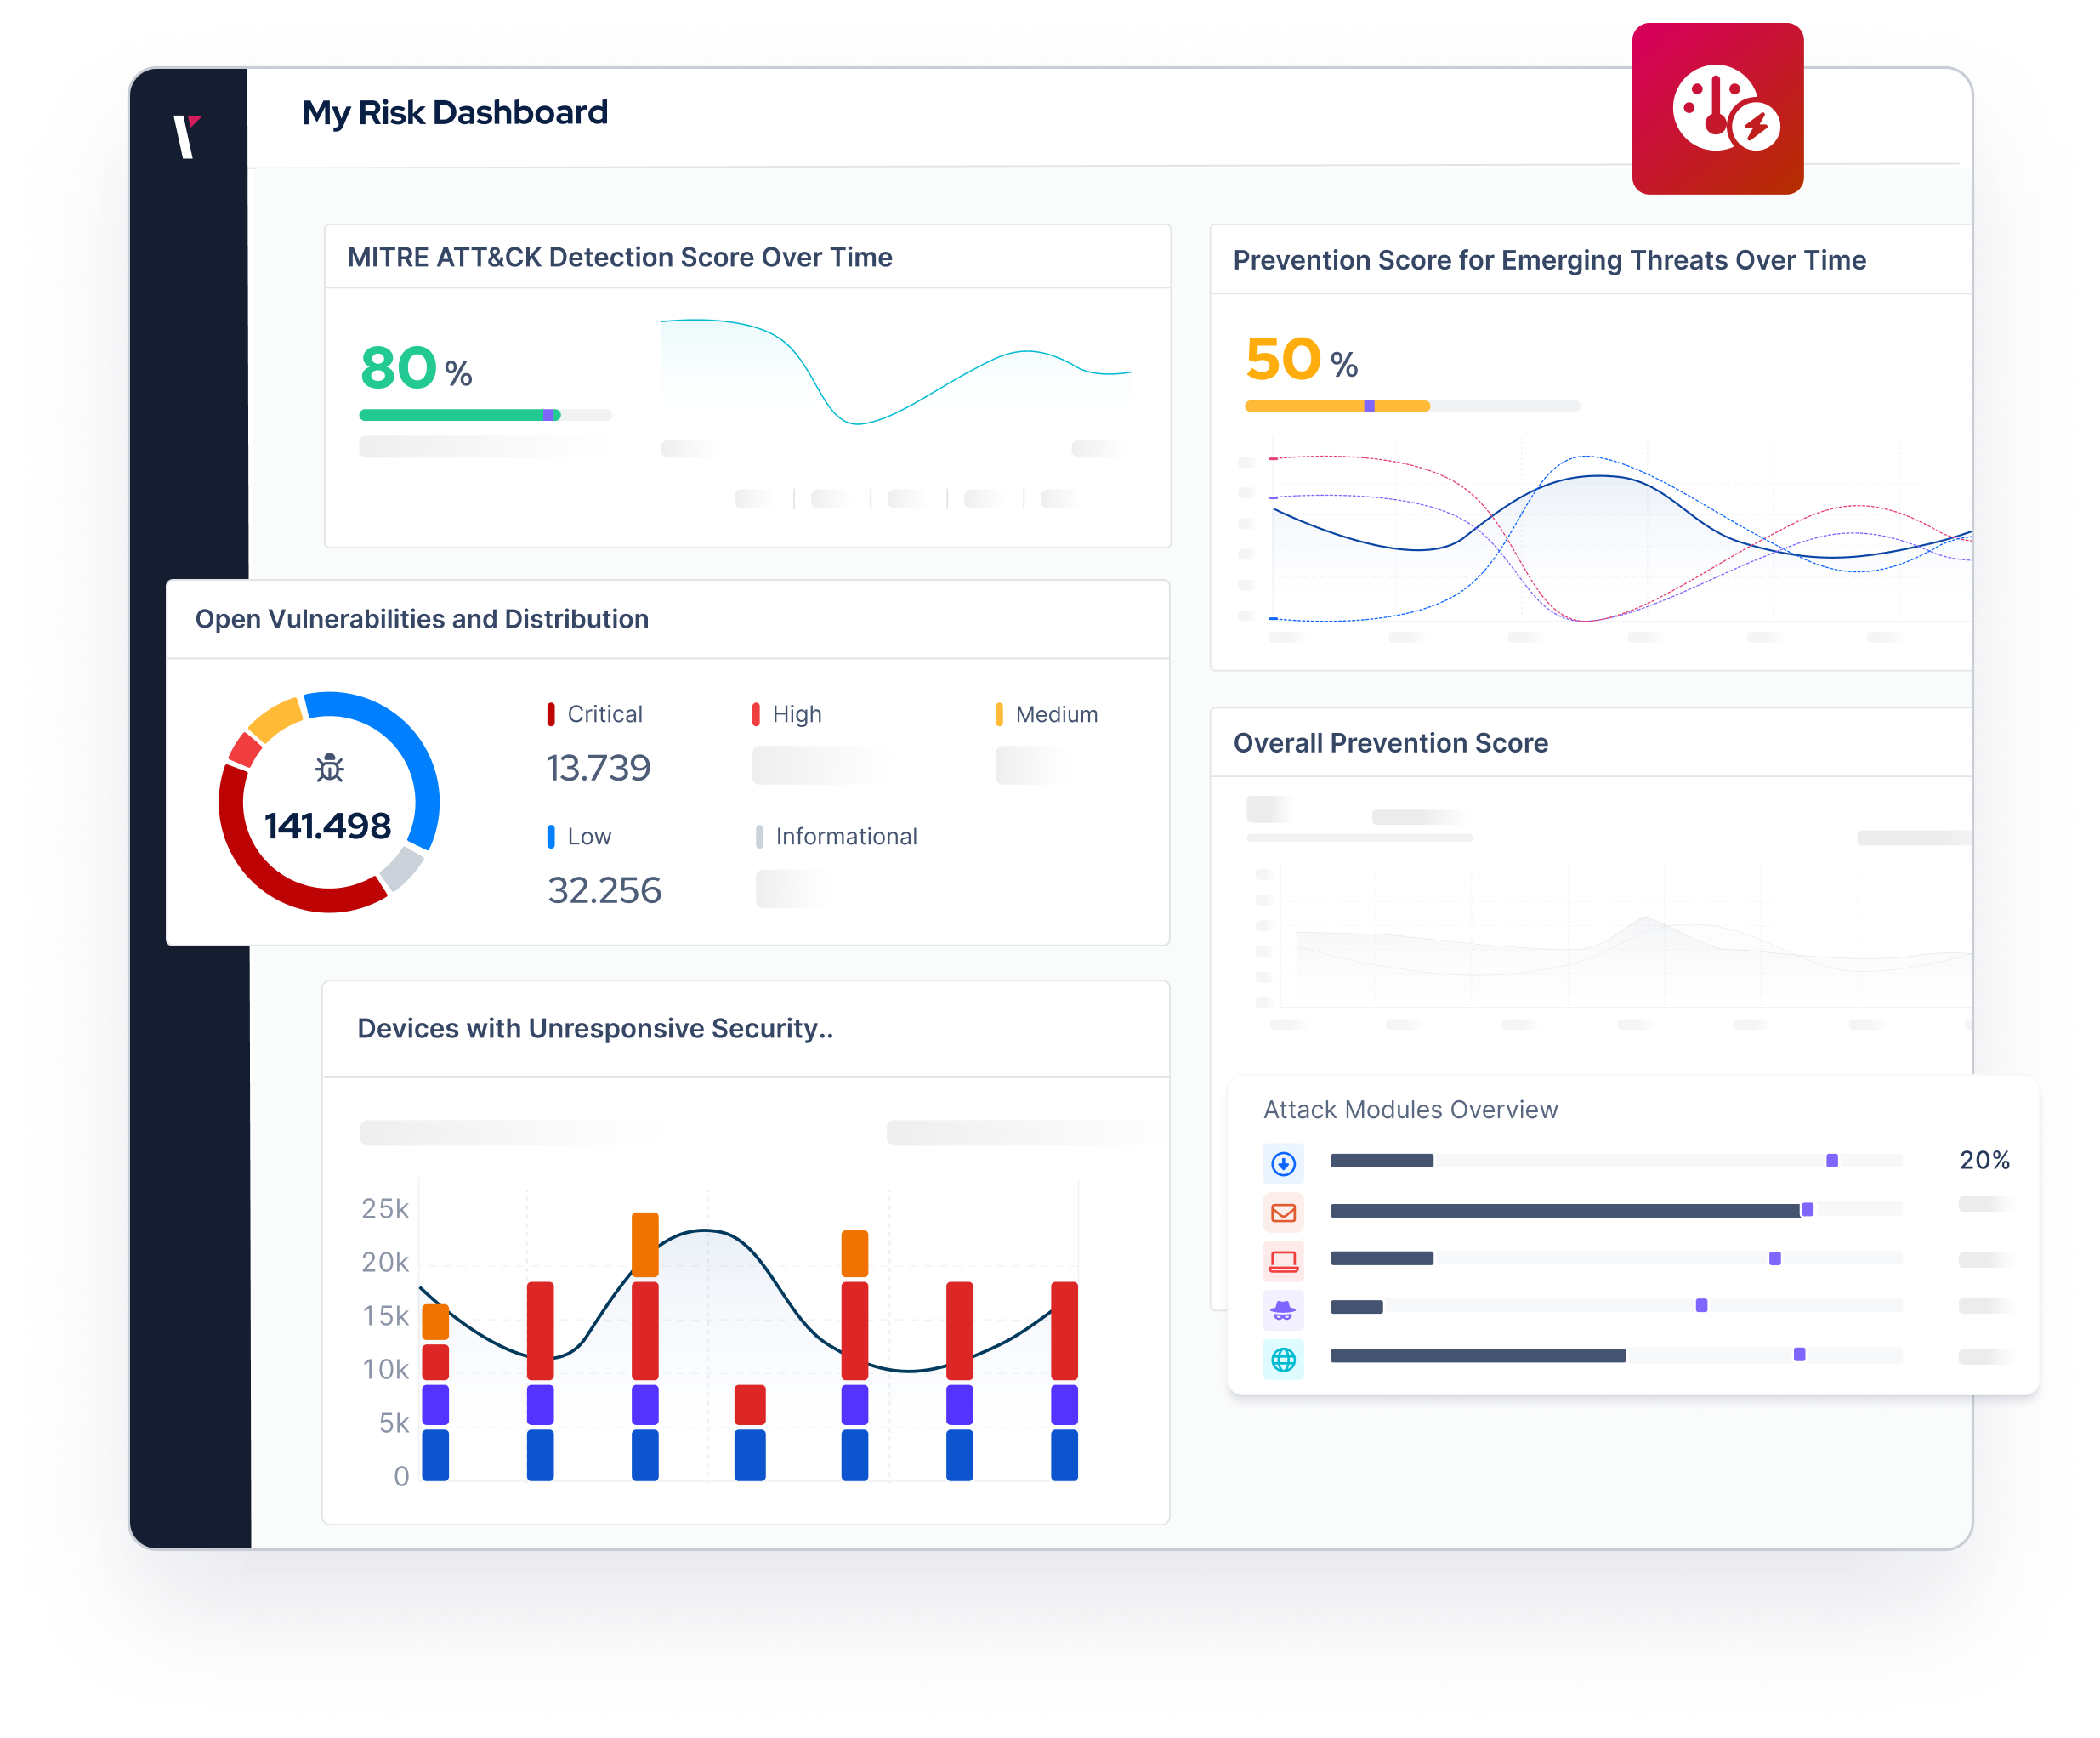
Picus Security Control Validation: prevention results 96% and detection results 68%, an AI assistant asked about the techniques of Lazarus Group, two threat profiles and the Simulate Now button

Achieve Regulatory Readiness with Continuous Security Validation

The Digital Operational Resilience Act (DORA) sets the standard for financial institutions across the European Union to manage ICT risks, maintain operational continuity, and combat evolving cyber threats. By addressing critical areas such as risk management, incident response, and third-party oversight, DORA establishes a unified standard for digital resilience.

DORA contains five pillars to cover security controls that financial organizations are required to meet to comply.

5 Pillars of DORA:

  • ICT Risk Management

  • ICT-Related Incident Management

  • Digital Operational Resilience Testing

  • Managing ICT Third-Party Risk

  • Information-sharing Arrangements

Benefits of Security Validation for DORA Compliance

  • Reduce risk by identifying and addressing vulnerabilities before they are exploited.

  • Focus resources effectively by prioritizing exposures based on real-world scenarios.

  • Maintain compliance over time with continuous testing and validation of security controls.

  • Maximize return on investment by validating security investments.

ON-DEMAND WEBINAR

Accelerate DORA Compliance With Picus

Watch now and learn:

  • How Security Validation platforms support compliance

  • Threat-Led Penetration Testing’s role in securing financial entity critical live production systems

  • How to accelerate your process, combine and correlate exposure data, and validate security control effectiveness
How to Support DORA Compliance

Autonomous Exposure Validation Platform is engineered to help financial institutions automate threat-led penetration testing and support DORA compliance.
 

ICT Risk Management

Financial institutions must have an internal governance and control framework for managing ICT risks.
This risk management framework must cover risk identification, protection, detection, response, and recovery.

How to Address the Gap

  • Simulate real-world cyberattacks to assess the efficacy of your security controls, including firewalls, endpoint protection, and intrusion detection systems. Picus ensures your defenses can handle the evolving threats your organization faces, aligning with DORA’s ICT Risk Management pillar.
  • Prioritize risk mitigation strategies by mapping simulation results to MITRE ATT&CK® and other frameworks. Picus Security Control Validation (SCV) supplies actionable mitigation recommendations, including vendor-specific prevention signatures and detection rules, to save time and effort.
  • Continuously improve your security posture by tracking changes over time, including your security score, device performance, and threats, to maintain and exceed compliance with DORA requirements.

Reducing Risk in Finance with Exposure Validation

Discover how finance security teams focus on critical risks, reducing immediate vulnerabilities as attack surfaces rapidly expand.
Picus platform overview

Proof

Trusted by Security Teams, Recognized by the Industry

  • Outstanding Experience with Picus – A Game-Changer in Security Validation. The platform is intuitive, the reporting is clear, and the actionable insights significantly enhance our overall security posture.

  • It allows me to test current cyber attack scenarios within my own environment, which is extremely valuable for improving our security posture.

Resources

Discover Risk & Compliance Content

  • Before Remediation Lands: How CISOs Can Close the Window of Exposure

    Before Remediation Lands: How CISOs Can Close the Window of Exposure

  • Gartner Report: Prioritize What Attackers Will Exploit: 4 Elements of Strong Exposure Prioritization

    Prioritize What Attackers Will Exploit: 4 Elements of Strong Exposure Prioritization

  • 5 Capabilities Every Exposure Management Program Needs

    5 Capabilities Every Exposure Management Program Needs

FAQ

Frequently Asked Questions

About Digital Operational Resiliency Act (DORA)

What is DORA Framework?

DORA Framework refers to the Digital Operational Resilience Act (DORA), a regulation established by the European Union to ensure financial institutions can withstand and recover from ICT-related disruptions. It focuses on key areas such as risk management, incident response, resilience testing, third-party oversight, and information sharing.

Why DORA compliance is important?

DORA compliance ensures a unified approach to digital operational resilience, reducing risks from ICT disruptions, mitigating vulnerabilities, and fostering trust across the financial sector. It also aligns financial institutions with EU-wide security standards to protect stakeholders and maintain business continuity.

How does DORA Framework relate to other regulations?

The DORA Framework shares similarities with standards such as ISO 27001, ISO 27002, ISO 27005, and ISO 22301, as it adopts many of their concepts. However, DORA is a regulation specific to the financial sector and takes precedence over other directives like NIS2 for organizations within its scope. While NIS2 applies to a broader range of entities, financial institutions covered by DORA are exempt from NIS2 compliance. Unlike GDPR, which focuses on personal data protection, DORA addresses the resilience of all ICT systems and operations.

Who needs to comply with DORA Framework?

The DORA Framework applies to a broad range of financial institutions, including banks, investment firms, insurance companies, and ICT service providers. Other covered entities include credit rating agencies, cloud service providers, and cryptocurrency firms operating in the EU.

What happens if my organization fail to achieve DORA compliance?

Non-compliance with DORA can result in significant financial penalties, including fines of up to 2% of annual global turnover. Additionally, failure to comply may lead to reputational damage and operational disruptions due to unmanaged ICT risks.

See the Picus Platform

  • See Picus Run on Your Environment

    In a live demo, watch Picus validate a real exposure end to end, from exploit to fix to re-test.

  • Discover the Platform

    Simulate real-world cyber threats in minutes and see a holistic view of your security effectiveness.