Red Report 2026: The Top 10 Most Prevalent MITRE ATT&CK® Techniques

RR26-hubpage-baner-front-update (1)
WARNING WARNING WARNING WARNING WARNING WARNING WARNING WARNING WARNING WARNING WARNING WARNING WARNING WARNING WARNING WARNING WARNING WARNING WARNING WARNING WARNING WARNING WARNING WARNING WARNING WARNING WARNING WARNING WARNING WARNING
DIGITAL PARASITE DIGITAL PARASITE DIGITAL PARASITE DIGITAL PARASITE DIGITAL PARASITE DIGITAL PARASITE DIGITAL PARASITE DIGITAL PARASITE DIGITAL PARASITE DIGITAL PARASITE DIGITAL PARASITE DIGITAL PARASITE DIGITAL PARASITE DIGITAL PARASITE DIGITAL PARASITE DIGITAL PARASITE DIGITAL PARASITE DIGITAL PARASITE DIGITAL PARASITE DIGITAL PARASITE DIGITAL PARASITE DIGITAL PARASITE DIGITAL PARASITE DIGITAL PARASITE DIGITAL PARASITE DIGITAL PARASITE DIGITAL PARASITE DIGITAL PARASITE DIGITAL PARASITE DIGITAL PARASITE

Methodology

Between January 2025 and December 2025,
Picus Labs analyzed 1,153,683 unique files, of which
1,084,718 (94.02%) were malicious.

This research mapped over 15.5 million adversarial
actions
to the MITRE ATT&CK® framework.
Sourced from commercial threat intel,
sandboxes, and underground forums, this data
identifies the 2026 tactical landscape to help
teams shift from hunting files to hunting behavior.
Red report 2026
2026-RR-methodology-web

Key figures

Key figures at a glance

Red Report 2026 6th annual edition Published By Picus Labs

Dataset and headline findings of the Red Report 2026. Percentages are shares of the 1,084,718 malicious files analyzed in 2025 unless stated otherwise.

Red Report 2026 — key figures
Metric Value Period & scope Source
Unique files analyzed 1,153,683 January–December 2025; commercial and open-source threat intel, security vendors, sandboxes, underground forums Red Report 2026, p. 21 (Methodology)
Files classified as malicious 1,084,718 (94.02%) Share of the 1,153,683 unique files analyzed in 2025 Red Report 2026, p. 21
Malicious actions detected 15,544,909 Across the malicious files; ≈14 actions per malware sample Red Report 2026, p. 21
MITRE ATT&CK technique instances identified 13,321,128 ≈12 distinct techniques per malware sample Red Report 2026, p. 21
Most prevalent technique: T1055 Process Injection 30.07% Share of malicious files exhibiting the technique (326,165 samples), 2025 dataset Red Report 2026, p. 21 (ranking example); Top 10 list
Top 10 techniques dedicated to evasion, persistence and C2 80% (8 of 10) 2025 dataset, Top 10 ranking by prevalence Red Report 2026, p. 3, 6
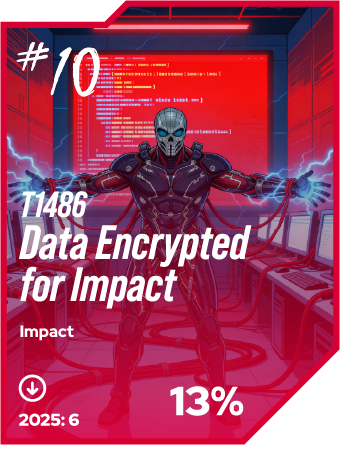
Ransomware encryption prevalence (T1486 Data Encrypted for Impact) 12.94% (down from 21.00%) Share of malicious samples, 2025 vs 2024; a 38% relative decline Red Report 2026, p. 7
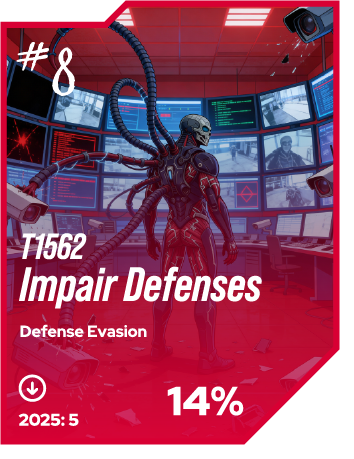
Impair Defenses (T1562) 14.18% (rank #8) Share of malicious samples, 2025 dataset Red Report 2026, p. 9

Methodology

Between January and December 2025, Picus Labs analyzed 1,153,683 unique files (1,084,718 malicious) sourced from commercial and open-source threat intelligence, security vendors, malware sandboxes and underground forums, and mapped 15,544,909 malicious actions to the MITRE ATT&CK framework. Techniques are ranked by the share of malicious files that employ them.

The full report (PDF) is available through the download form on this page.

The Rise of the Digital Parasite

Adversaries have fundamentally traded "predatory" smash-and-grab tactics for "parasitic" silent residency. The Red Report 2026 confirms a strategic pivot toward burrowing into legitimate processes to hide from your organization's immune system. With Defense Evasion, Persistence, and C2 tactics accounting for 80% of the top ten techniques, it is clear that blending in has become far more critical to attackers than breaking in.

KEY FINDINGS

The Anatomy of the Digital Parasite

Discover the six behavioral traits that define modern stealth malware and learn why your current security stack is blind to residency.

Ransomware Encryption Drops 38%

Attackers have abandoned loud encryption for silent extortion, trading immediate disruption for long-lived, high-value network access and data theft.

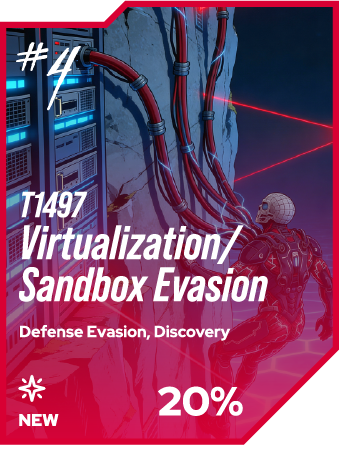
Malware Becomes "Self-Aware"

New threats use trigonometry and mouse-angle math to detect sandboxes, "playing dead" to bypass automated security cameras and analysis.

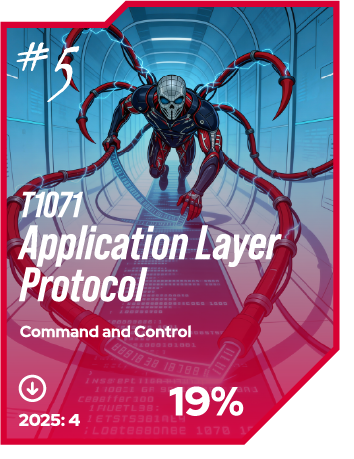
Living Off Trusted Cloud APIs

Adversaries hide commands inside platforms like OpenAI and AWS, masking malicious traffic as legitimate business work to bypass traditional firewalls.

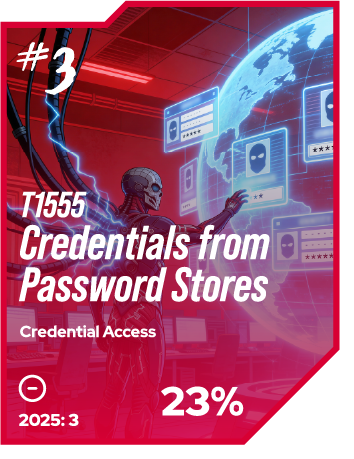
The Strategic Pivot to Logins

Nearly 1 in 4 attacks now targets stored credentials to "log in" rather than hack in, making identity weaponization a primary goal.

80% Focused on Evasion

Eight of the top ten techniques prioritize staying hidden. Success is now measured by dwell time rather than immediate destruction.

Hiding in Plain Sight

Malware renames files to mimic legitimate system processes, hiding in plain sight and turning your trusted environment into its own camouflage.

CHAPTERS OF INFECTION

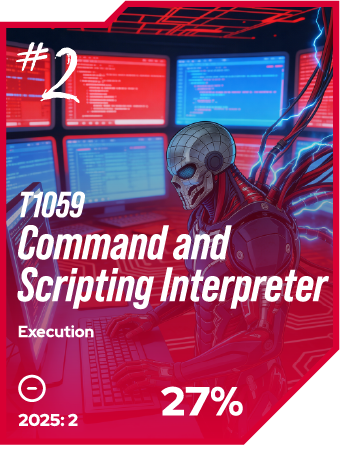
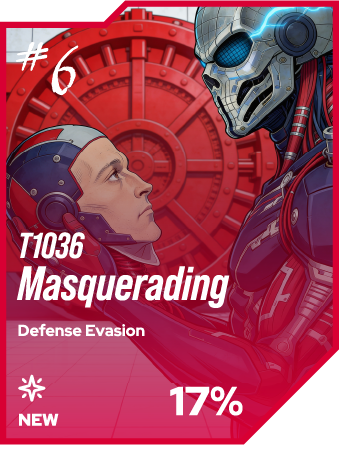
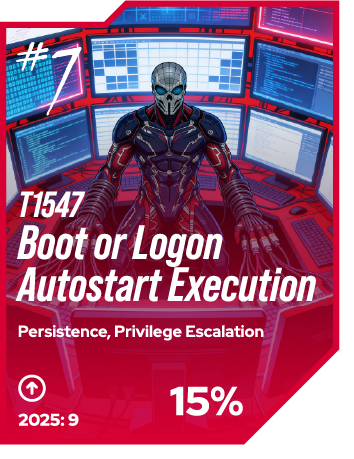
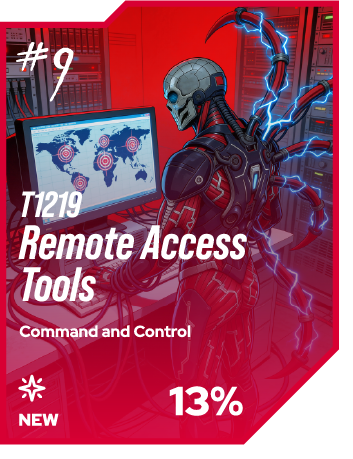
Top 10 MITRE ATT&CK® Techniques

The most prevalent ATT&CK techniques identified in 2025 are ranked by the percentage of malware samples exhibiting each behavior. Click on a technique to explore its details: how to simulate it (red team exercise), how to detect and mitigate it (blue team exercise), and which threat actors and malware leverage it against specific targets.
LIVE DEMO

Simulating the Top 10 ATT&CK Techniques with Picus

March 12, 10:00 AM GMT

Join this live demo to see how Red Report 2026 findings translate into real defensive action. Discover how to validate against 2026’s most prevalent threats, measure control effectiveness, and close gaps with ready-to-apply recommendations before attackers establish persistence.

rr-webinar-play-button-red

Ready to Simulate Real-World Threats
From Red Report 2026?

Validate your defenses against the most prevalent threats of 2026 using the five Red Report Threat Templates.

From Top 10 Techniques to APTs, Threat Groups (Windows & Linux), and Malware, uncover the Digital Parasite by testing your security against the year’s most critical attack techniques.

simulate red report 2026
TOP MITRE ATT&CK TECHNIQUES

Previous Picus Red Reports

Red-report-2025
Red Report 2025

Explore common malware ATT&CK techniques and defend against Infostealer malware.

Picus-RedReport-2024
Red Report 2024

Explore common malware ATT&CK techniques and defend against evasive ‘Hunter-killer’ variants.

Picus-RedReport-2023
Red Report 2023

Discover how lateral movement techniques rose to become the most prevalent adversary tactic.

Picus-RedReport-2021
Red Report 2021

Uncover how ransomware became the #1 cyber threat and how to defend against it.

Picus-RedReport-2020 (2)
Red Report 2020

Learn about the common ATT&CK techniques and how to prioritize cyber risks.

RESOURCES

Discover Our Latest News and Content

See the
Picus Platform

See Picus run on your environment

In a live demo, watch Picus validate a real exposure end to end, from exploit to fix to re-test.

Discover the Platform

Simulate real-world cyber threats in minutes and see a holistic view of your security effectiveness.