
CTEM
Continuous Threat Exposure Management
In today’s evolving threat landscape, proactive security is essential. CTEM helps you stay ahead by continuously identifying, validating, and remediating exposures before attackers exploit them.
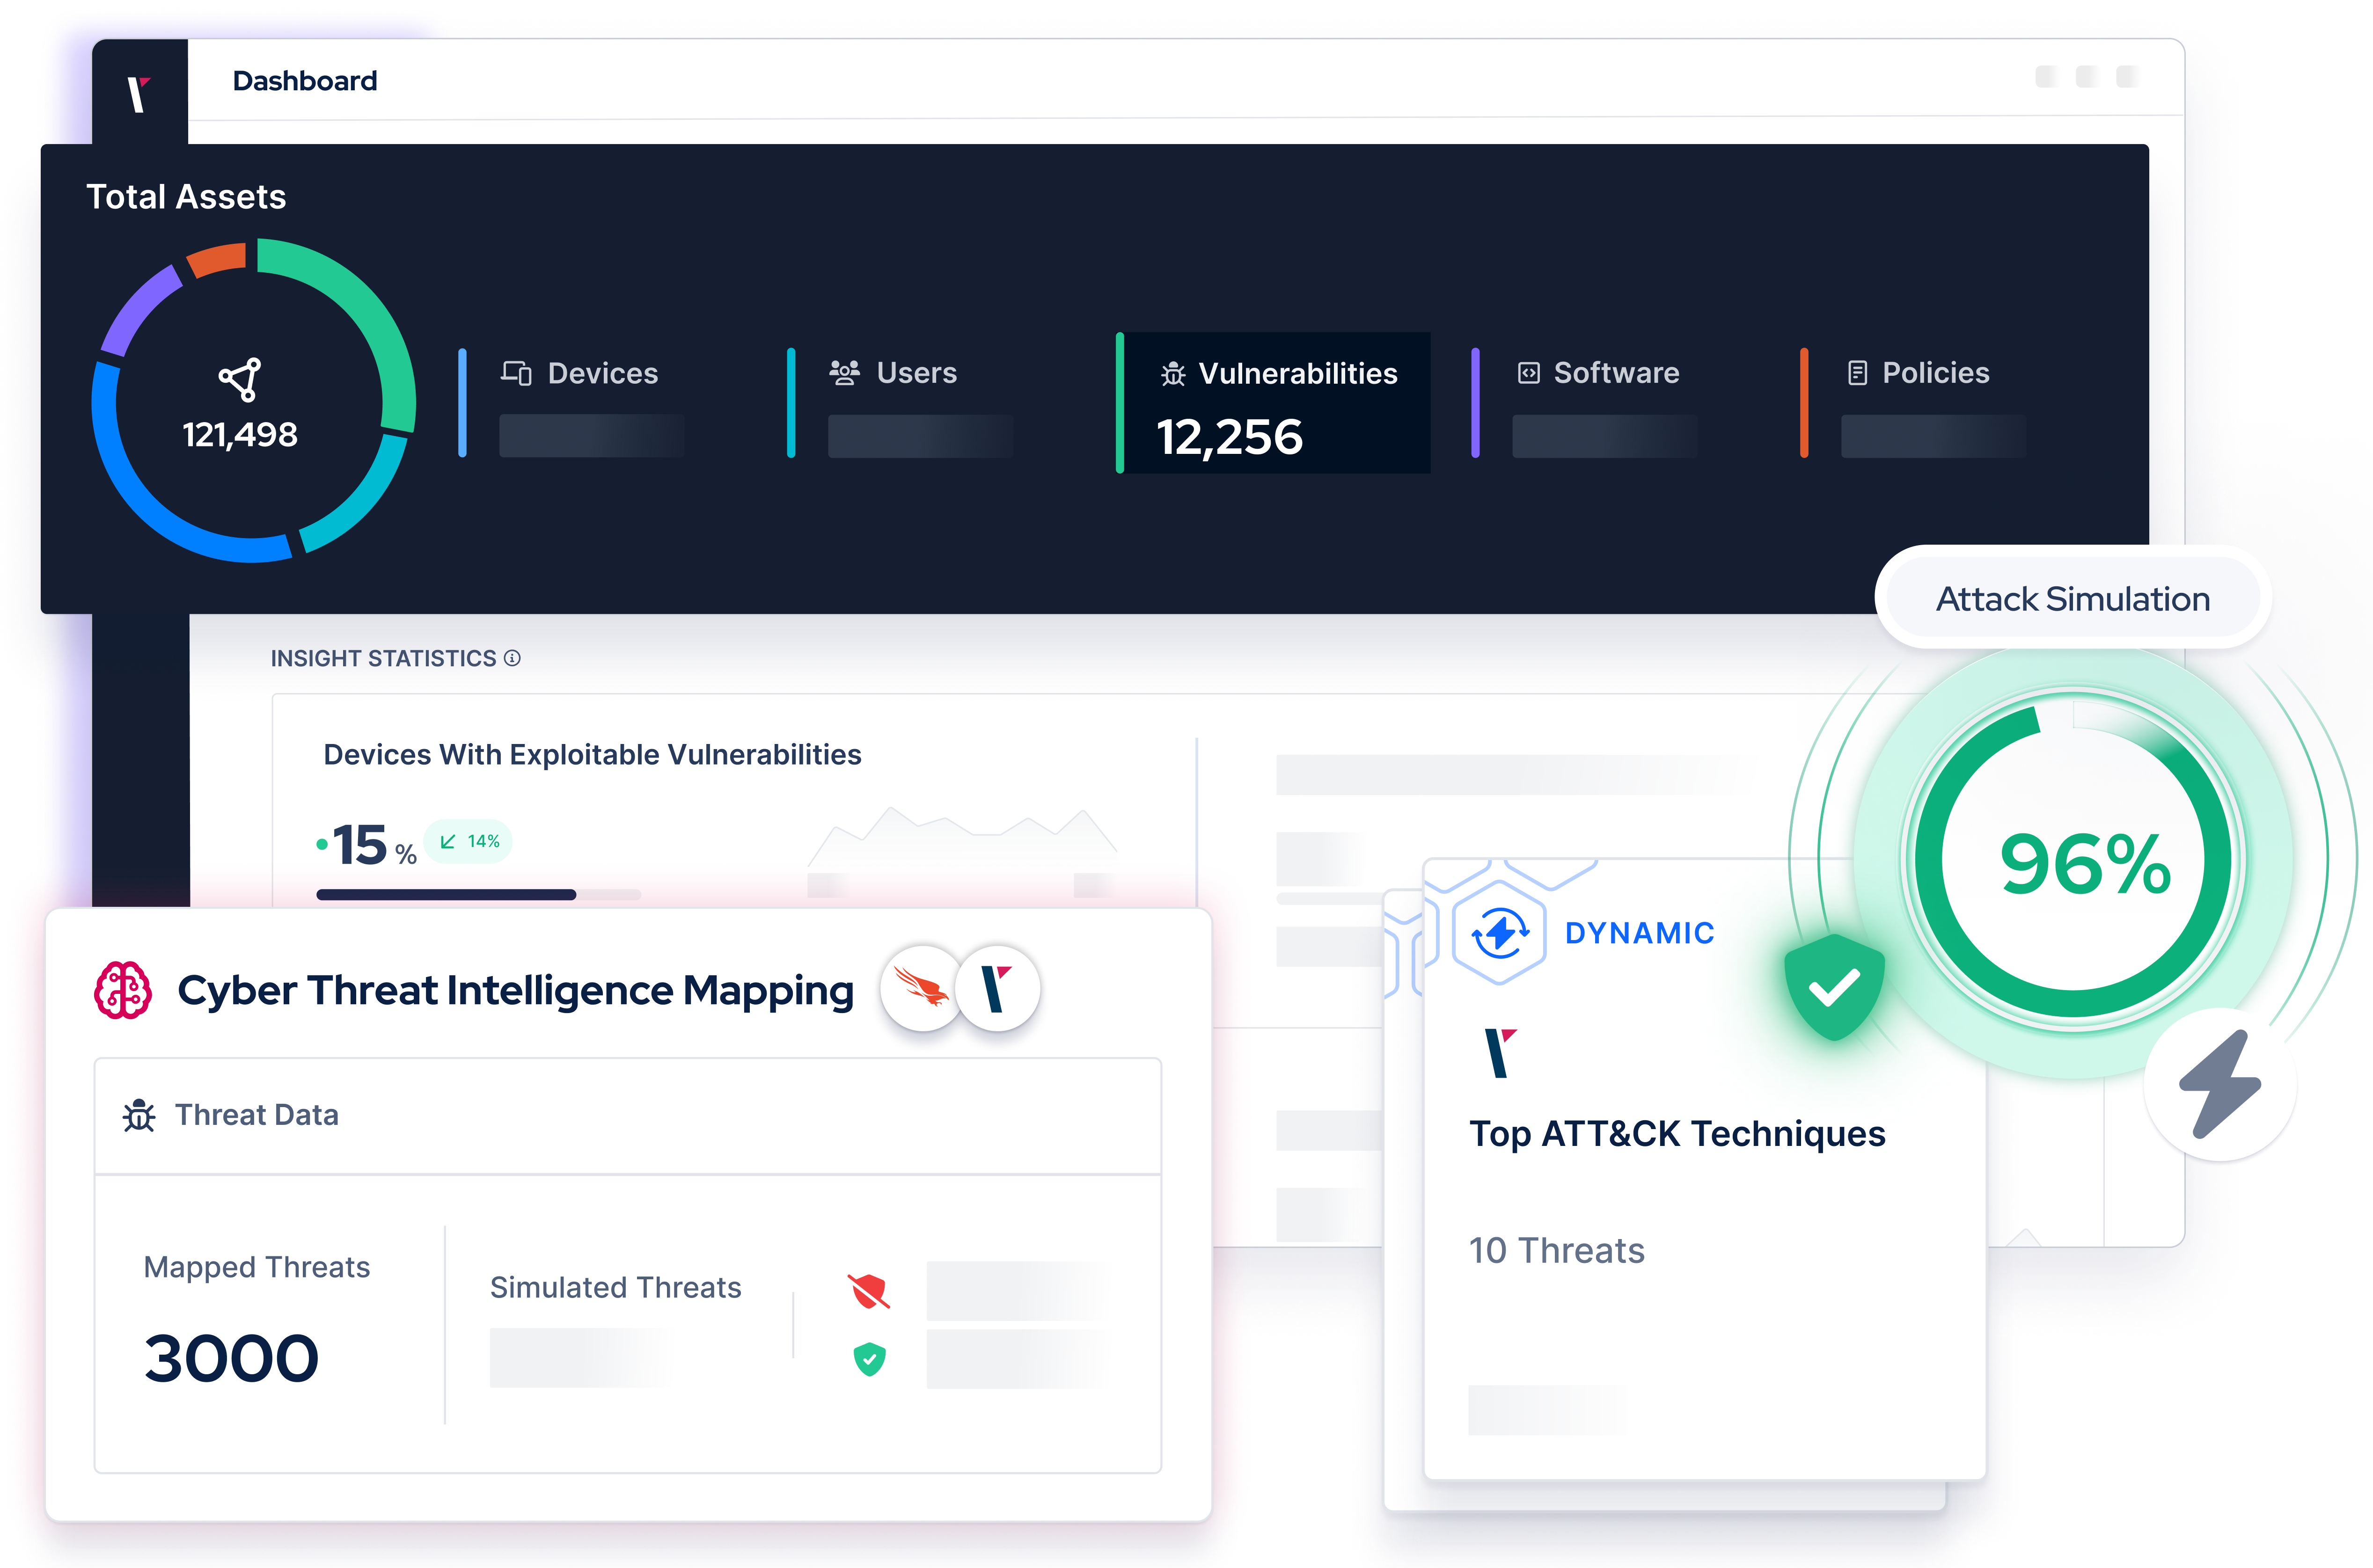
What is Continuous Threat Exposure Management (CTEM)?
CTEM is a continuous, risk-centric approach that empowers security teams to identify, validate, and remediate exposures before adversaries exploit them. It goes beyond static vulnerability lists by simulating real-world attack paths and measuring how effectively your controls protect critical assets across your environment. By doing so, CTEM enables more confident decisions and stronger operational resilience.
Core Components of an Effective CTEM Solution
-
Prioritize exploitable risks, not just CVEs
-
Reveal hidden attack paths across enterprise environment
-
Strengthen defenses for critical assets in cloud and network systems
-
Continuously validate your security controls for effective remediation
Benefits of a Continuous Threat Exposure Management Program
-
Gain greater security visibility.
-
Break down silos.
-
Realize a more proactive approach.
-
Prioritize threats most material to your business.
-
Align your security program with business goals.
-
Make continuous security improvements.
Powering Every Step of CTEM
Five Stages of a CTEM Program
Build a continuous, structured approach to managing exposures across your enterprise.
Picus supports every stage of the CTEM cycle, from scoping to validation, helping you turn visibility into action.
Scoping
Identify and define the critical assets, environments, and business functions to be evaluated. This sets the foundation for exposure management.
Coverage includes
Picus enables flexible and comprehensive CTEM scoping by validating exposures across on-premises, cloud, and hybrid environments. With its broad coverage, Picus ensures nothing is out-of-scope. From targeted assessments to organization-wide validation, security teams can implement their CTEM program wherever it matters most.
Discovery
Map the assets, vulnerabilities, misconfigurations, and potential attack paths across your enterprise, cloud, and hybrid environments.
Coverage includes
Picus uncovers organizations’ attack surface by discovering both known and unknown assets within their CTEM scope. By integrating with vulnerability assessment and attack surface management technologies, Picus expands visibility beyond CVEs, identifying misconfigurations, insecure services, and other vulnerabilities that traditional tools often miss. The platform maps potential attack paths to highlight exposures that could lead to the compromise of critical assets.
Prioritization
Focus on exposures that are most likely to be exploited. Use threat intelligence, asset criticality, and exploitability to rank risks.
Coverage includes
Picus helps security teams prioritize exposures based on the potential impact on their environment. The platform dynamically adjusts risk levels, taking into account critical factors such as exploitability, ease of attack, and the context of business-critical assets. This allows security teams to prioritize the highest-impact exposures, ensuring that resources are focused on mitigating the threats that pose the greatest risk to the organization.
Validation
Simulate real-world attacks to confirm which exposures are truly exploitable in your environment. This step turns assumptions into evidence.
Coverage includes
Picus validates exposures with its leading Adversarial Exposure technologies, including Breach and Attack Simulation (BAS) and Automated Penetration Testing (APT). By simulating real-world attack scenarios, Picus not only confirms the exploitability of identified vulnerabilities but also tests the effectiveness of existing security controls. The platform ensures that security teams focus on the most critical and validated exposures, avoiding wasted efforts on futile pursuits.
Mobilization
Take action to remediate validated exposures and improve defenses. Mobilization also includes ongoing communication between security and IT teams.
Coverage includes
Picus delivers clear, actionable reports with remediation guidance, including vendor-specific prevention signatures and detection rules tailored to the environment in the CTEM scope. Integrations with ticketing and issue-tracking tools automate remediation workflows, and after fixes are applied, Picus re-validates exposures to confirm the mitigations work. This consistent reporting lets security teams track mobilization efforts, measure progress, and strengthen their security posture over time.
Prioritize the Exposures That Matter
Siloed approaches make it difficult to manage your threat exposure successfully.
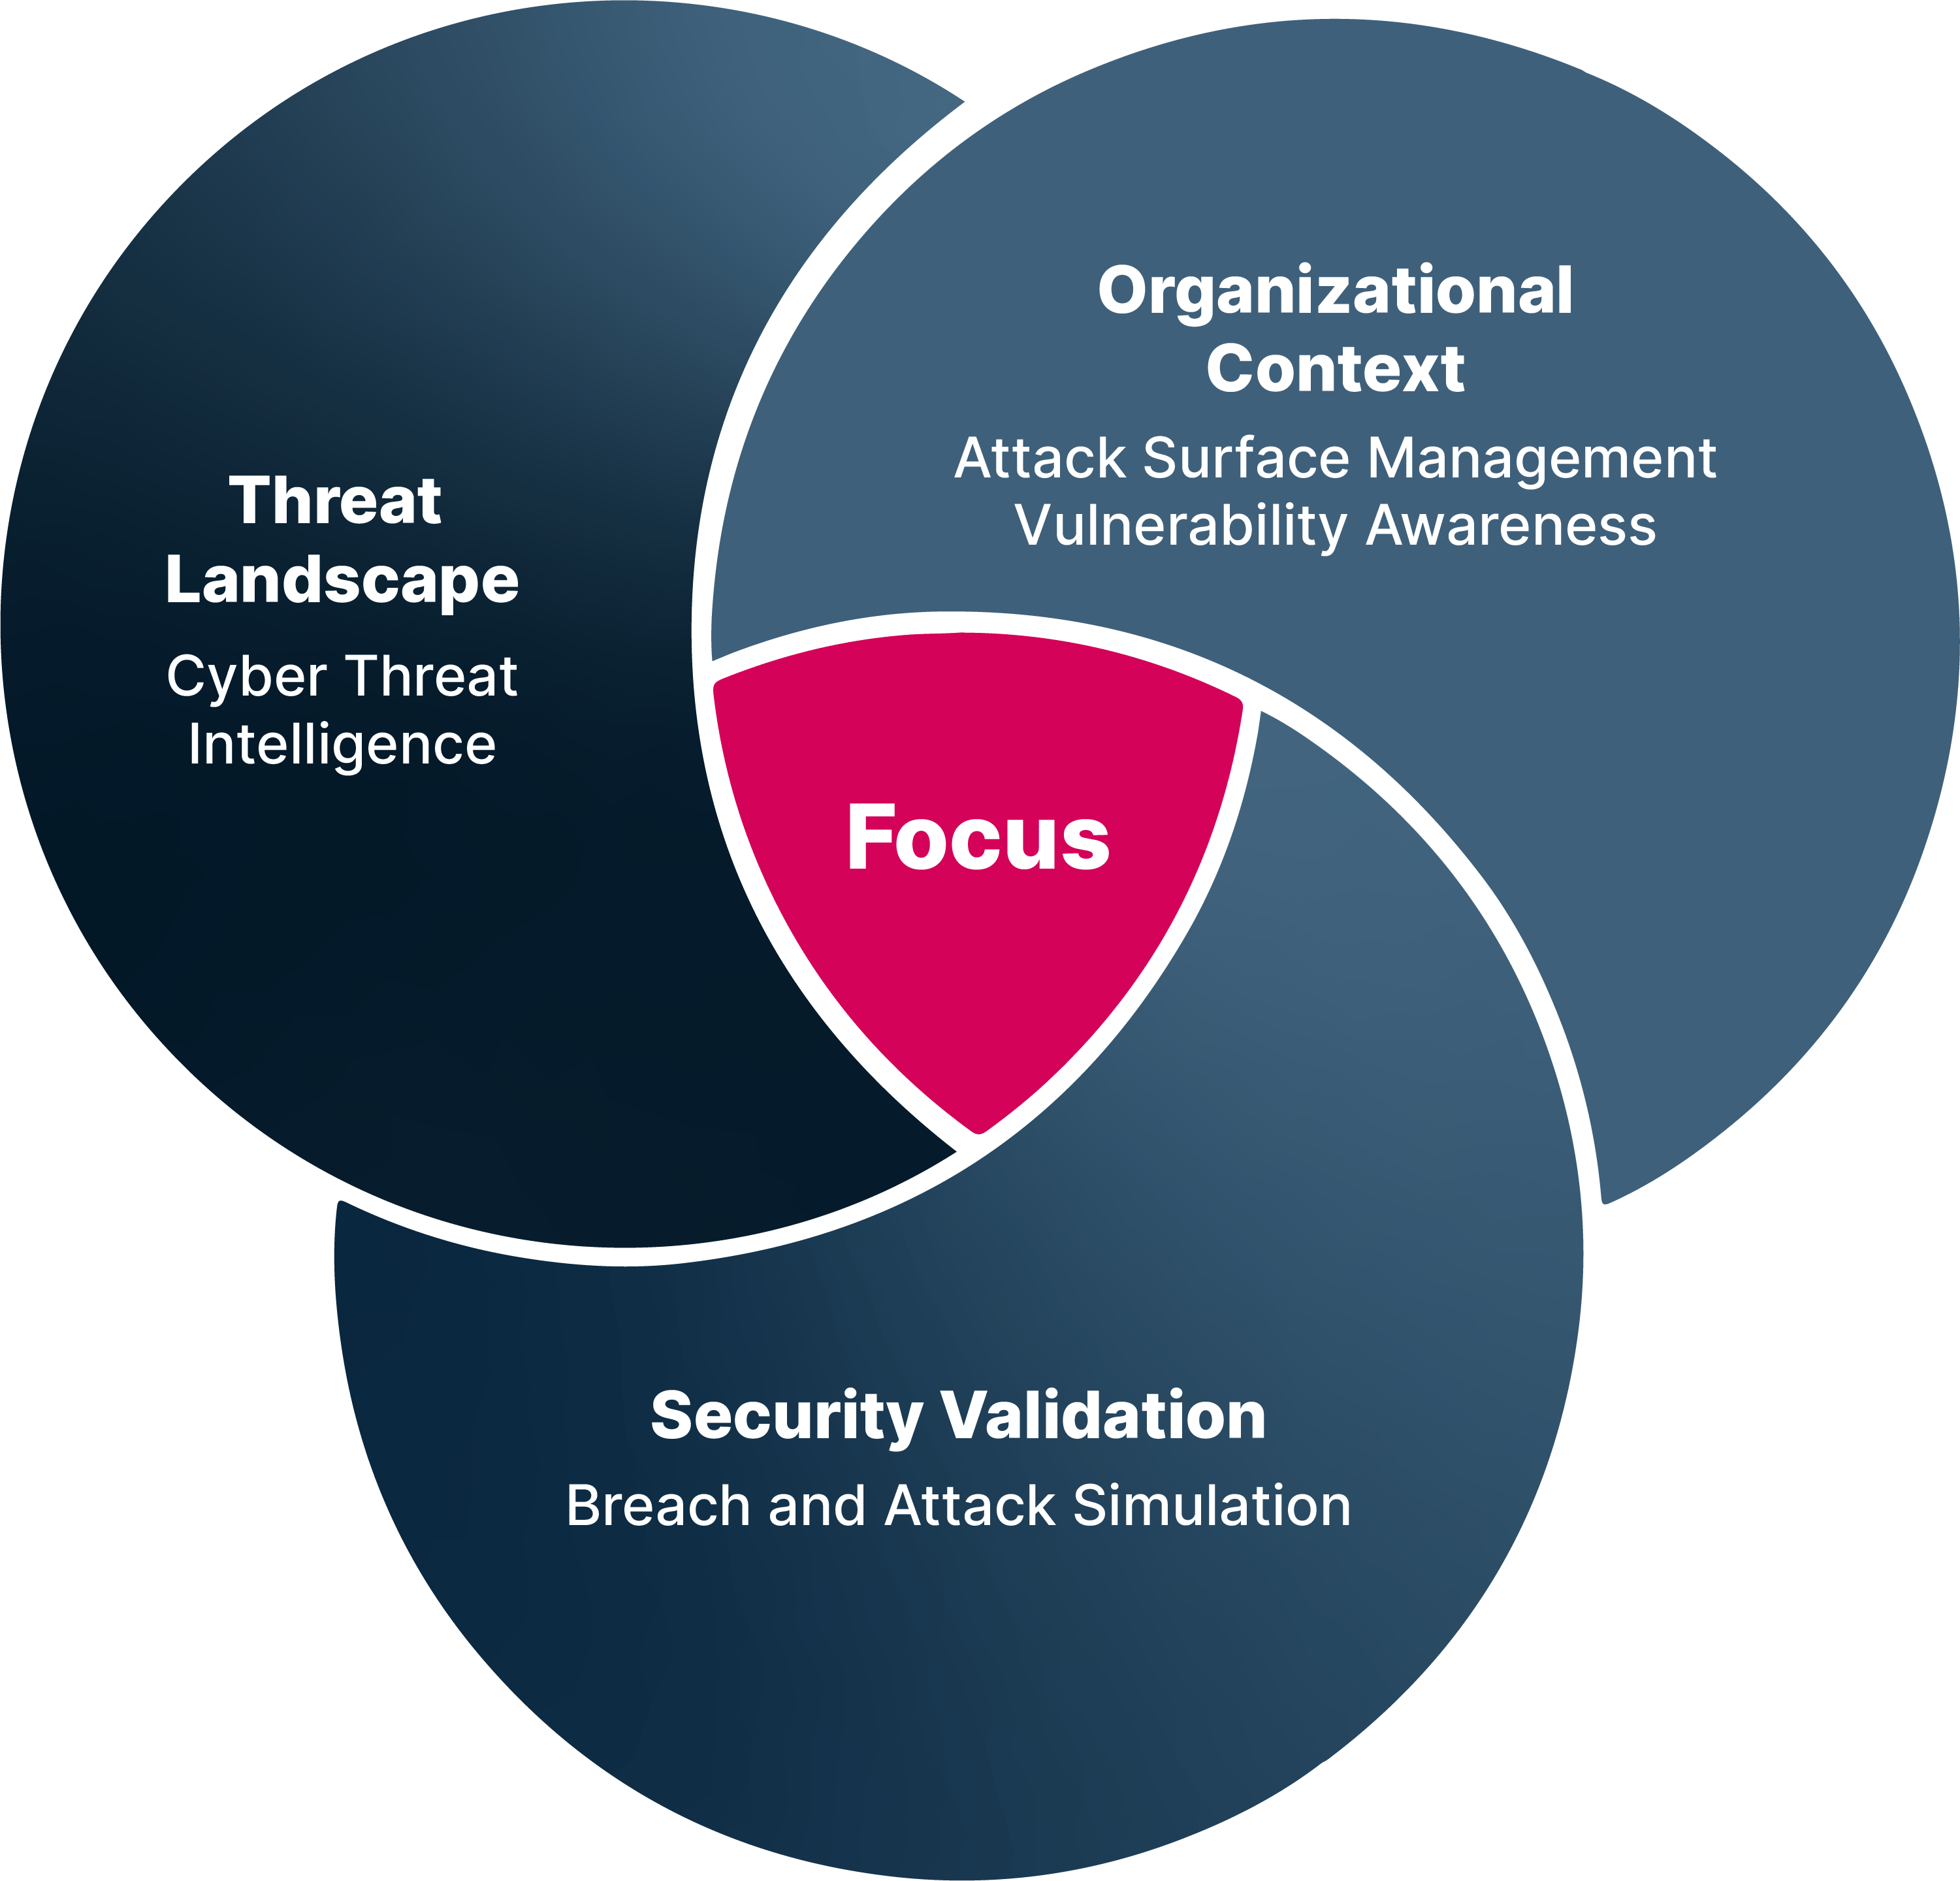
In a single platform, Picus supplies the context you need to make better security decisions across all areas of your security program.
Security validation insights, combined with data from the threat landscape and your attack surface, enable you to focus remediation and mitigation in the areas that matter.
Proof
Trusted by Security Teams, Recognized by the Industry
-
Customers' Choice
Gartner Peer Insights Voice of the Customer Adversarial Exposure Validation
-
BAS Category Leader
#1 Breach and Attack Simulation
(BAS) Solution
-
#1 Leader Frost Radar
The Innovation Leader in
Automated Security Validation
-
Outstanding Experience with Picus – A Game-Changer in Security Validation. The platform is intuitive, the reporting is clear, and the actionable insights significantly enhance our overall security posture.
Cyber Security Team Lead, Mid Market
Read more -
It allows me to test current cyber attack scenarios within my own environment, which is extremely valuable for improving our security posture.
Manager, IT Security and Risk Management, IT Services
Read more
One platform, every surface
What Picus Can Validate
Security Control Validation is one job on a platform built to validate your defenses end to end. The same evidence-driven loop extends across every surface attackers touch.
-
Security Control Validation
Simulate attacks to measure and optimize security controls.
-
Detection Rule Validation
Stay on top of exposures while alleviating manual testing requirements.
-
Adversarial Exposure Validation
Improve decision making with a holistic view of your security posture.
-
Automated Penetration Testing
Improve decision making with a holistic view of your security posture.
-
AI Security Validation
Improve decision making with a holistic view of your security posture.
-
Attack Surface Validation
Improve decision making with a holistic view of your security posture.
-
Cloud Security Validation
Improve decision making with a holistic view of your security posture.
Integrations
Unlock Your Security Stack’s Full Power
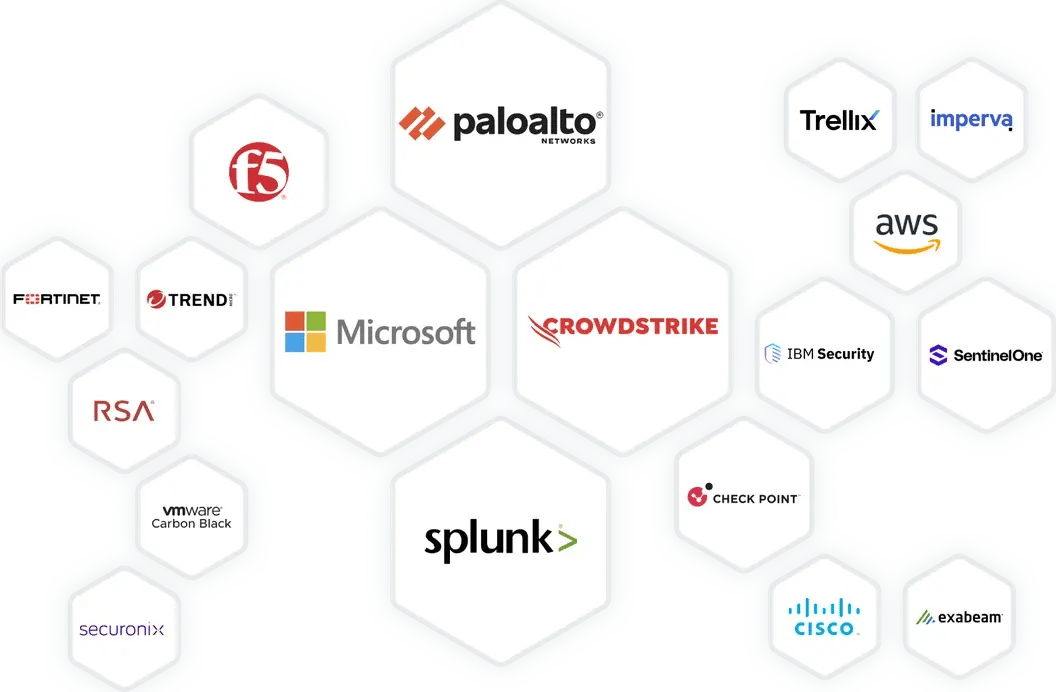
Picus integrates with the controls you already run, so simulation results turn directly into tuning and remediation.
- Identify what your NGFWs, WAFs, EDRs, SIEMs, and other security controls are missing.
- Fine-tune controls using vendor-specific and agnostic mitigation guidance and detection rules.
Resources
Latest Resources on Security Control Validation
-
Picus Security Launches Production-Safe Agentic Pentesting for Autonomous Testing and Defense
-
OWASP LLM Top 10 (2026): What Every Security Team Should Know
-
Imperial Kitten (Tortoiseshell) APT: TTPs, Malware, and Attack Simulation
FAQ
Frequently Asked Questions
About Continuous Threat Exposure Management
What is continuous threat exposure management (CTEM)?
Continuous Threat Exposure Management (CTEM) is an approach to cyber security designed to help organizations obtain the context they need to prioritize exposures and manage risks more effectively.
Practically every security and IT team needs help to keep up with essential tasks such as vulnerability management. By combining data from the threat landscape and attack surface with vulnerability and security validation insights, CTEM helps organizations determine which exposures pose the greatest risk.
Garner’s CTEM definition comprises five cycle steps: scoping, discovery, prioritization, validation, and mobilization.
What is the difference between CTEM and vulnerability management?
A traditional approach to vulnerability management involves prioritizing common vulnerabilities and exposures (CVEs) according to their CVSS score. A limitation of this approach, however, is that a severity score is not a rating that applies across all organizations - it can also be influenced by factors such as the number of assets affected, security controls coverage, and attack paths.
Continuous Threat Exposure Management helps overcome the limitations of traditional approaches to vulnerability management by facilitating a more holistic view and providing additional context to help security teams determine which exposures to prioritize.
How can I adopt a CTEM approach?
Adopting a Continuous Threat Exposure management approach can require significant time and effort. To ease the process, it’s sensible to break the process into manageable steps.
Picus recommends a four-stage process: Discover, Validate, Prioritize, Optimize. By enriching security validation insights with threat intelligence, asset data, and vulnerability insights, our platform aggregates the information required to obtain a more holistic view and helps mitigate high-risk exposures swiftly and effectively.
Why is validation a component of CTEM?
Security validation is a core component of Continuous Threat Exposure Management because it enables security teams to quantify the effectiveness of security controls and processes.
For instance, by understanding if security controls are successfully configured to protect assets by blocking the exploitation of CVEs, security teams can obtain the additional insights they need to manage risks and prioritize the remediation of vulnerabilities.
How long does a CTEM approach take to achieve?
The time it takes to adopt a Continuous Threat Management approach varies between organizations and can depend upon factors such as an organization’s existing maturity, controls, and resources.
Adopting CTEM by integrating multiple tools, such as Threat Intelligence, Attack Surface Management, Vulnerability Scanning and Breach and Attack Simulation solutions can create additional complexity and extend the adoption period by months.
For organizations that want to speed up the adoption of CTEM, unified platforms that offer broad functionality and integrate with a wide range of controls can speed up the process significantly.
See the Picus Platform
-
See Picus Run on Your Environment
In a live demo, watch Picus validate a real exposure end to end, from exploit to fix to re-test.
-
Discover the Platform
Simulate real-world cyber threats in minutes and see a holistic view of your security effectiveness.