
Prove what's exploitable, everywhere
Exposure Validation
AI has collapsed time-to-exploit from weeks to hours. Automated pentesting only tests CVEs it has an exploit for, on assets it can reach. Picus proves what's exploitable across every exposure.
- Reach what live exploits can't. Validate restricted assets, and CVEs with no safe exploit, on day one of disclosure.
- Act on real risk. Deprioritize theoretical vulnerabilities; focus on what your controls fail to block.
- Decide on evidence. Patch, Mitigate, Monitor, or Accept Risk.
Why now
Finding Exposures Is Easy. Proving the Right Call Isn't.
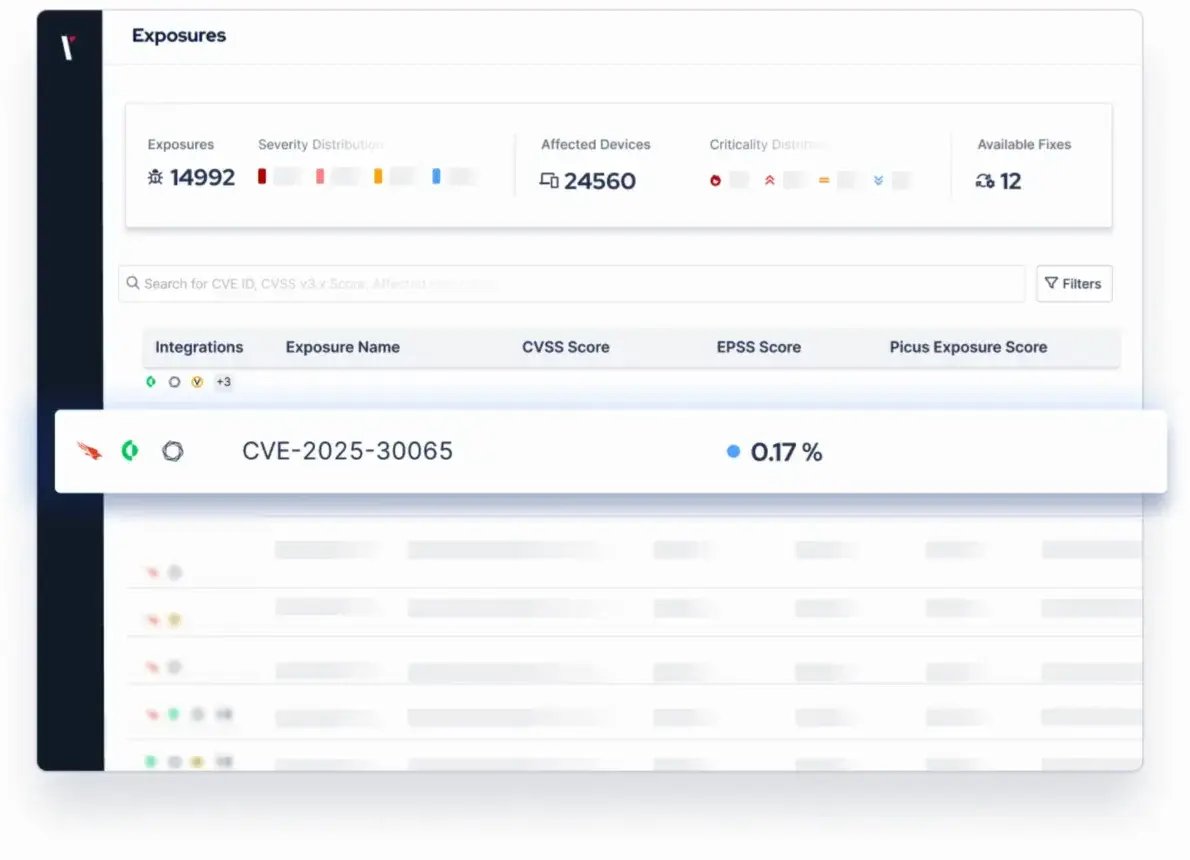
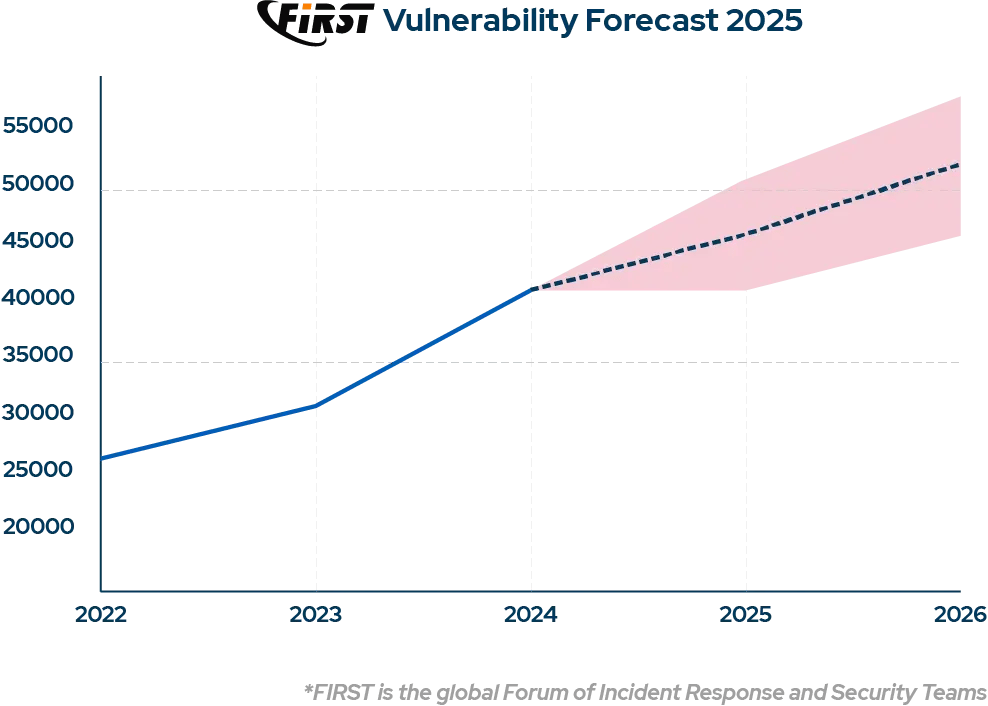
Roughly 135 new CVEs land every day, and Mythos-class AI has cut time-to-exploit from weeks to hours. Severity scores (CVSS, EPSS) can't tell you which ones are exploitable in your environment.
Finding exposures was never the hard part. Proving the right call (patch, mitigate, monitor, or accept with evidence) is.
Capabilities
Prove What's Truly Exploitable in Your Environment
Picus validates exploitability across attack surfaces, exposures, and security controls together, so you know what an attacker could actually exploit and what your defenses stop, then resolve each exposure into a defensible decision.
Coverage beyond pentest
Validate Exploitability, Even Where a Live Exploit Can't Reach
Picus combines Breach and Attack Simulation, automated pentesting, and TTP-chaining to prove which exposures are exploitable against your deployed controls.
Reachable asset with a safe exploit? Validates by execution. Restricted asset or a CVE with no exploit? Validates the TTP chain. No single pentest tool does both.
Evidence backed remediation
Decide on Evidence, Then Mobilize the Fix
Every validated exposure resolves into a defensible call: Patch, Mitigate, Monitor, or Accept with Evidence.
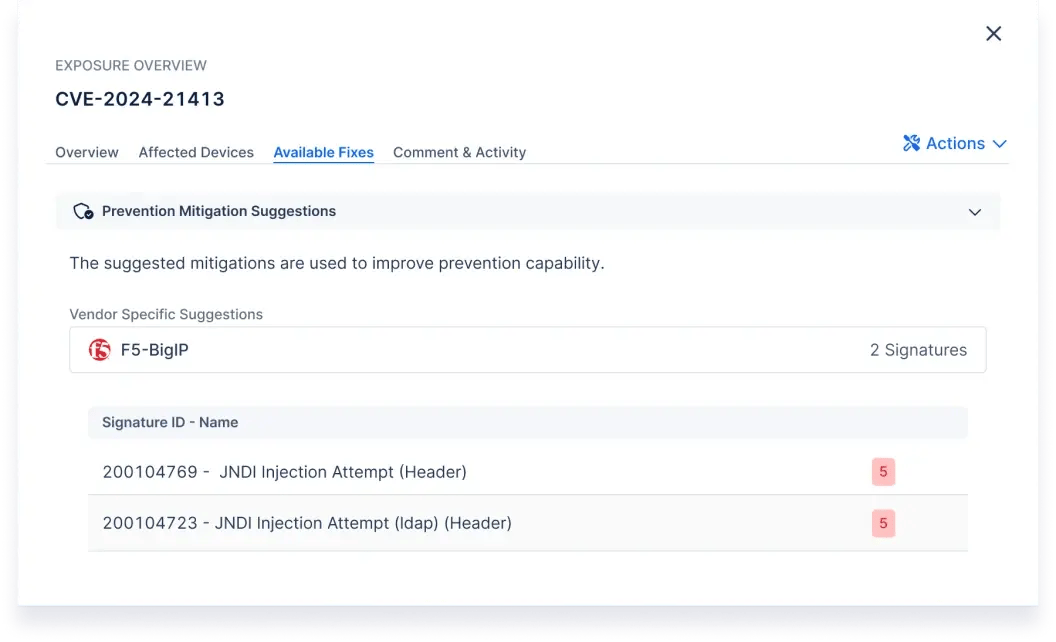
Picus delivers ready-to-apply mitigation signatures and detection rules, so you can act even when patching isn't feasible, then re-validate to prove the gap is actually closed.
Measurable risk reduction
Prioritize Real Risk, Maximize ROI
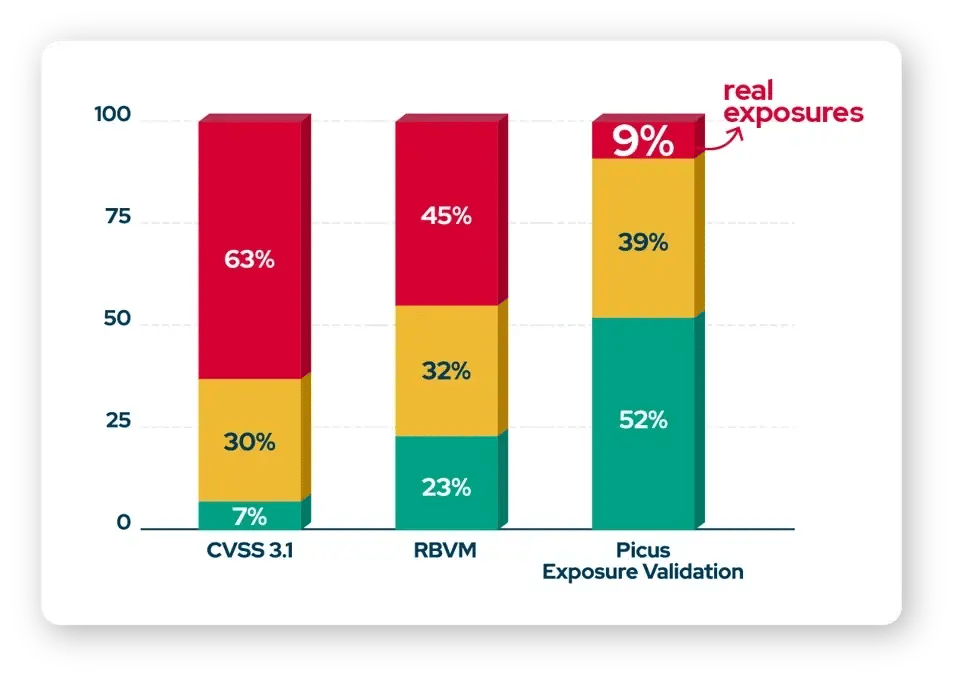
Focus on the exposures your defenses can't stop, and safely deprioritize the ones they already block, with evidence.
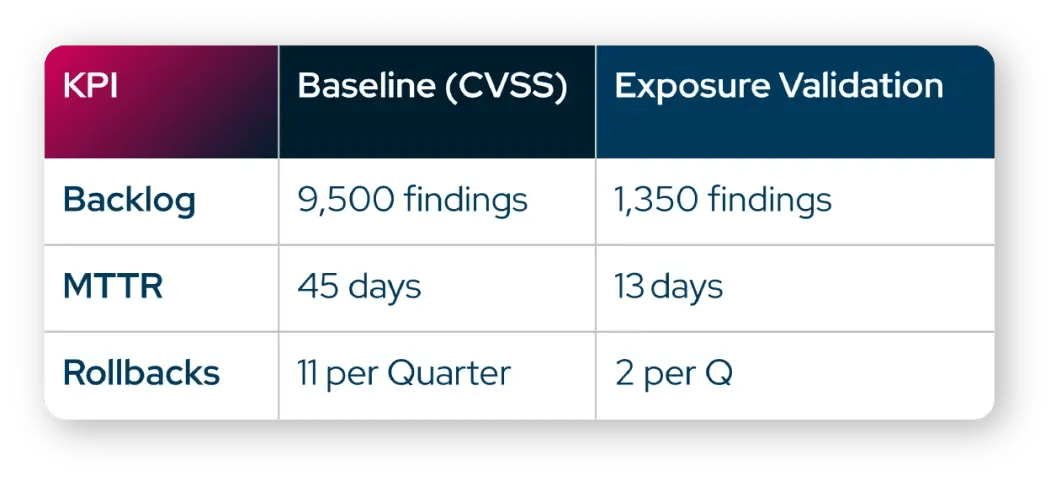
The result: faster, evidence-backed remediation, measurable risk reduction, and more value from the controls you already own.
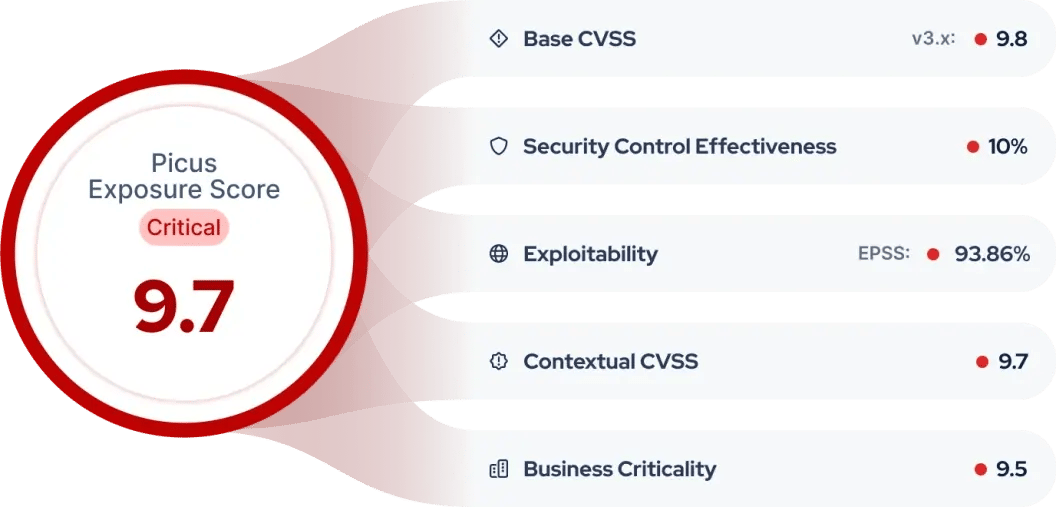
The Picus Exposure Score (PXS)
Score Real Risk, Not Theoretical Severity
Validates exploitability in your environment, answers what a CVSS or EPSS score cannot: is this exposure actually exploitable here, right now?
- Security Control Performance
How effectively your deployed defenses block or detect each exposure. - Asset Importance & Business Context
Adjusts the score by each asset's criticality and business value. - Vulnerability Severity & Exploit Availability
Factors in CVSS, plus exploit signals from EPSS, KEV, and other sources.
Exposure Validation
Three Disciplines, One Validation Loop
No single tool proves exploitability everywhere. Exposure Validation unifies three disciplines, so every exposure is validated and decided.
Breach and Attack Simulation (BAS)
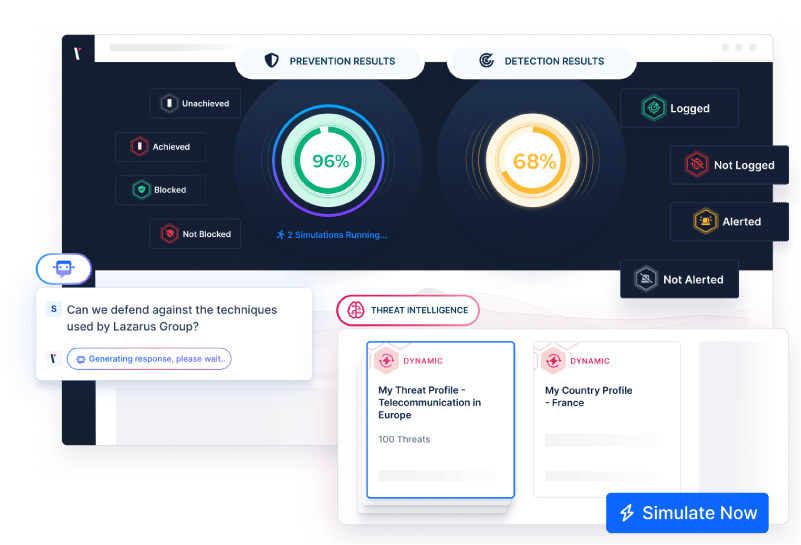
Continuously test your controls against real-world TTPs. By proving what your defenses block and what they miss, Picus BAS is the foundation that keeps every exposure decision defensible over time.
Autonomous Penetration Testing
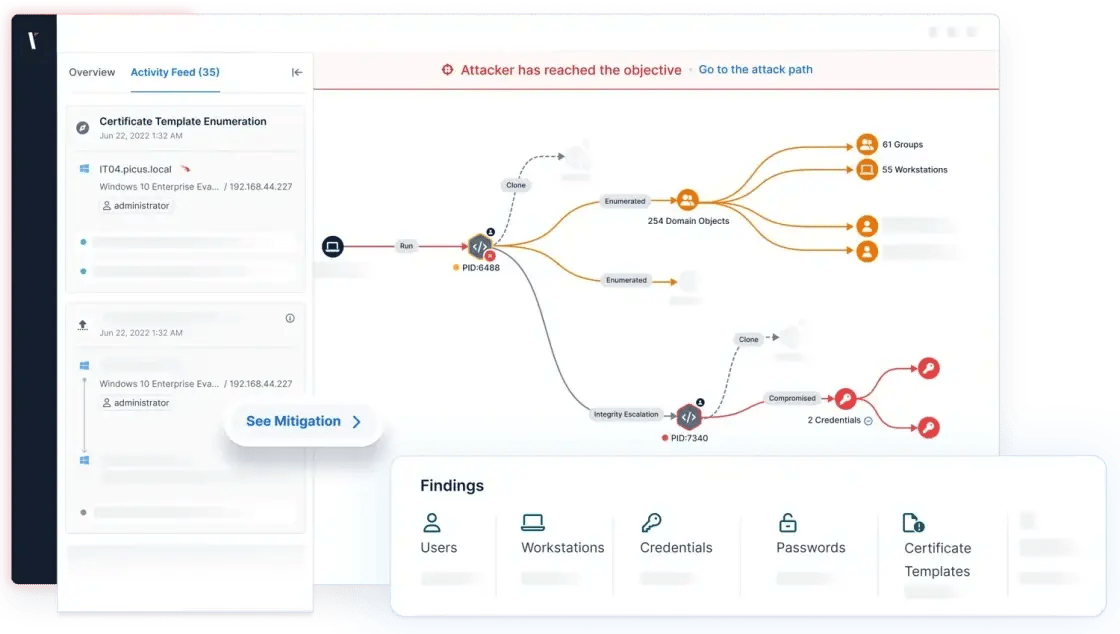
Uncover exploitable paths with Picus Autonomous Penetration Testing. It chains exposures the way an attacker would, validating exploitability by execution on the assets it can safely reach.
Attack Surface Management
Discover exposed assets with Picus Attack Surface Validation. It feeds Exposure Validation the entry points and business context that power the Picus Exposure Score.
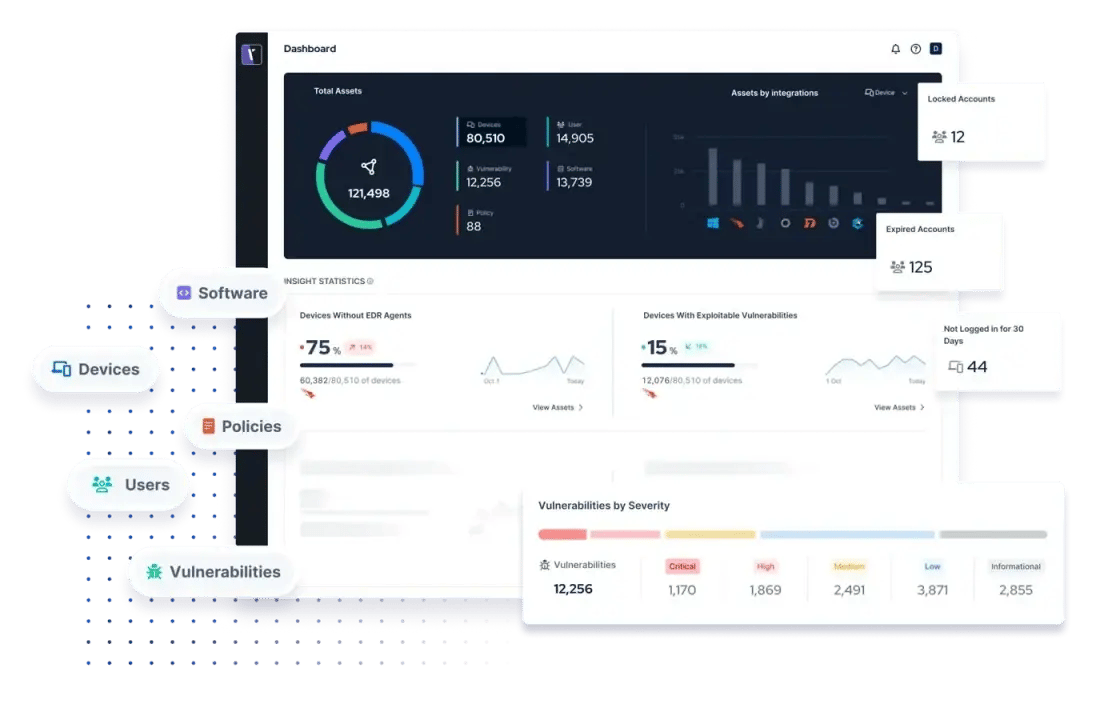
See Picus in Action
Deprioritize Theoretical Vulnerabilities
See how Picus Exposure Validation calculates real risk scores, transforming a 10.0 CVSS score to 5.2 Picus Exposure Score.
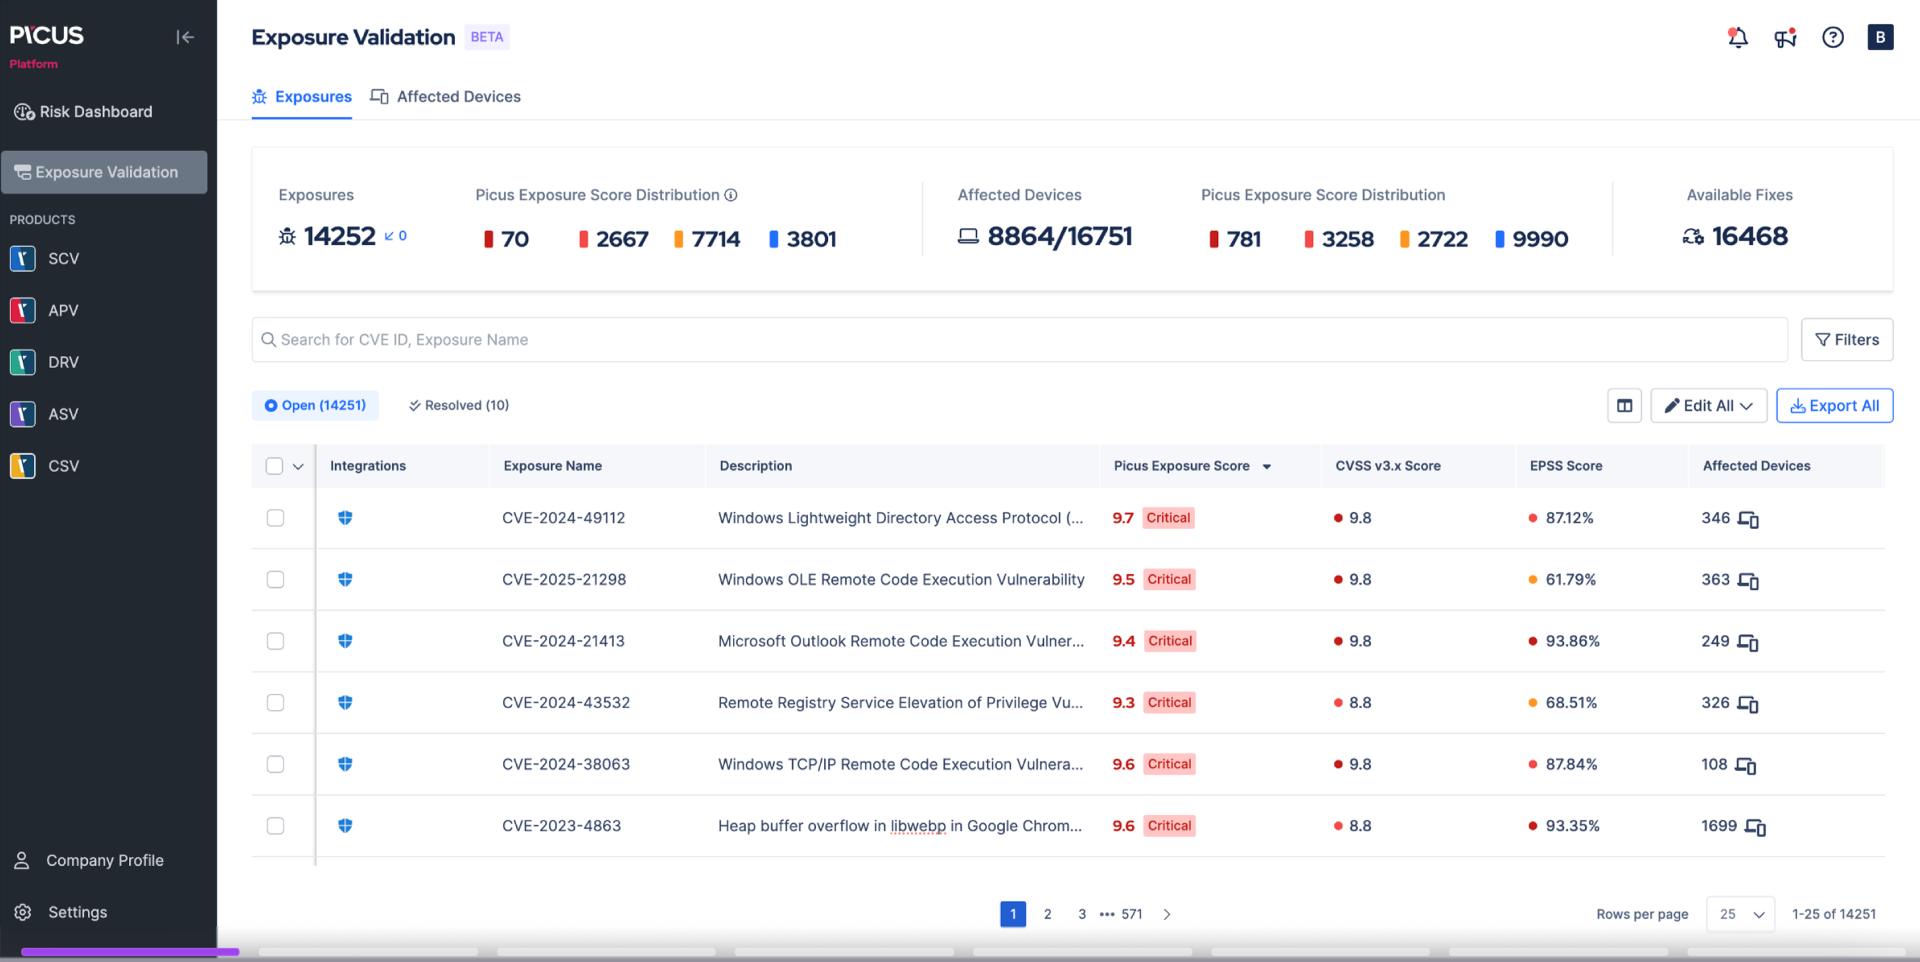

Proof
Trusted by Security Teams, Recognized by the Industry
-
Customers' Choice
Gartner Peer Insights Voice of the Customer Adversarial Exposure Validation
-
BAS Category Leader
#1 Breach and Attack Simulation
(BAS) Solution
-
#1 Leader Frost Radar
The Innovation Leader in
Automated Security Validation
-
Outstanding Experience with Picus – A Game-Changer in Security Validation. The platform is intuitive, the reporting is clear, and the actionable insights significantly enhance our overall security posture.
Cyber Security Team Lead, Mid Market
Read more -

It allows me to test current cyber attack scenarios within my own environment, which is extremely valuable for improving our security posture.
Manager, IT Security and Risk Management, IT Services
Read more
Resources
Learn More About Exposure Validation
-
Prioritize What Attackers Will Exploit: 4 Elements of Strong Exposure Prioritization
-
5 Capabilities Every Exposure Management Program Needs
-
A 2026 Gartner® Peer Insights™ Customers’ Choice for Adversarial Exposure Validation