HEALTHCARE CYBERSECURITY

Validate Cyber Readiness Across Healthcare Systems

Healthcare organizations use Picus to validate their defenses against ransomware, data breaches, and misconfigurations, helping protect patient data, ensure HIPAA compliance, and strengthen operational resilience without disruption.
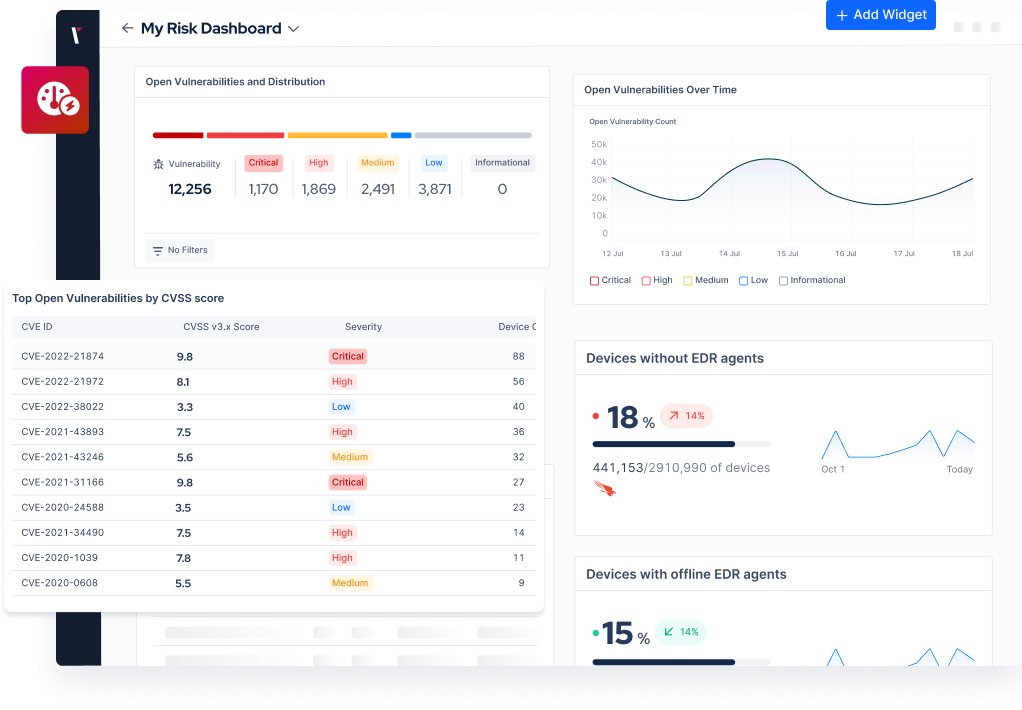
Picus platform overview

USE CASES

Protect Critical Systems withEvidence-Driven Validation

Validate how your healthcare defenses hold up against real-world attacks—like ransomware moving through your EHR network or privilege escalation via outdated medical devices. Picus helps test what matters, where it matters most.

BENEFITS

Built for The Real World Challenges of Healthcare Institutions

From ransomware simulations to validating control effectiveness and generating compliance reports, Picus helps healthcare security teams stay ahead of threats, meet regulatory demands like HIPAA and HITRUST, and focus on fixing what truly puts patient care at risk.

  • Stay Ahead of Healthcare-Targeted Threats

    Simulate ransomware, phishing, and lateral movement tailored to healthcare environments. Validate readiness across EHRs, IoT devices, and third-party portals—before attackers do.

  • Meet and Maintain Compliance with Confidence

    Get audit-ready reports aligned with HIPAA, HITRUST, and ISO 27799 and prove compliance with clear, evidence-based assurance of control effectiveness.

  • Increase Team Efficiency and Focus

    Healthcare teams are stretched thin. Automate offensive testing, prioritize the most critical exposures, and reduce wasted time chasing false positives.

  • Validate Ransomware Readiness for Healthcare Systems

    Simulate end-to-end ransomware attacks to uncover gaps in prevention, detection, and response across critical clinical systems.

  • Secure Hybrid Environments Without the Guesswork

    Whether you operate across on-prem systems, cloud services, or hybrid networks, Picus helps you identify exposures and test defenses consistently without requiring red team expertise.

  • Optimize Your Healthcare SOC with Continuous Validation

    Reduce alert fatigue and false positives by focusing on what your controls actually detect. Picus enables SOC teams to test detection logic, improve SIEM rules, and prioritize gaps based on real risk.

Compliance for Healthcare

HIPAA Compliance with Continuous Security Validation

Reduce compliance risk by validating your security controls against real-world threats. Learn how Picus helps healthcare organizations stay audit-ready and meet HIPAA requirements with confidence.
Picus integrations: Palo Alto Networks, F5, Fortinet, Trend Micro, Microsoft, CrowdStrike, RSA, VMware Carbon Black, Splunk, Securonix, Check Point, Trellix, Imperva, AWS, IBM Security, SentinelOne, Cisco and Exabeam

on demand webınar

Real-World Healthcare Security: A Pragmatic Approach to Protection and Compliance

Watch this webinar to discover a pragmatic strategy that ensures your healthcare system stays protected against modern threats while maintaining compliance and seamless clinical operations.
Healthcare Threat Templates

Simulate Cyber Threats Targeting Healthcare

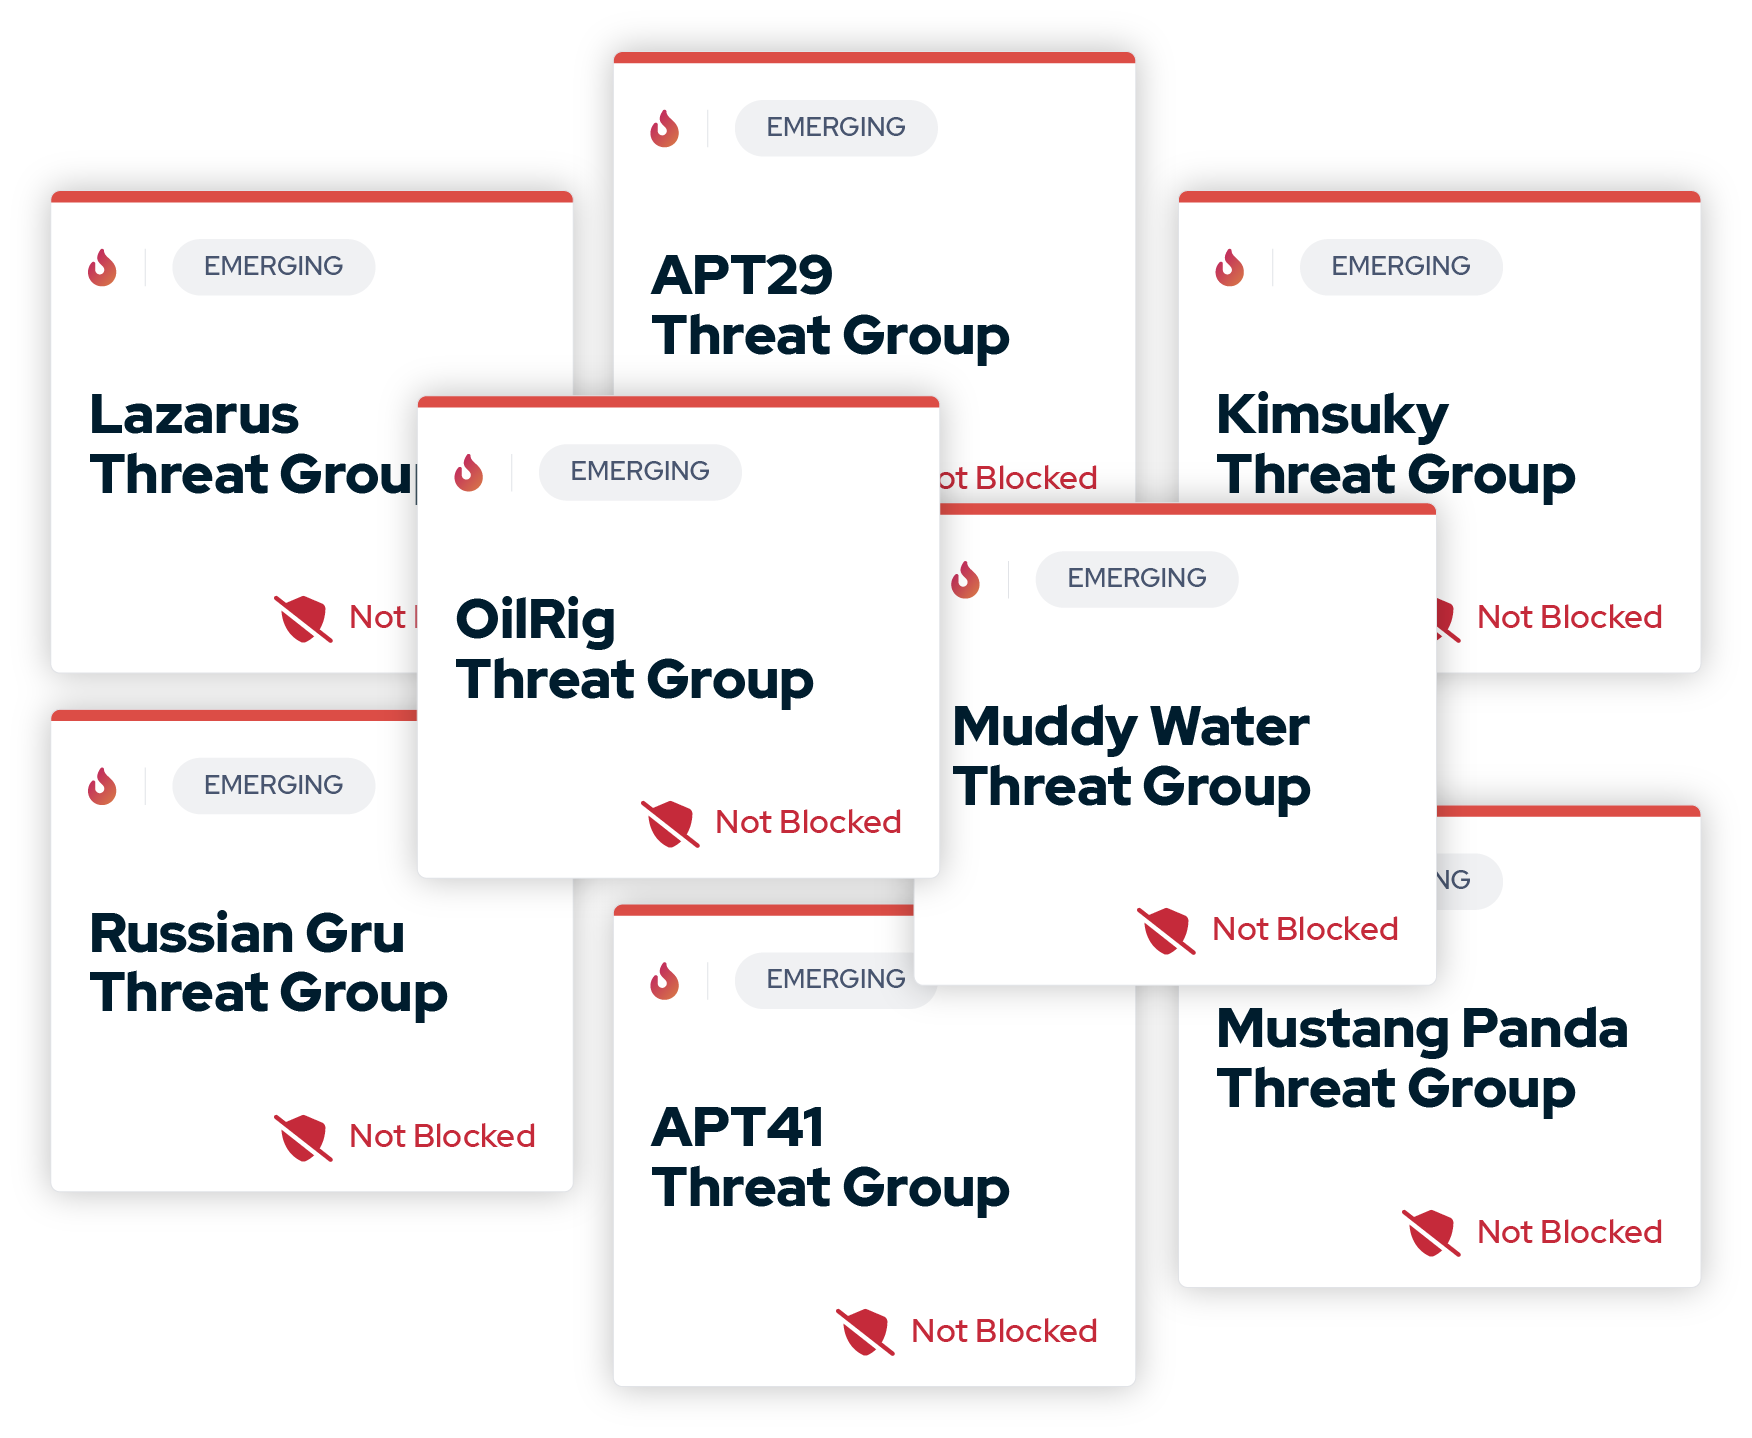
With Picus Threat Templates for Healthcare, you can validate your defenses against the latest campaigns targeting hospitals and medical systems, including TA505 ransomware, MuddyWater, and Lazarus.

Simulate real-world attacks on endpoints and networks, reveal hidden gaps, and strengthen defenses against sector-specific risks.
Picus platform overview

Who benefits

Why Healthcare Organizations Choose Picus

Security leaders across the healthcare sector trust Picus to validate their security posture safely, continuously, and at scale. Here's how Picus supports key roles across the organization: 
  • CISOs

    • Clear security posture visibility
    • Measurable control effectiveness
    • Board- and audit-ready reporting
  • SOC Managers

    • Streamline SOC operations
    • Reduce alert fatigue
    • Reliable controls against real threats
  • Compliance Officers

    • Faster audit preparation
    • Evidence-based reporting
    • HIPAA, HITRUST & ISO 27799 aligned
  • Security Analysts

    • See what’s blocked or missed
    • Hands-on control validation
    • Apply vendor-specific mitigations

CUSTOMERS

Sutter Health’s Continuous Security Validation With Picus

Sutter Health replaced manual security testing with continuous, automated validation using Picus. Real-world attack simulations reduced validation cycles from weeks to under an hour, improved visibility into control effectiveness, and supported faster remediation and HIPAA compliance.
Picus platform overview

Proof

Trusted by Security Teams, Recognized by the Industry

  • Outstanding Experience with Picus – A Game-Changer in Security Validation. The platform is intuitive, the reporting is clear, and the actionable insights significantly enhance our overall security posture.

  • It allows me to test current cyber attack scenarios within my own environment, which is extremely valuable for improving our security posture.

Resources

Stay Informed with Picus Healthcare Blogs

  • Healthcare Cybersecurity: 2026 Performance in Healthcare and Pharmaceuticals

    Healthcare Cybersecurity: 2026 Performance in Healthcare and Pharmaceuticals

  • Istanbul Sabiha Gokcen International Airport (ISG) Transforms Critical Infrastructure Security with Picus

    Istanbul Sabiha Gokcen International Airport (ISG) Transforms Critical Infrastructure Security with Picus

  • How an Enterprise Software Company Separates Real Risk from Theoretical Risk with Picus

    How an Enterprise Software Company Separates Real Risk from Theoretical Risk with Picus

FAQ

Frequently Asked Questions

About Healthcare Organizations

What are the main cybersecurity risks healthcare organizations should validate against?

Healthcare organizations face significant cybersecurity threats, including ransomware attacks, advanced persistent threats (APTs), phishing, insider threats, unpatched vulnerabilities in legacy systems, cloud misconfigurations, and supply chain exploits. Due to the high value of patient data and life-critical systems involved, these risks must be continuously validated through proactive testing such as Breach and Attack Simulation (BAS) and Automated Penetration Testing. This validation ensures security controls effectively protect against real-world threats.

How impactful is a ransomware incident for healthcare organizations?

Ransomware incidents can have devastating effects on healthcare organizations, disrupting patient care, compromising life-saving operations, and causing severe financial losses. Beyond operational disruption, attackers often demand substantial ransoms and threaten to leak sensitive patient data, risking patient safety and trust. On average, healthcare breaches cost around $10.93 million, reflecting the industry's vulnerability. Continuous validation helps mitigate these impacts by identifying weaknesses before attackers do, ensuring faster response and recovery.

How can healthcare organizations stay compliant?

Continuous validation of security controls is critical for healthcare organizations to maintain compliance with regulations such as HIPAA, HITECH, GDPR, ISO 27799, and HITRUST CSF. Traditional periodic assessments often miss evolving threats. Leveraging automated and continuous validation platforms like Picus, healthcare organizations can demonstrate consistent adherence to regulatory requirements. By continuously testing defenses and promptly addressing identified gaps, compliance becomes proactive rather than reactive, helping healthcare providers meet stringent standards while safeguarding patient data.

How can healthcare SOC teams improve visibility and reduce alert fatigue?

Many healthcare SOCs struggle with overwhelming alert volumes and false positive alerts. This often leads to alert fatigue, missed threats, and reduced response speed. By continuously validating detection rules and simulating real-world attacks, teams can identify what their tools are catching and what they're missing. Platforms like Picus help optimize SIEM and EDR configurations, reduce false positives, and ensure that analysts are focused on real threats, not noise.

What makes Breach and Attack Simulation (BAS) valuable for healthcare organizations?

BAS allows healthcare organizations to safely simulate attacker techniques used in real-world campaigns, such as ransomware, credential theft, and lateral movement. Unlike one-off assessments, BAS is continuous, automated, and tailored to your environment. It helps validate that security controls are working as expected, identifies prevention and detection gaps, and enables teams to apply mitigation measures with confidence without disrupting critical workflows.

Can Picus help with validating ransomware readiness?

Yes. Picus simulates ransomware behaviors from initial infection to encryption and data exfiltration, allowing healthcare organizations to assess their defenses across the kill chain. This includes validating endpoint protection, email gateways, segmentation, and detection workflows. With visibility into what techniques are detected or blocked, teams can proactively close gaps, reduce dwell time, and strengthen preparedness against high-impact ransomware threats.

See the Picus Platform

  • See Picus Run on Your Environment

    In a live demo, watch Picus validate a real exposure end to end, from exploit to fix to re-test.

  • Discover the Platform

    Simulate real-world cyber threats in minutes and see a holistic view of your security effectiveness.