Attack Surface Validation

Know every asset attackers can reach,and the risk each one carries.

Bring your assets, users, software, policies, and vulnerabilities into one continuously updated view, enriched with validation evidence, so you can prioritize by real risk instead of a scanner's severity score.

attack-surface-validation

What is Attack Surface Validation?

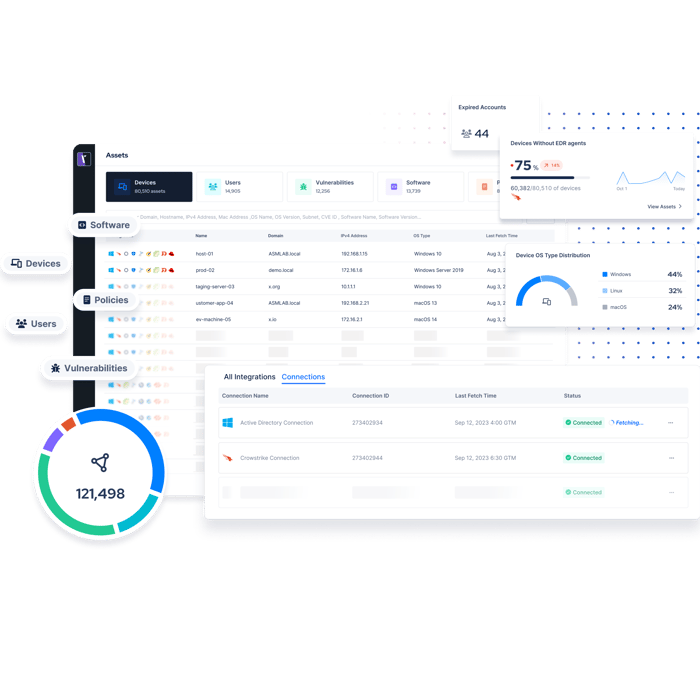
Attack Surface Validation pulls asset and vulnerability data from the tools you already run into one continuously updated view of your internal and external attack surface. No new scanner: it consolidates what your environment already produces into a single asset library.

As part of the Picus Autonomous Exposure Validation Platform, that view is enriched with validation evidence, so every asset is understood in the context of what an attacker could do with it.

Exploitable, not just present

Every asset is enriched with validation evidence, so remediation targets what an attacker could truly exploit.

Covered, not just catalogued

Discovery says an asset exists; it can't say the agent is missing or a policy went unenforced. Validation finds those gaps.

One count, not five

When teams report different device totals, no one can act with confidence. One consolidated view ends the reconciliation.

THE PROBLEM

The assets that hurt you are already in your inventory.
No one has validated them.

Traditional attack surface management finds and counts assets. It tells you what you have, not whether an exposure is exploitable, whether an asset is defended, or which finding to fix first. Discovery is table stakes. The risk lives in what happens after the list.

Severity ≠ Risk

A longer list is not a shorter risk.

Discovery ranks findings by generic severity and hands you thousands of them. Without knowing what an attacker could actually exploit here, prioritization stays guesswork, just with more rows.

Coverage Gaps

Catalogued does not mean covered.

An asset can sit in your inventory while its security agent is missing, its policy goes unenforced, or no scanner has ever reached it. Discovery confirms the asset exists. It can't confirm it's defended.

Fragmented Data

Counts that never reconcile.

Every tool sees only part of the environment, so the EDR, the CMDB, and the SIEM each report a different total. Reconciling them by hand is slow, and the number is stale the moment it's finished.

the solution

Discovery finds the assets.
Validation tells you which ones an attacker can exploit.

Picus Attack Surface Validation consolidates asset and vulnerability data from the tools you already run into one continuously updated view, then goes where discovery stops. As part of the Picus Autonomous Exposure Validation Platform, every asset is enriched with validation evidence, so you don't just see what you have, you know what's exploitable, what's actually defended, and what to fix first.

ASSET INVENTORY

Discover and catalog every digital asset in your environment.

Automatically identify and classify devices, users, software, policies, and vulnerabilities across internal and external assets, then keep that inventory current as the environment changes. Map it visually, segment it by business scope, and get a reliable answer to "what do we have?"

Powered by seamless integrations across Active Directory, endpoint detection, config management, vulnerability management, and external attack surface tools.
overcome-asv
Image_1_risklevel
ENDPOINT SECURITY HYGIENE

Confirm every endpoint is actually covered by the controls you deployed.

Check endpoints against your security policies, verify that necessary controls are present and healthy, and surface agents that are missing, offline, misconfigured, or out of date. Instead of assuming coverage, you prove it, and find the gaps before an attacker does.

Powered by continuous monitoring of agent status, policy enforcement, and endpoint security management services.
VULNERABILITY DISCOVERY & PRIORITIZATION

Focus remediation on the exposures that carry real risk.

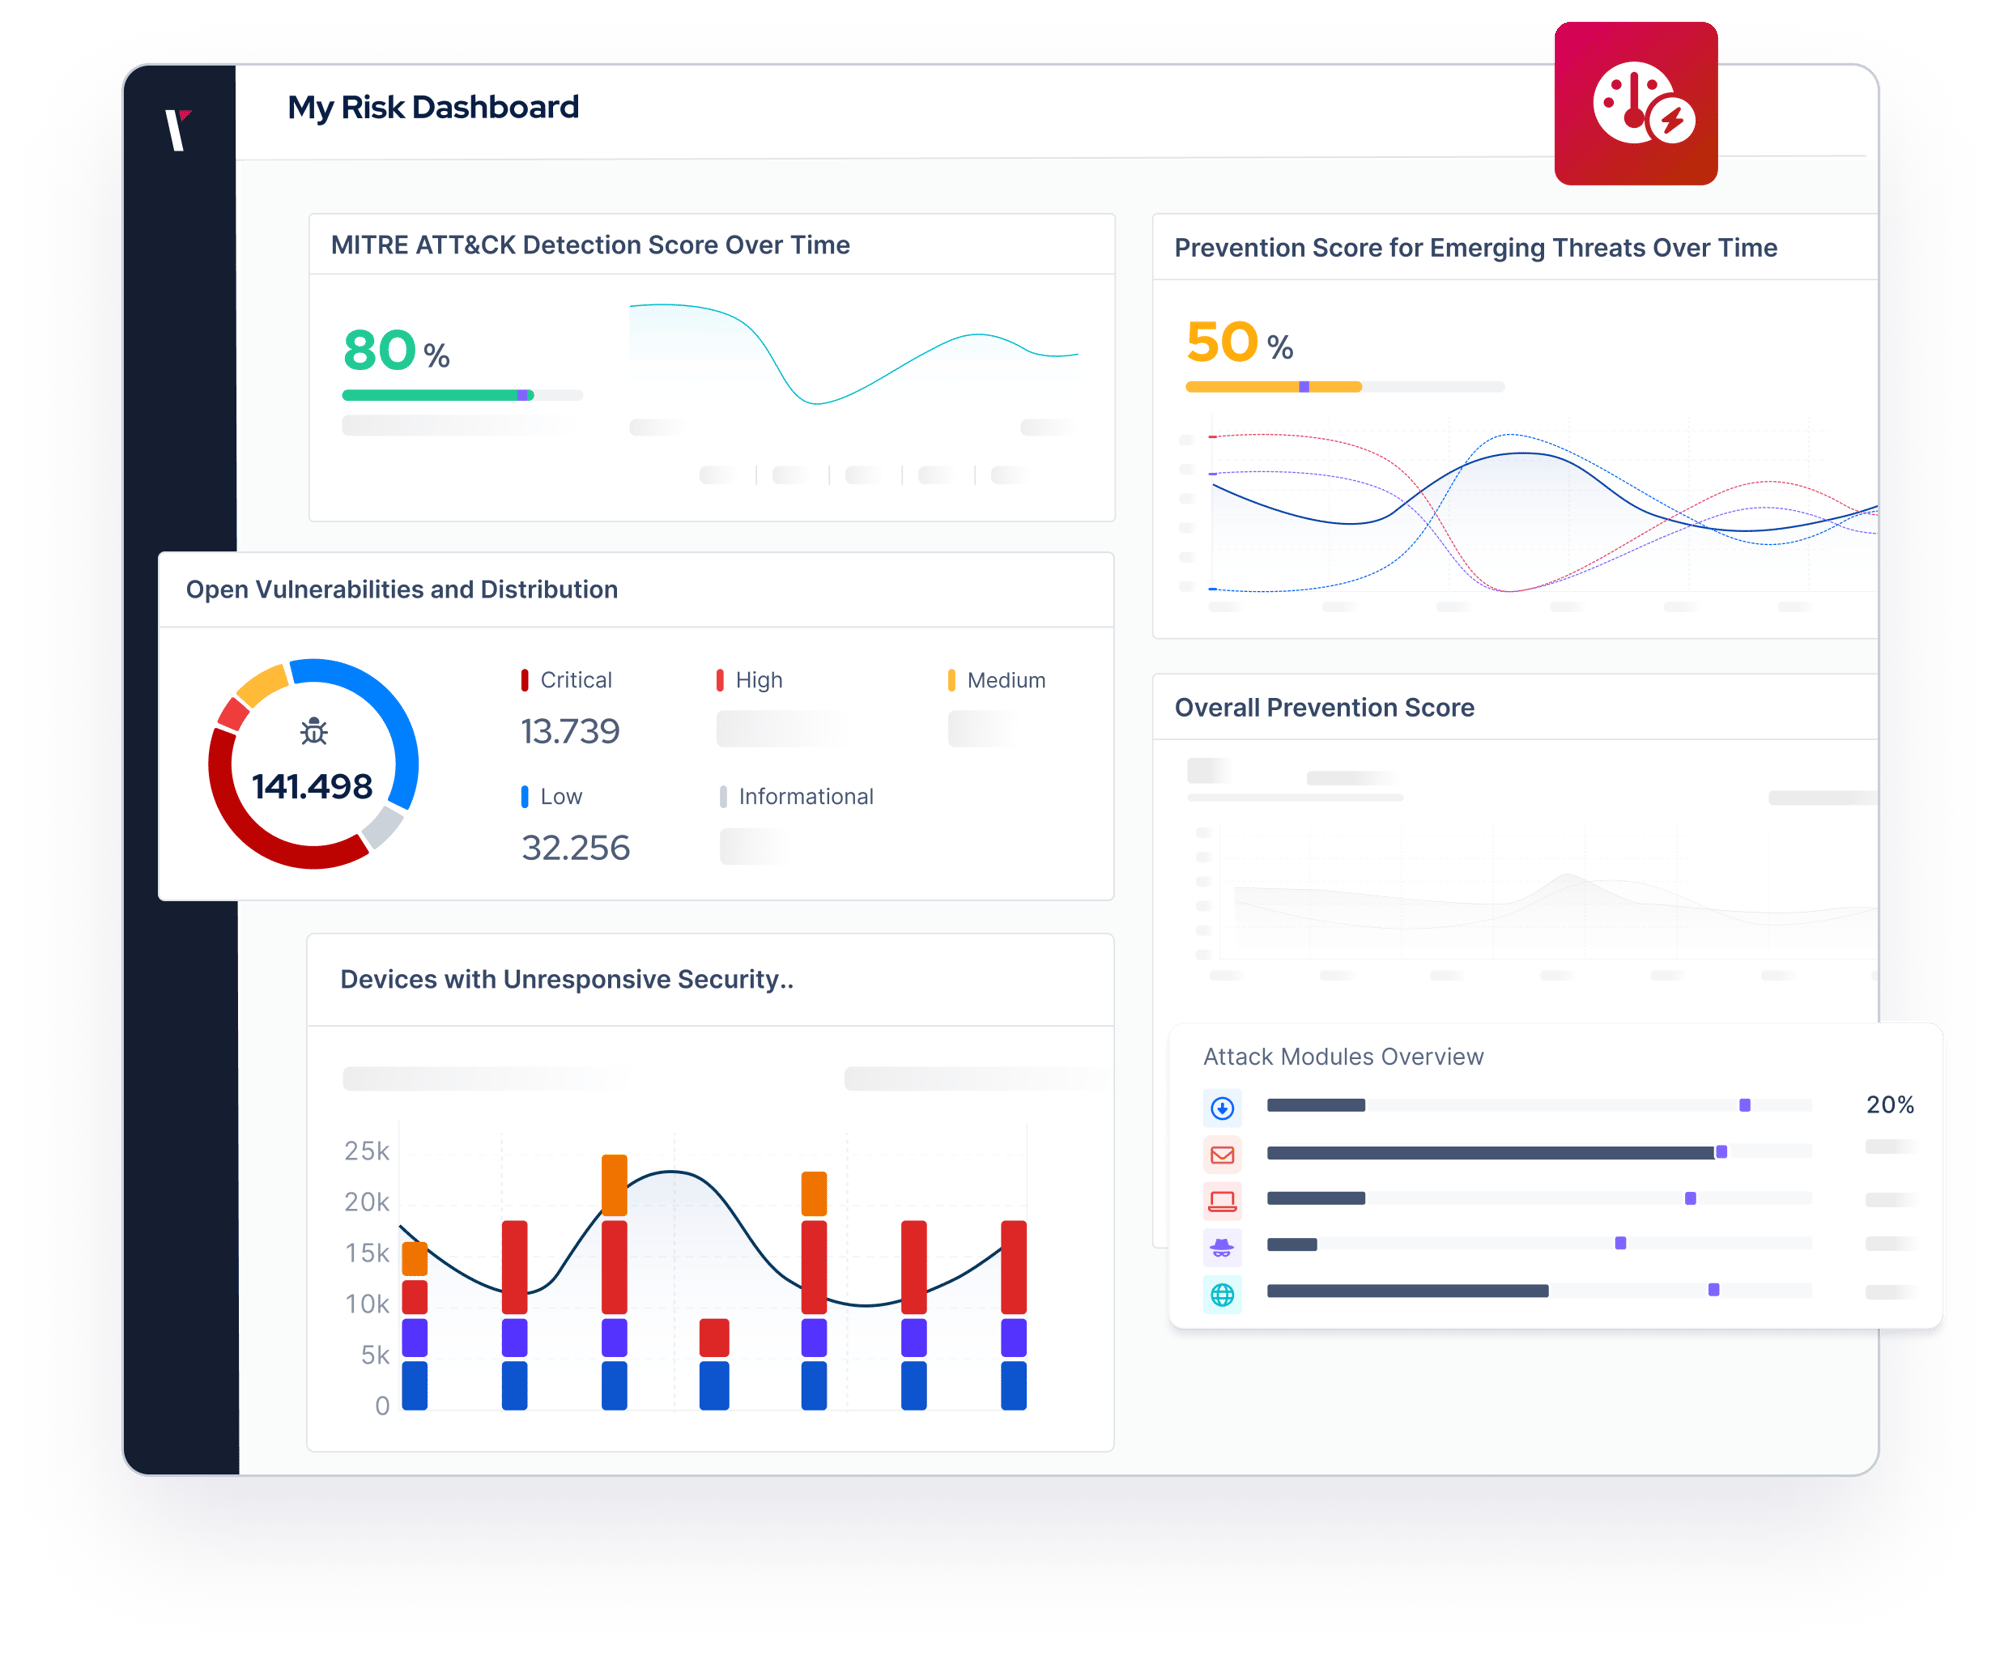
Consolidate vulnerability data from every source into a single view, then prioritize with the Picus Asset Score rather than a flat severity number. Findings are enriched with validation evidence and tied to next steps, so you act on what is genuinely exploitable in your environment.

Powered by unified vulnerability visibility, the Picus Asset Score, and validation evidence from the Picus Platform.
undefined-Jun-29-2026-01-39-42-7086-PM
reporting dashboard full-1
RISK-BASED VISUALIZATION

See the whole environment, then zoom to what carries the most risk.

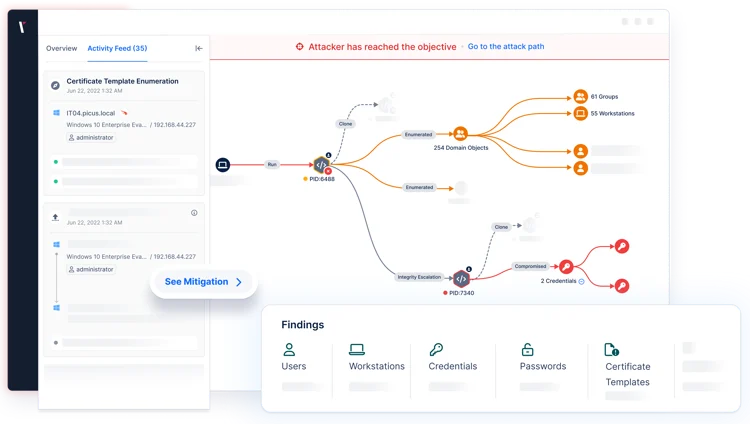
Map your attack surface as a live topology, grouped by operating system or by the business scopes that matter to you, with the Picus Asset Score rolled up per group. An Estimated Financial Impact translates that risk into dollars, so security and the business are looking at the same picture and the same priorities.

Powered by the Organization Map, business scopes, the Picus Asset Score, and estimated financial impact from validation.
HOW IT WORKS

From scattered data to a decision-ready view.

Attack Surface Validation turns the data your tools already produce into one continuous, validated picture of your attack surface.

  1. Step 1: Aggregate

    Integrate with the sources across your environment to pull in assets and their context automatically.

  2. Step 2: Discover

    Identify and catalog every device, user, software instance, policy, and vulnerability, internal and external.

  3. Step 3: Enrich

    Score every asset with the Picus Asset Score and validation evidence from the Picus Platform.

  4. Step 4: Prioritize

    Rank exposures by real risk, factoring in exploitability, control coverage, and business criticality.

  5. Step 5: Act

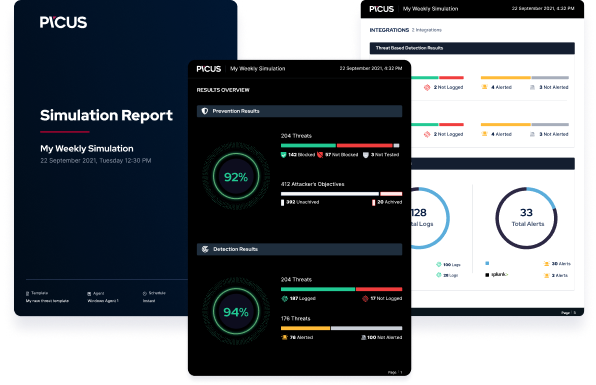
    Move straight to next steps: analyze exposures, review the score, or run a simulation to validate controls

WHO BENEFITS

Value for every team.

SOC & Blue Teams

  • Faster context during investigations.
  • One reliable asset picture.
  • Early warning on coverage gaps.

Security Engineers

  • Spot endpoints missing controls.
  • Catch policy and config drift.
  • Verify agent health at scale.

Vulnerability Management

  • Unified vulnerability visibility.
  • Risk-based prioritization.
  • Assets no scanner has reached.

CISO / Risk

  • One source of truth for the estate.
  • Estimated financial impact of risk.
  • Defensible resource allocation.
INTEGRATIONS

Built on the tools you already run.

Picus aggregates asset and exposure data from a wide range of sources, so validation runs on your real environment, not a partial copy.

Active Directory
EPP
Vulnerability Management
Endpoint & Config Management
External ASM
WHAT CUSTOMERS SAY
Trusted by Security Teams, Recognized by the Industry
mid-strip-gray-mobile mid-strip-gray

gartner-logo-2025 1 (1)

Customer's Choice

Gartner Peer Insights Voice of the Customer Adversarial Exposure Validation

mid-strip-gray-mobile mid-strip-gray

2026-G2-summer-dark

BAS Category Leader

Ranked #1 by Users on G2

mid-strip-gray-mobile mid-strip-gray

frost-radar-leader-badge-2026 (1) (1)

#1 Leader Frost Radar

Automated Security Validation

THE PICUS PLATFORM

One platform validates your whole security program.

Attack Surface Validation is one capability on the Picus Autonomous Exposure Validation Platform. Together, these capabilities converge into one continuous validation loop, from attack surface to exposures to controls.

Breach and Attack Simulation
Continuously tests what your EDR, SIEM, firewall, WAF, and other security controls actually block and detect against the newest attacker techniques, then ships the fixes and re-validates that the gap closed.
Autonomous Pentesting
Executes real exploit chains in your environment, showing what an attacker can actually reach and do, not what a CVSS or EPSS score predicts. Live validation, run safely in production.
Exposure Validation
Proves exploitability without firing an exploit, covering the restricted assets no live test can touch and the CVEs with no public or safe exploit, for a defensible verdict on day one of disclosure.
mid-strip-gray-mobile mid-strip-gray
WHAT SETS PICUS APART

Other tools discover your attack surface.
Picus tells you what an attacker can actually do with it.

Validation, not just discovery

Traditional attack surface management stops at a list ranked by generic severity. Picus enriches every asset with validation evidence, so you know which exposures are truly exploitable in your environment and which are already contained by your controls.

One score that reflects real risk

The Picus Asset Score combines security control effectiveness, exploitability, contextual CVSS, and business criticality into a single measure. A critical finding on a defended asset drops down the list; a moderate one on an exposed, business-critical asset rises to the top.

Part of one platform

Attack Surface Validation feeds a continuous loop on the Picus Autonomous Exposure Validation Platform. The same platform runs breach and attack simulation, autonomous penetration testing, and exposure validation, so a finding becomes a defensible decision.

See the Picus Platform

Pattern-mobile Pattern(1)

See Picus run on your environment

In a live demo, watch Picus validate a real exposure end to end, from exploit to fix to re-test.

Discover the Platform

Simulate real-world cyber threats in minutes and see a holistic view of your security effectiveness.

Frequently Asked Questions

An attack surface is the full set of points an attacker could use to breach or impact an organization. It includes external assets like internet-facing websites, applications, and cloud workloads, and the internal attack surface of users, hosts, systems, and applications inside your networks.

Attack Surface Validation is the continuous process of discovering, classifying, and assessing every internal and external asset, then aggregating what your tools know about each into one risk-ranked view. It moves you from a flat inventory to a prioritized picture of what actually needs defending, backed by attack-simulation evidence.

You can only protect what you can see. Environments change daily through cloud migration, new applications, and shadow IT, so an attack surface shifts constantly. Continuous validation keeps visibility current so teams can prioritize protection and respond to risk quickly.

Yes. Picus Attack Surface Validation is a Cyber Asset Attack Surface Management (CAASM) tool that integrates with a wide range of data sources for internal and external asset visibility, and can integrate with External Attack Surface Management (EASM) tools to extend external coverage.

Yes. The Picus Platform is SOC 2 Type 2 compliant. You can request a copy of the report from Picus.