Security teams evaluating or already using Pentera are increasingly looking for platforms that deliver broader security control validation, faster emerging threat updates, dedicated detection engineering, and richer remediation guidance across the entire attack kill chain within a unified platform.
Based on publicly available customer feedback from peer review and ratings platforms and competitive analysis, the two strongest alternatives to Pentera today are:
- Picus Security, the pioneer of Breach and Attack Simulation and a leader in Adversarial Exposure Validation
- Horizon3, maker of the NodeZero automated pentesting platform
This blog provides a concise breakdown of each option and why modern teams are choosing them over Pentera in 2026.
The Top Alternatives to Pentera in 2026
-
Picus Security
Picus Security stands out as the leading alternative to Pentera for Breach and Attack Simulation (BAS), Adversarial Exposure Validation (AEV), Automated Penetration Testing, and Continuous Threat Exposure Management (CTEM).
Picus offers a unified security validation platform that simulates real world attacks to prove how well defenses actually detect and block threats, prioritizes only truly exploitable business critical risk, and delivers precise, actionable remediation. The platform answers a question Pentera leaves partially open. Not just where can an attacker go, but are an organization's security controls (firewalls, EDRs, SIEMs, email gateways, WAFs) actually capable of stopping a real breach.
Picus Platform stands out in these ways.
- Comprehensive BAS plus Exposure Validation across email, web, endpoint, network, data, and cloud, ensuring full attack coverage with 30,000+ adversary actions fully mapped to MITRE ATT&CK.
- Vendor specific prevention and detection content with 80,000+ ready to implement signatures for security controls such as NGFW, IPS, and WAF, and 4,400+ validated detection rules for major SIEM and EDR platforms. Picus also provides log source recommendations to enhance visibility and improve SIEM efficiency.
- Picus Labs threat research division delivers a guaranteed 24 hour SLA for emerging threats, with a measured mean time to release of 5.3 hours, the fastest in the market.
- Attack Path Validation (APV), Picus' automated pentesting solution, identifies and prioritizes the shortest, most exploitable attack paths using techniques such as credential harvesting, Kerberoasting, lateral movement, privilege escalation, and data exfiltration, executed in an evasive manner designed to avoid premature detection.
- Numi AI, an AI powered virtual security analyst that translates complex findings into natural language recommendations, prioritized actions, automated playbooks, and tickets teams can execute immediately.
- Flexible deployment including on premises, cloud, hybrid, and air gapped environments managed from a single centralized console, an option that pure SaaS alternatives cannot offer.
Picus Security vs Pentera: Key Differences
|
Category |
Picus Security |
Pentera |
|
Primary Use Case |
Best in class BAS + Attack Path Validation (Automated Penetration Testing) + ASM + Exposure Validation + Automated Mitigation + Detection Analytics & Engineering |
Automated internal penetration testing with EASM |
|
Threat Library Transparency |
Transparent, continuously updated library with full MITRE ATT&CK mapping |
Operates as a black box with limited visibility into what is being tested and why |
|
Detection Engineering |
Automated SIEM rule validation, log source health checks, vendor specific detection content, and detection rule hygiene analysis |
No detection analytics. Users must manually export action logs and cross reference against SIEM logs |
|
Emerging Threat SLA |
24 hour SLA with measured 5.3 hour mean time to release |
Updates deployed every 4 to 6 weeks. No publicly defined SLA. |
|
Remediation Guidance |
80,000+ vendor specific prevention signatures and 4,400+ validated detection rules ready for immediate deployment |
Remediation Wiki provides directional guidance only. No vendor specific signatures |
|
Email and Email Gateway Validation |
Full simulation of email infiltration, phishing payload delivery, and gateway bypass |
Does not simulate email infiltration attacks to validate firewalls and email gateways |
|
Integration Breadth |
50+ native integrations across IPS, NGFW, WAF, EDR, EPP, XDR, SIEM, SOAR, email and web gateways, and ticketing tools |
Limited connectors. Integrations are positioned for workflow handoff rather than security control validation |
|
Deployment and Data Residency |
Cloud, on premises, hybrid, and air gapped from a single console |
Cloud SaaS or on premises. Air gapped support is constrained |
|
Best For |
Full spectrum CTEM, continuous security control validation, automated pentesting, lateral movement validation, and detection engineering |
Internal network pentesting and lateral movement validation |
What Real Users Think About Picus
Picus consistently outperforms Pentera and other security validation vendors on independent review platforms.
On Gartner Peer Insights, Picus is a Customers' Choice, with the highest 98% willingness to recommend score among all vendors in the 2025 Voice of the Customer for Adversarial Exposure Validation report, compared to Pentera's 89%. Picus also earned a 95% willingness to recommend in the equivalent 2024 BAS Tools report, the highest score of any vendor in that report as well.
On G2, Picus earns an exceptional 4.9 out of 5, reflecting its strong user satisfaction and product experience.
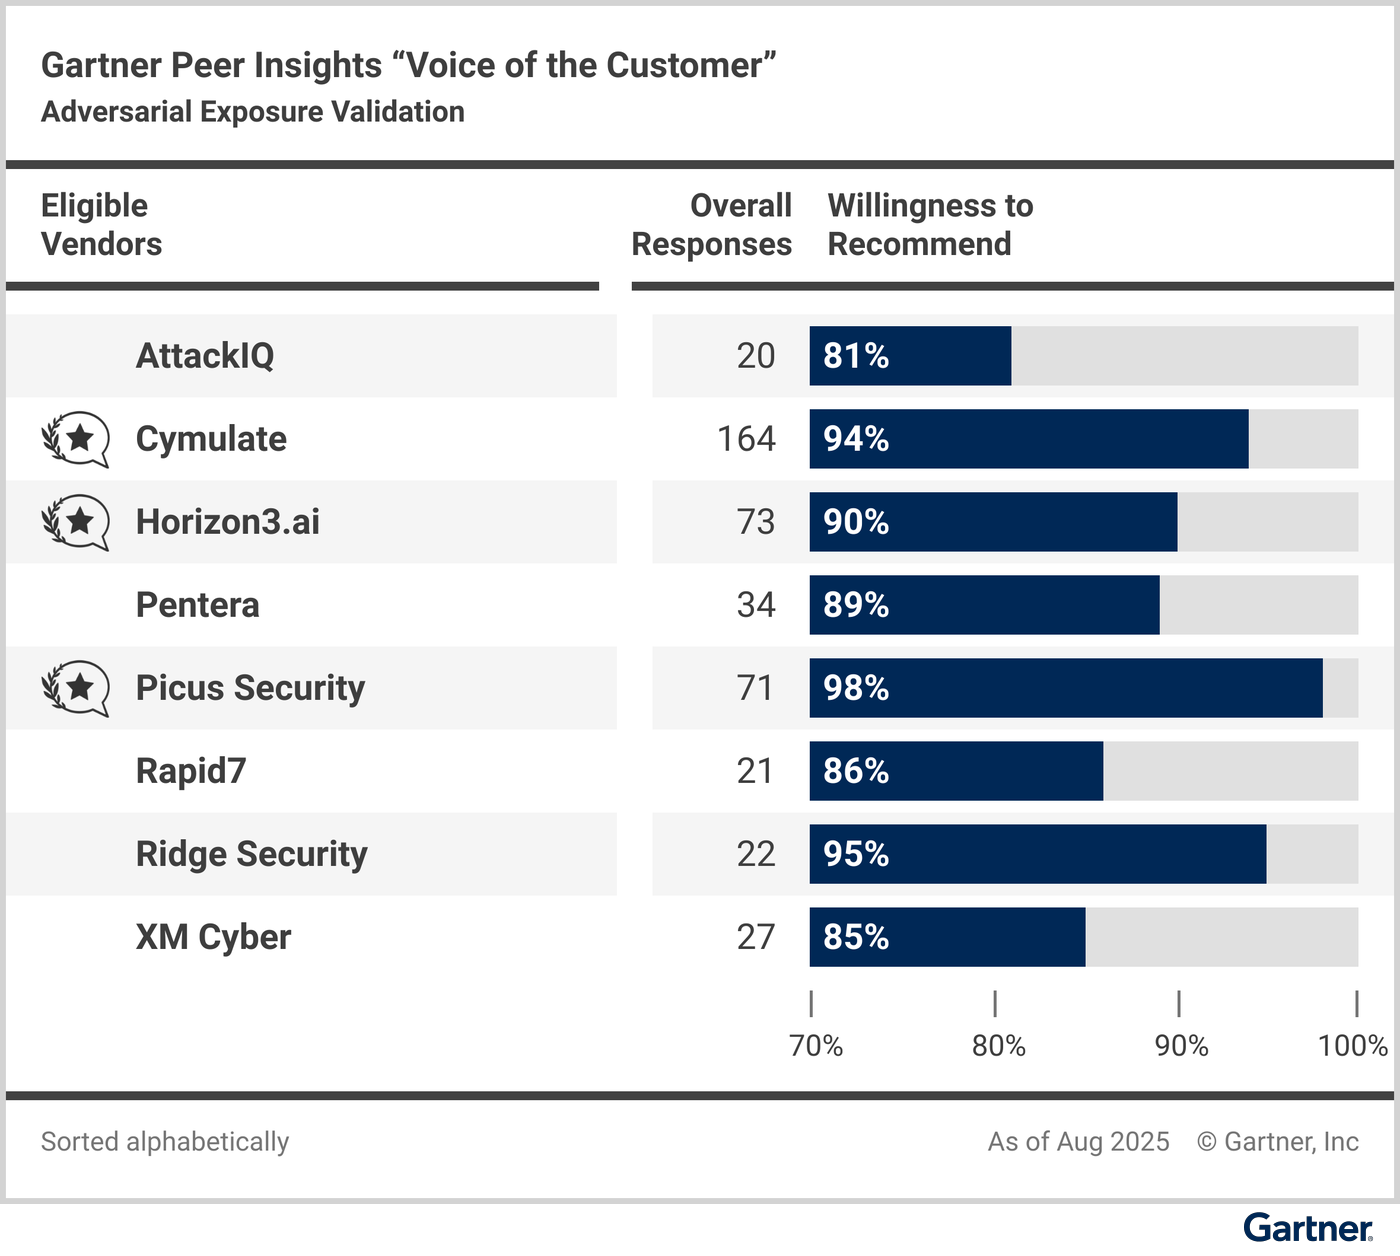
Figure: Gartner Peer Insights Voice of the Customer, As of August 2025
Users praise Picus for its ease of use, powerful detection engineering capabilities, continuous validation, and clear, actionable remediation guidance. Security teams highlight how quickly the platform delivers value and how it transforms their ability to monitor and improve defenses in real time.
- "Proactive, insight driven and reliable security validation." - IT Security and Risk Management (Energy and Utilities)
- "Continuous validation and automation enhance defense capabilities and efficiency." - Network Security Engineer (IT Services)
- "The tool has proven to be an invaluable asset, intuitive, automated, and effective at identifying weaknesses before attackers do." - IT Security and Risk Management (IT Services)
- "Stronger detections with Picus. They significantly improved our correlation and detection capabilities." - Engineer (Banking)
Together, this feedback makes one thing clear. Real users see Picus as the most reliable, highest rated, and fastest to value security validation platform available today.
-
Horizon3 (NodeZero)
Horizon3 delivers the NodeZero platform, an automated pentesting solution built to continuously find, fix, and verify exploitable weaknesses across on premises, cloud, and hybrid environments. NodeZero targets organizations seeking a self-service, SaaS delivered alternative to manual penetration testing and traditional vulnerability management.
Horizon3 and Pentera serve overlapping needs but with different philosophies. Pentera focuses on internal network penetration testing with an established product line, while NodeZero behaves as an active adversary, looking to reveal real attack paths. The platform is particularly effective in hybrid environments, where it exposes the identity and IAM seams attackers exploit to pivot between on premises environments and cloud services such as AWS, Azure, and GCP.
NodeZero stands out in these ways.
- Autonomous Attack Chaining maneuvers through cloud and on premises networks, chaining weaknesses together as a real attacker would to prove actual business impact.
- Path, Proof, and Impact reporting provides attack path visualization, step by step exploit chain, and impact assessment so teams know exactly what to fix.
- 1-Click Verify lets teams instantly retest a specific vector after applying a fix, without running a full pentest cycle.
- NodeZero Tripwires automatically deploys decoys along proven attack paths to enable early detection of active threats and real time alerting on malicious activity.
NodeZero also has known limitations.
- No native BAS or security control validation. Horizon3 explicitly states that NodeZero is not a breach and attack simulation tool and rejects atomic simulations, meaning it lacks the safe, hyper specific control validation typical of BAS platforms. Practitioners running NodeZero alongside detection gaps, cloud misconfiguration exposure, or thousands of unvalidated scanner findings often need a complementary platform.
- No air gapped deployment. As a SaaS first platform, NodeZero is not documented as supporting air gapped or fully isolated network environments, a constraint for classified or high security regulated environments.
- Limited detection engineering. NodeZero helps teams correlate telemetry by matching timestamps and commands with EDR or SIEM logs. There is no dedicated SIEM detection rule validator equivalent to Picus detection analytics.
- Narrower threat content transparency. NodeZero surfaces emerging threats through a Rapid Response center, but does not publish a formally defined SLA for new threat content releases comparable to dedicated BAS platforms.
- Web application pentesting remains in Early Access rather than general availability, and Linux post enumeration capabilities have been described as still under development by Horizon3's own engineering blog.
- Limited integrations. Integration documentation primarily covers ticketing platform APIs, webhooks, and a Splunk app. The GraphQL API exposes only a subset of portal functionality.
Horizon3 vs Pentera, Key Differences
|
Category |
Horizon3 (NodeZero) |
Pentera |
|
Core Technology |
Automated penetration testing with attack chaining |
Automated internal penetration testing |
|
Simulation Accuracy |
High practical accuracy driven by real exploit execution and attack path chaining |
Realistic exploit testing with strong lateral movement and credential abuse coverage |
|
Production Safety |
Production safe operation, but some actions can leave artifacts requiring manual cleanup |
Requires user approval for specific actions, which can slow large scale runs |
|
Detection Engineering |
EDR effectiveness module. No native SIEM detection rule validation |
No detection analytics. Users manually sift logs to analyze detection capability |
|
Remediation Guidance |
1-Click Verify retest after fix. Detailed fix guidance, but no vendor specific signatures |
Remediation Wiki, but no vendor specific signatures |
|
Threat Content SLA |
Rapid Response alerting. No publicly defined SLA |
Updates deployed every 4 to 6 weeks. No publicly defined SLA |
|
Email Gateway Validation |
Not a focus area |
Does not simulate email infiltration attacks |
|
Air Gapped Support |
Not documented |
Limited |
|
Licensing |
Tiered packages based on asset counts and feature sets |
Subscription based, tied to endpoints and domains, with additional modules at extra cost |
|
Best For |
Self-service automated pentesting with proof of impact reporting and rapid retest |
Internal network pentesting and lateral movement validation |
What Is Better than Pentera?
Both Picus Security and Horizon3 represent strong alternatives to Pentera, each with a distinct approach to the security validation problem. Horizon3's NodeZero excels at self-service automated pentesting with attack path visualization, making it a compelling choice for organizations that want to replace manual penetration testing at scale.
Picus Security takes a broader view of the problem, combining BAS, automated pentesting, attack path validation, detection rule validation, and exposure management into a single unified platform with the industry's fastest threat content SLA and the most actionable remediation library available. When security teams evaluate what Pentera does well, they are describing a platform optimized for a single layer of the security validation problem. Picus is built to solve the full problem.
Picus stands out as the superior solution compared to Pentera in several important areas.
- Picus provides over 80,000+ vendor specific prevention signatures and 4,400+ validated detection rules that teams can scan, copy, and deploy immediately, reducing the gap between identified and fixed. Pentera's Remediation Wiki provides directional guidance only and does not deliver vendor specific signatures.
- Picus delivers a guaranteed 24 hour threat content SLA with a measured 5.3 hour mean time to release for emerging threats, including those triggered by CISA alerts. Pentera does not publish a comparable public SLA, and customer reviews confirm threat content updates are deployed every 4 to 6 weeks.
- Picus supports cloud, on premises, hybrid, and air gapped deployments from a single centralized console. Pentera is primarily delivered as a cloud managed platform with limited options for air gapped networks, classified environments, or strict data residency requirements.
- Picus delivers automated detection rule validation, vendor specific detection content, and log source recommendations that directly improve SIEM efficiency. Pentera has no dedicated SIEM or EDR validation capabilities. Users must manually sift through logs to understand their detection posture.
- Picus simulates 30,000+ malicious actions spanning network infiltration, endpoint compromise, web application attacks, email infiltration, and data exfiltration. Pentera does not simulate email infiltration attacks to validate the effectiveness of firewalls and email gateways.
- Picus provides transparent, continuously updated threat libraries with full MITRE ATT&CK mapping so security teams understand exactly what they are measuring. Pentera's threat library operates as a relative black box with limited visibility into what is being tested and why.
- Picus Numi AI and the Picus Exposure Score (PXS) combine CVSS, EPSS, asset criticality, and validated control effectiveness into evidence-based risk scoring. This goes well beyond endpoint count based prioritization, giving CISOs defensible, business context aware metrics for board reporting.
- Picus offers 50+ native integrations across network, endpoint, SIEM, SOAR, email, web gateway, and ticketing tools. Pentera's integration ecosystem is more limited and primarily positioned for workflow handoff rather than security control validation.
- Picus has earned Gartner Peer Insights Customers' Choice designation for both Adversarial Exposure Validation (2025, 98% willingness to recommend) and BAS Tools (2024, 95% willingness to recommend), the highest scores in both reports. Picus also holds a 4.9 out of 5 rating on G2.
For security teams that have outgrown point in time penetration testing or are building toward a full CTEM lifecycle, Picus is the only platform that combines the depth of automated pentesting, the breadth of security control validation, and the operational completeness to close the loop from simulation to verified remediation, making it the clear choice over Pentera.
Book a demo to find out what separates Picus from Pentera, and other Pentera competitors.