Cloud Security Validation
Know Which Cloud Exposures an Attacker Could Actually Exploit
Audit AWS, Azure, and Google Cloud, then safely simulate real attacks to prove which misconfigurations and identities are reachable, exploitable, and worth fixing first.
the basics
What Is Cloud Security Validation?
Cloud security validation is the practice of safely emulating real attacker behavior against your cloud environment to confirm which misconfigurations and identities can actually be exploited, and what an attacker could reach with them. Rather than treating every flagged finding as a real risk, it gives you evidence: proof of which exposures are reachable in your environment, and which only look dangerous on paper.
Why it matters?
- From noise to evidence. Thousands of findings become the few that are truly exploitable.
- From symptoms to root cause. See which identities can escalate, so you fix policies, not individual alerts.
- From estates to one view. Validate AWS, Azure, GCP, and Kubernetes together.
- From point-in-time to current. Proof stays fresh as configs and identities change.
The problem
Your cloud generates thousands of findings. Few of them tell you what an attacker can do.
-
A backlog that resists clearing
Posture tools flag excessive permissions and misconfigurations by the thousand, but cannot say whether an attacker could ever use them.
-
IAM that is hard to reason about
Roles, policies, and entitlements multiply across accounts. Telling a genuinely abusable identity from one that only looks risky is nearly impossible by inspection alone.
-
An environment that changes daily
Identities, policies, and services change constantly. A point-in-time audit is stale almost immediately, leaving windows of unvalidated exposure between checks.
Cloud environments change daily, and shared-responsibility gaps are easy to miss. What looked safe last week may quietly be exploitable now, which leaves more alerts than answers and little certainty about what truly puts the business at risk.
The approach
Put your cloud under real attack, safely and continuously.
Picus Cloud Security Validation, scans core AWS, Azure, and Google Cloud services, then safely simulates real attacks against what it finds. You learn which misconfigurations are reachable, which identities can be abused, and how a single foothold chains into real impact, with clear steps to fix each one.
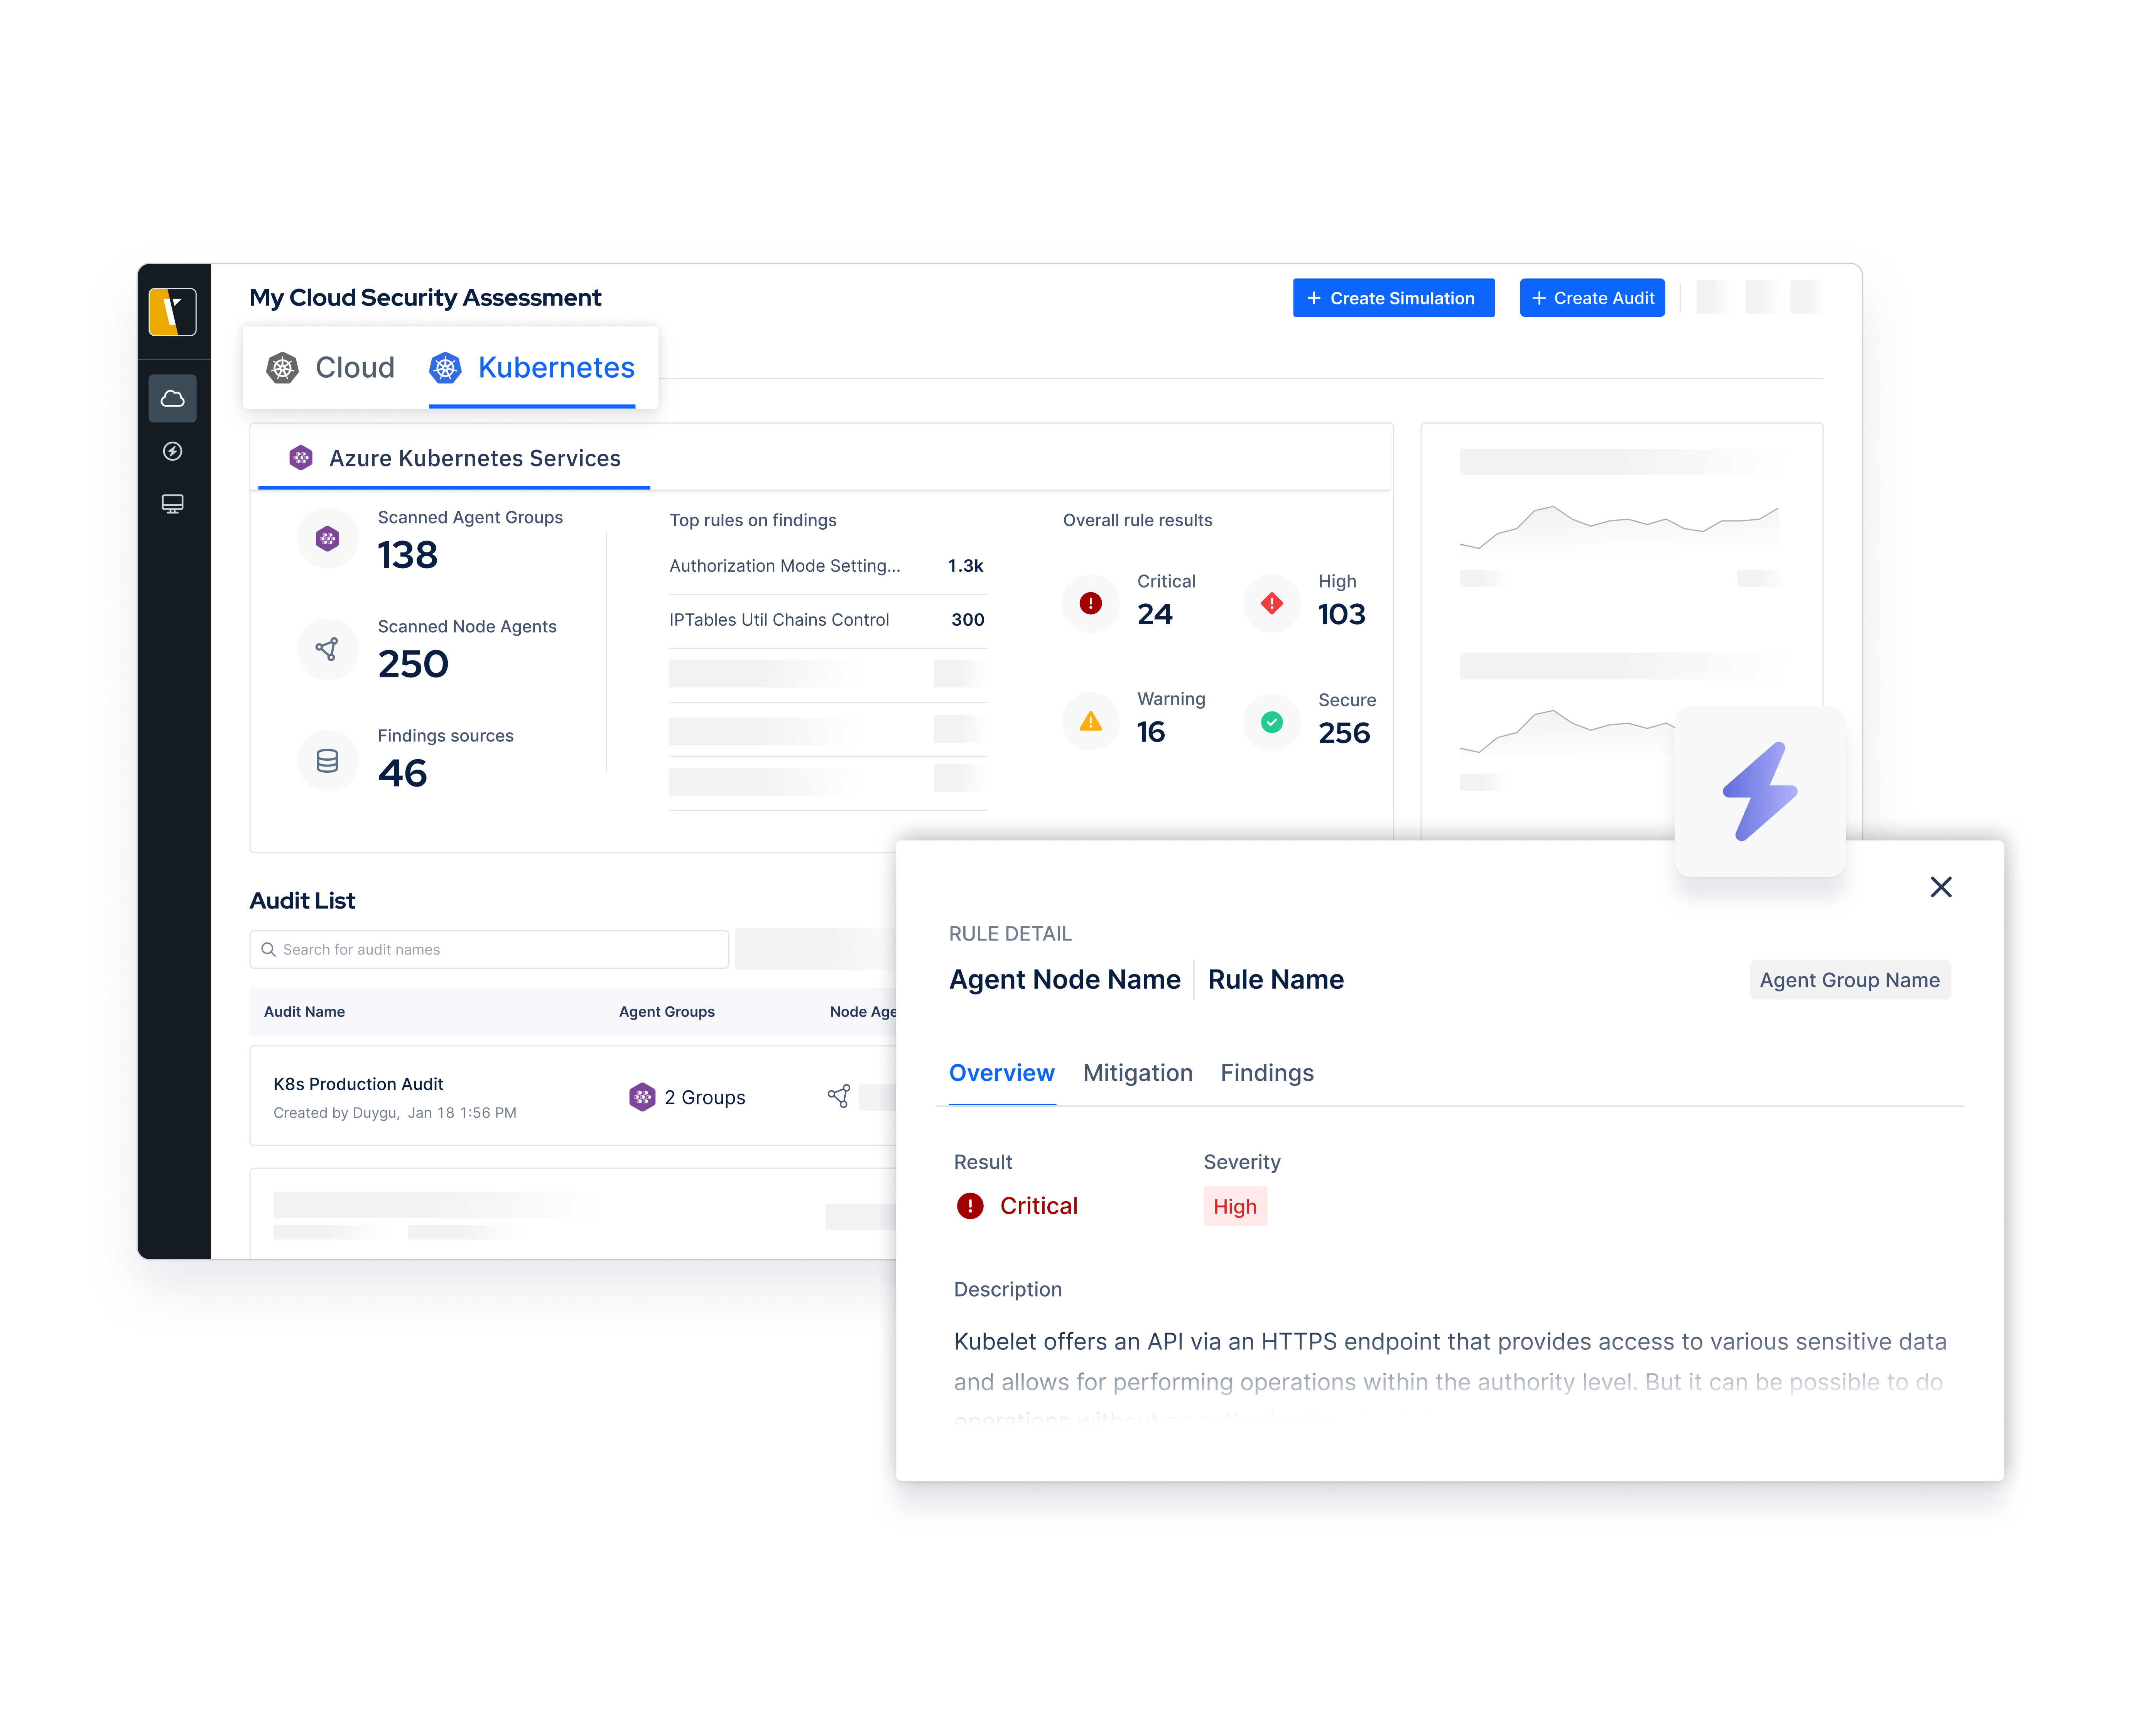
Cloud Auditing
Identify critical cloud misconfigurations.
Picus audits your cloud, then safely simulates real attacks to test whether misconfigurations are reachable, whether identities can be abused, and whether exposures chain into real impact. It turns a flat list of findings into evidence of what an attacker could actually do. Rules cover the exposures that lead to breaches: public access controls, unencrypted storage, dangling key pairs, cross-account access, and more.
Cloud Security Auditing across core AWS, Azure, GCP, and Kubernetes services.
Attack Simulation
Prevent overly permissive IAM policies.
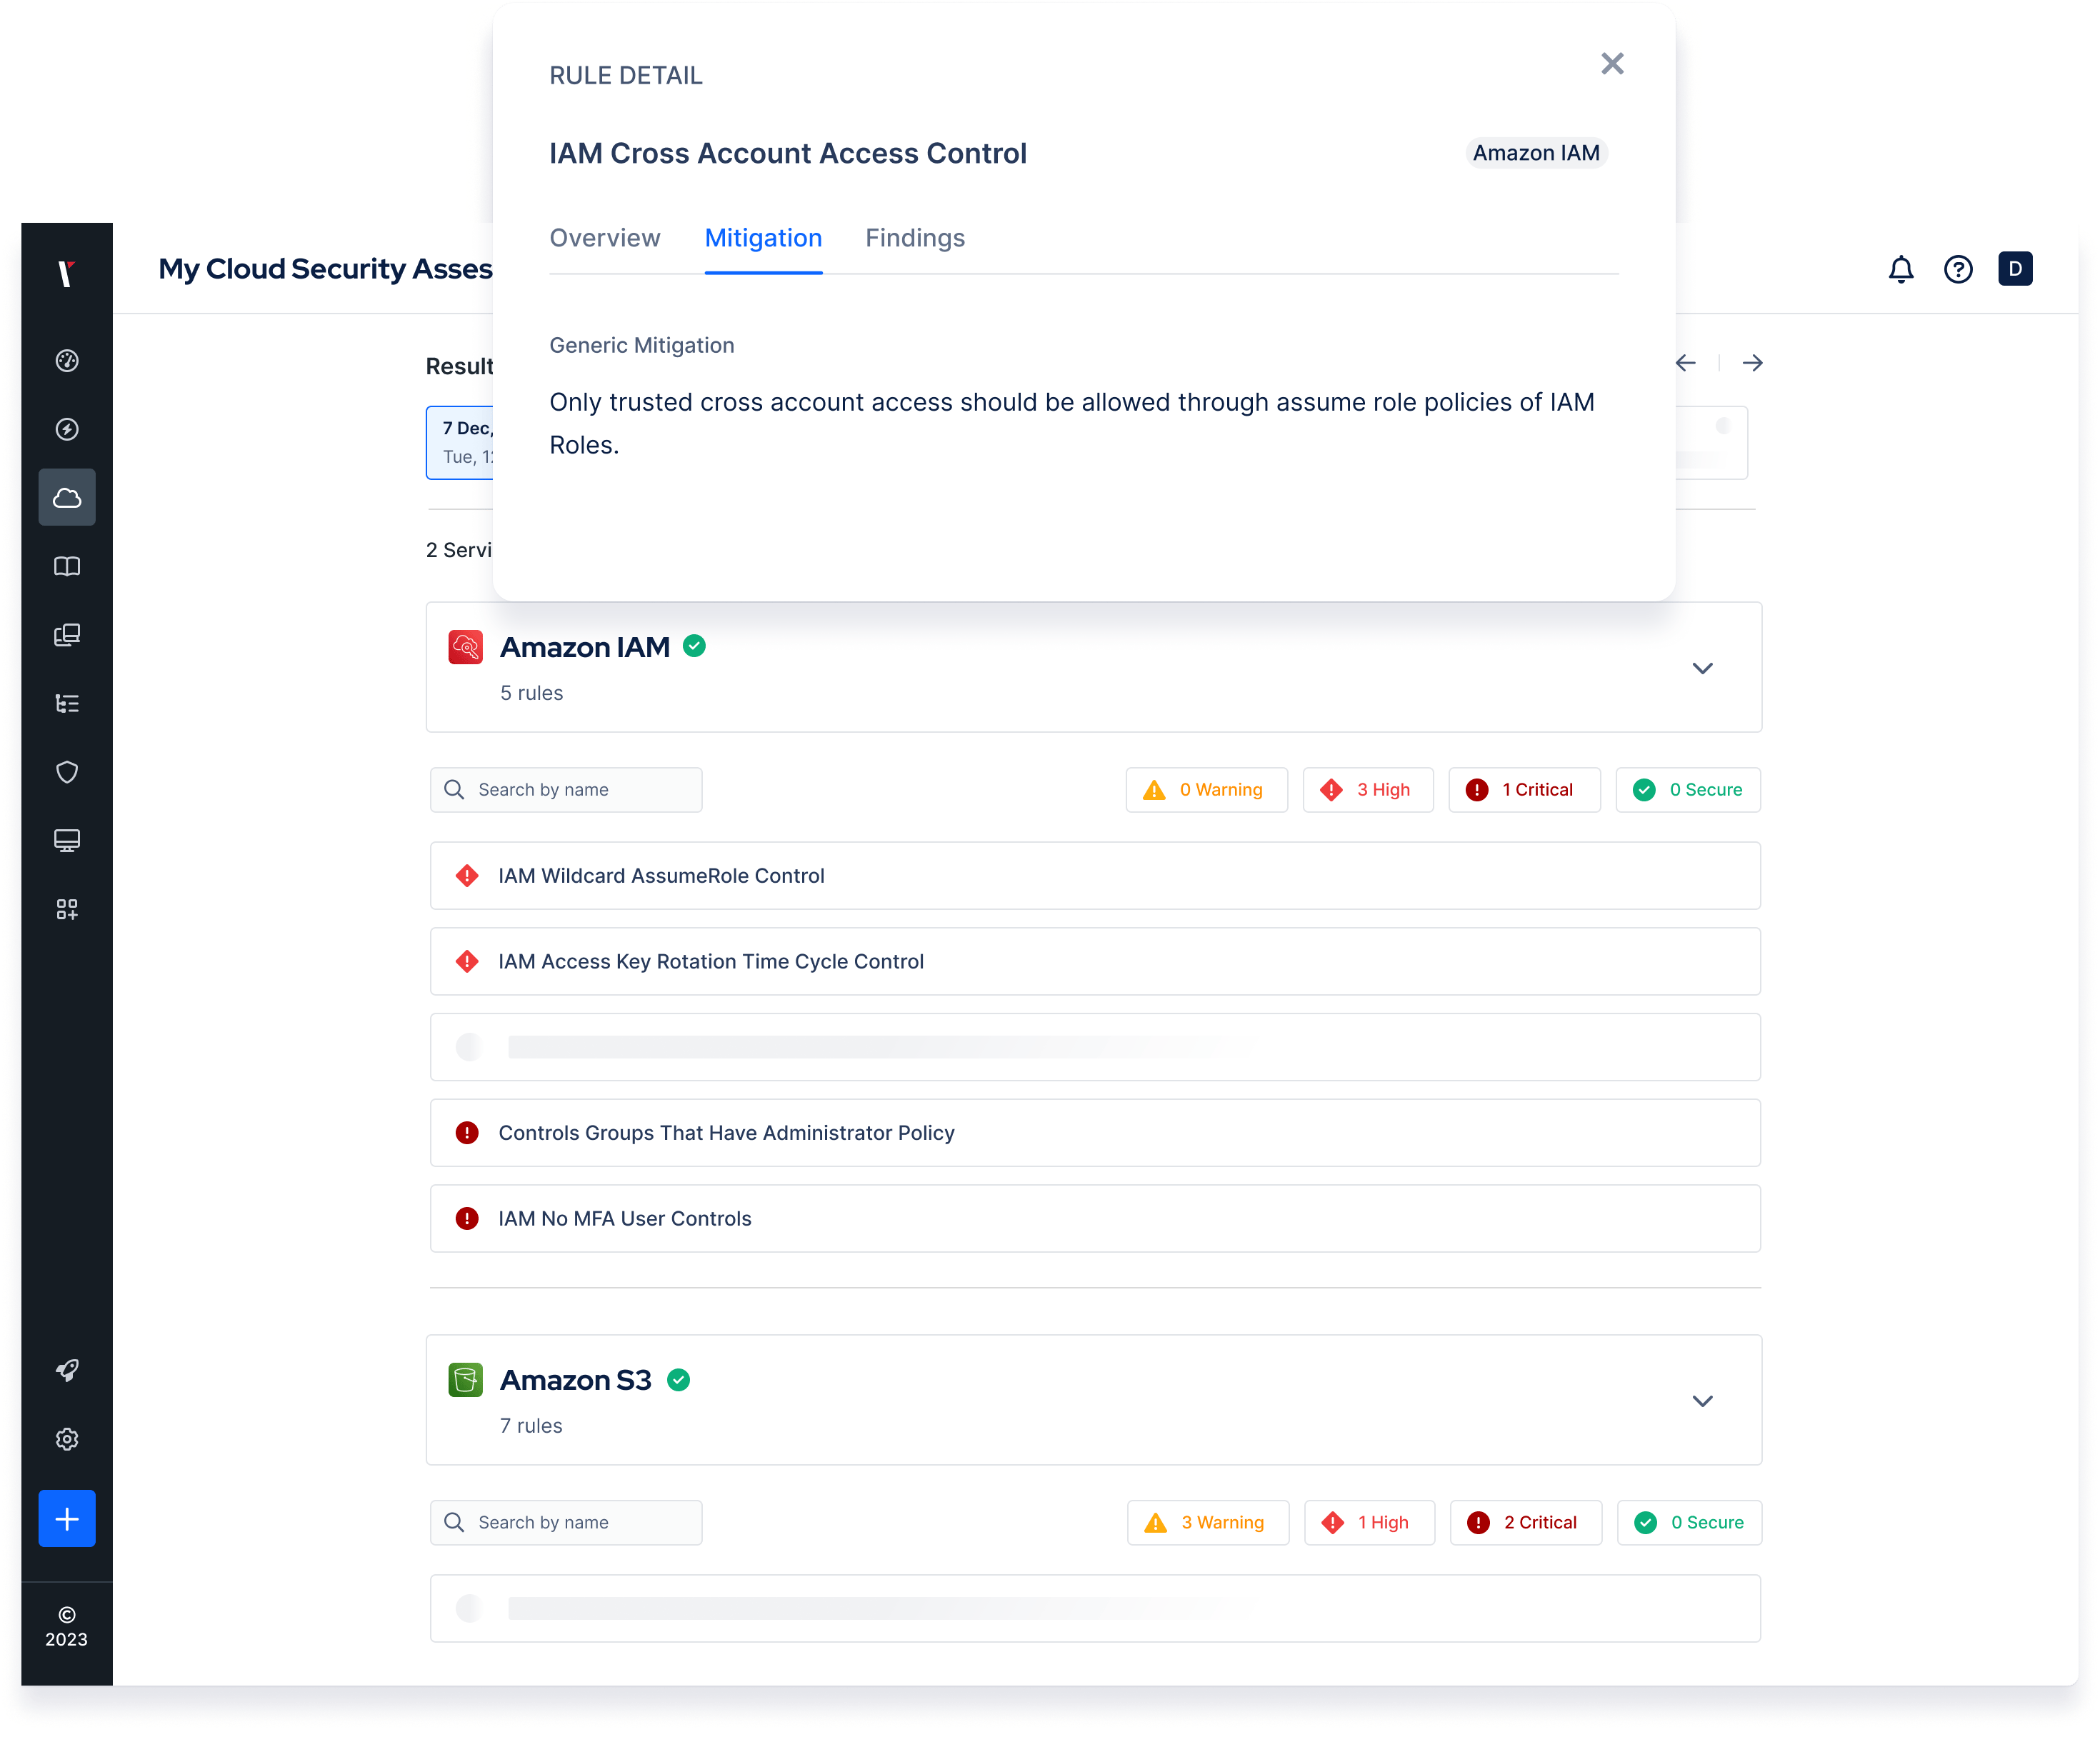
If attackers reach your cloud environment, they will likely try to escalate privileges toward critical systems. Picus gathers your cloud identities and runs them through a local policy simulator to reveal which roles, policies, and entitlements can actually be abused.
You see the exploitable targets each identity can reach, so you enforce the principle of least privilege where it matters, and fix policies instead of chasing individual symptoms.
Cloud Attack Simulation and the Picus Policy Decision Engine.
Attack Paths
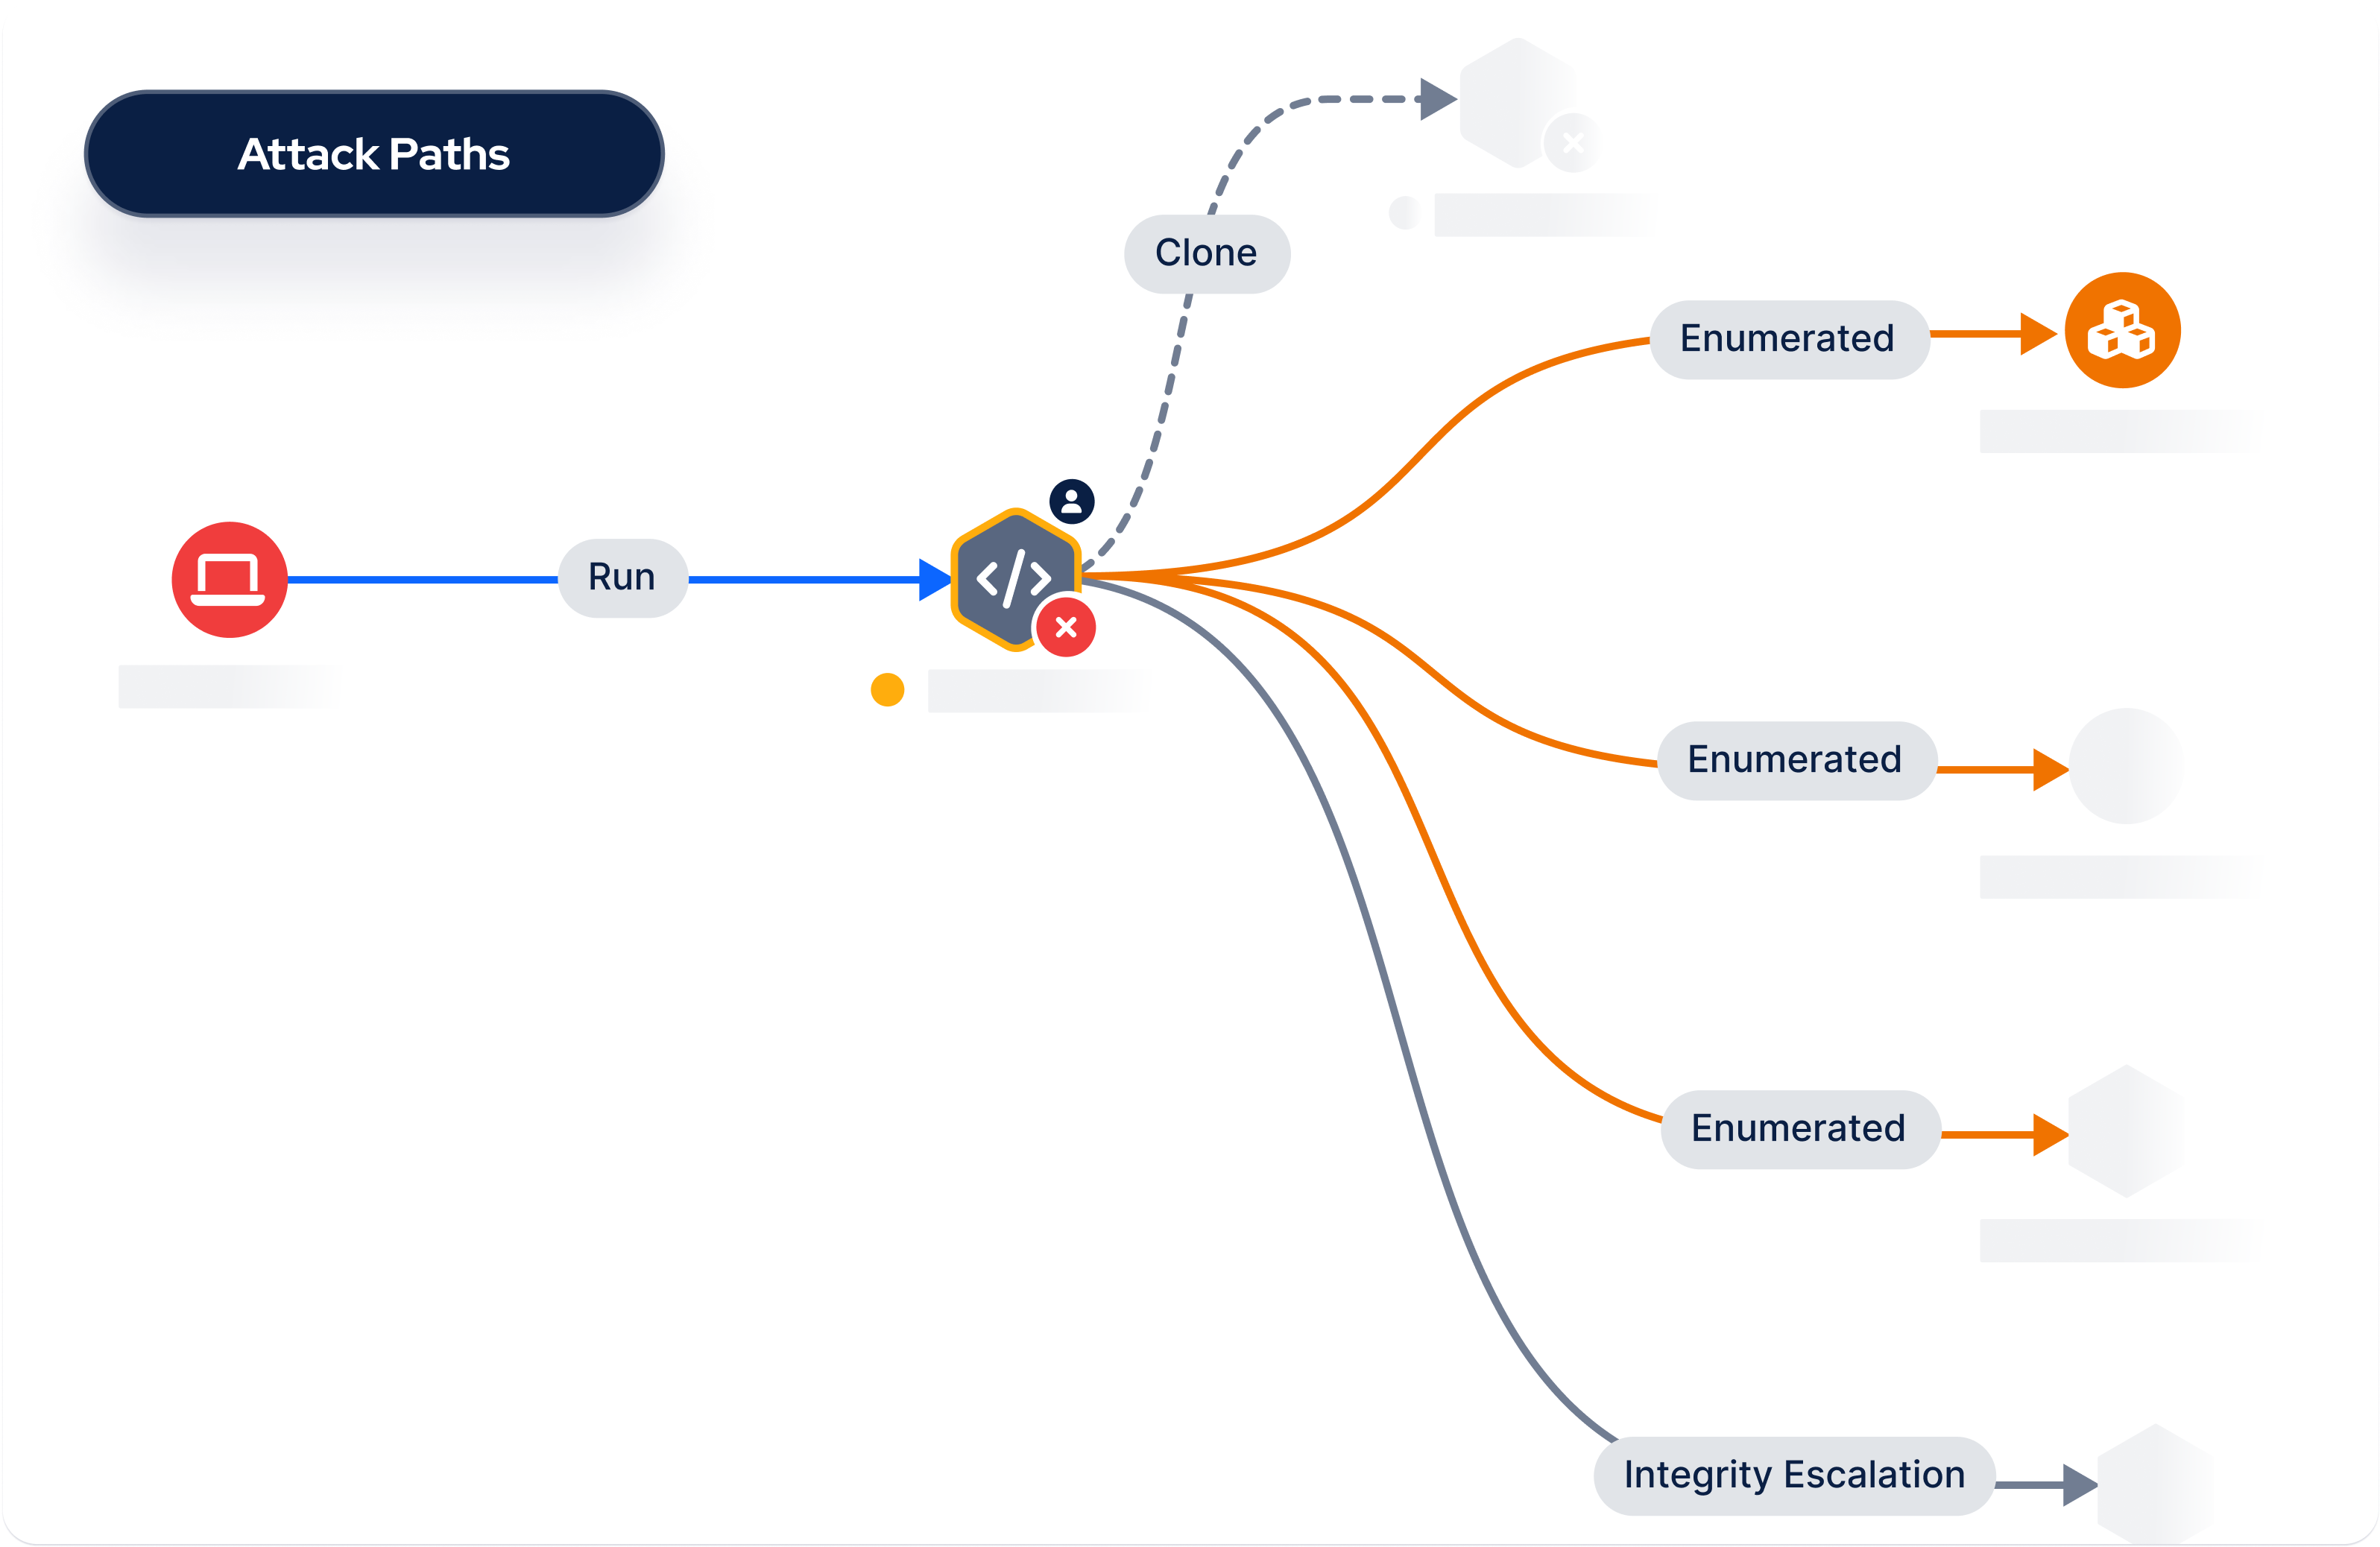
Simulate How an Initial Foothold Becomes a Breach.
Picus simulates how real adversaries chain identities, permissions, and cloud weaknesses together, showing how a single foothold can become access to critical systems and sensitive data, before an attacker finds the same path.
Powered by Attack scenario emulation that walks the chain step by step in your real environment and returns the outcome of each move.
Attack scenario emulation that walks the chain step by step in your real environment.
Actionable Insights
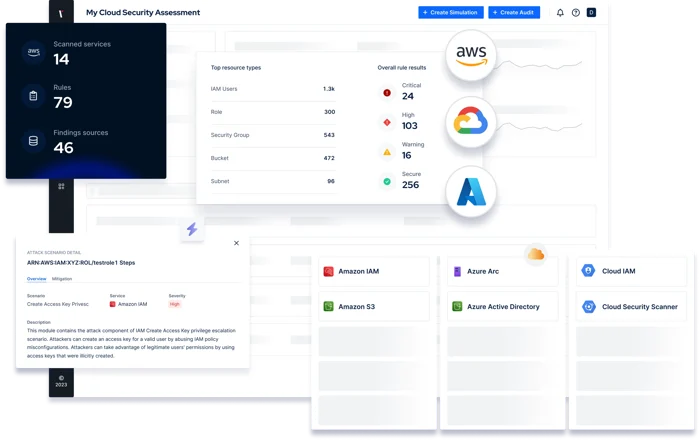
Validate AWS, Azure, and GCP From One Platform.
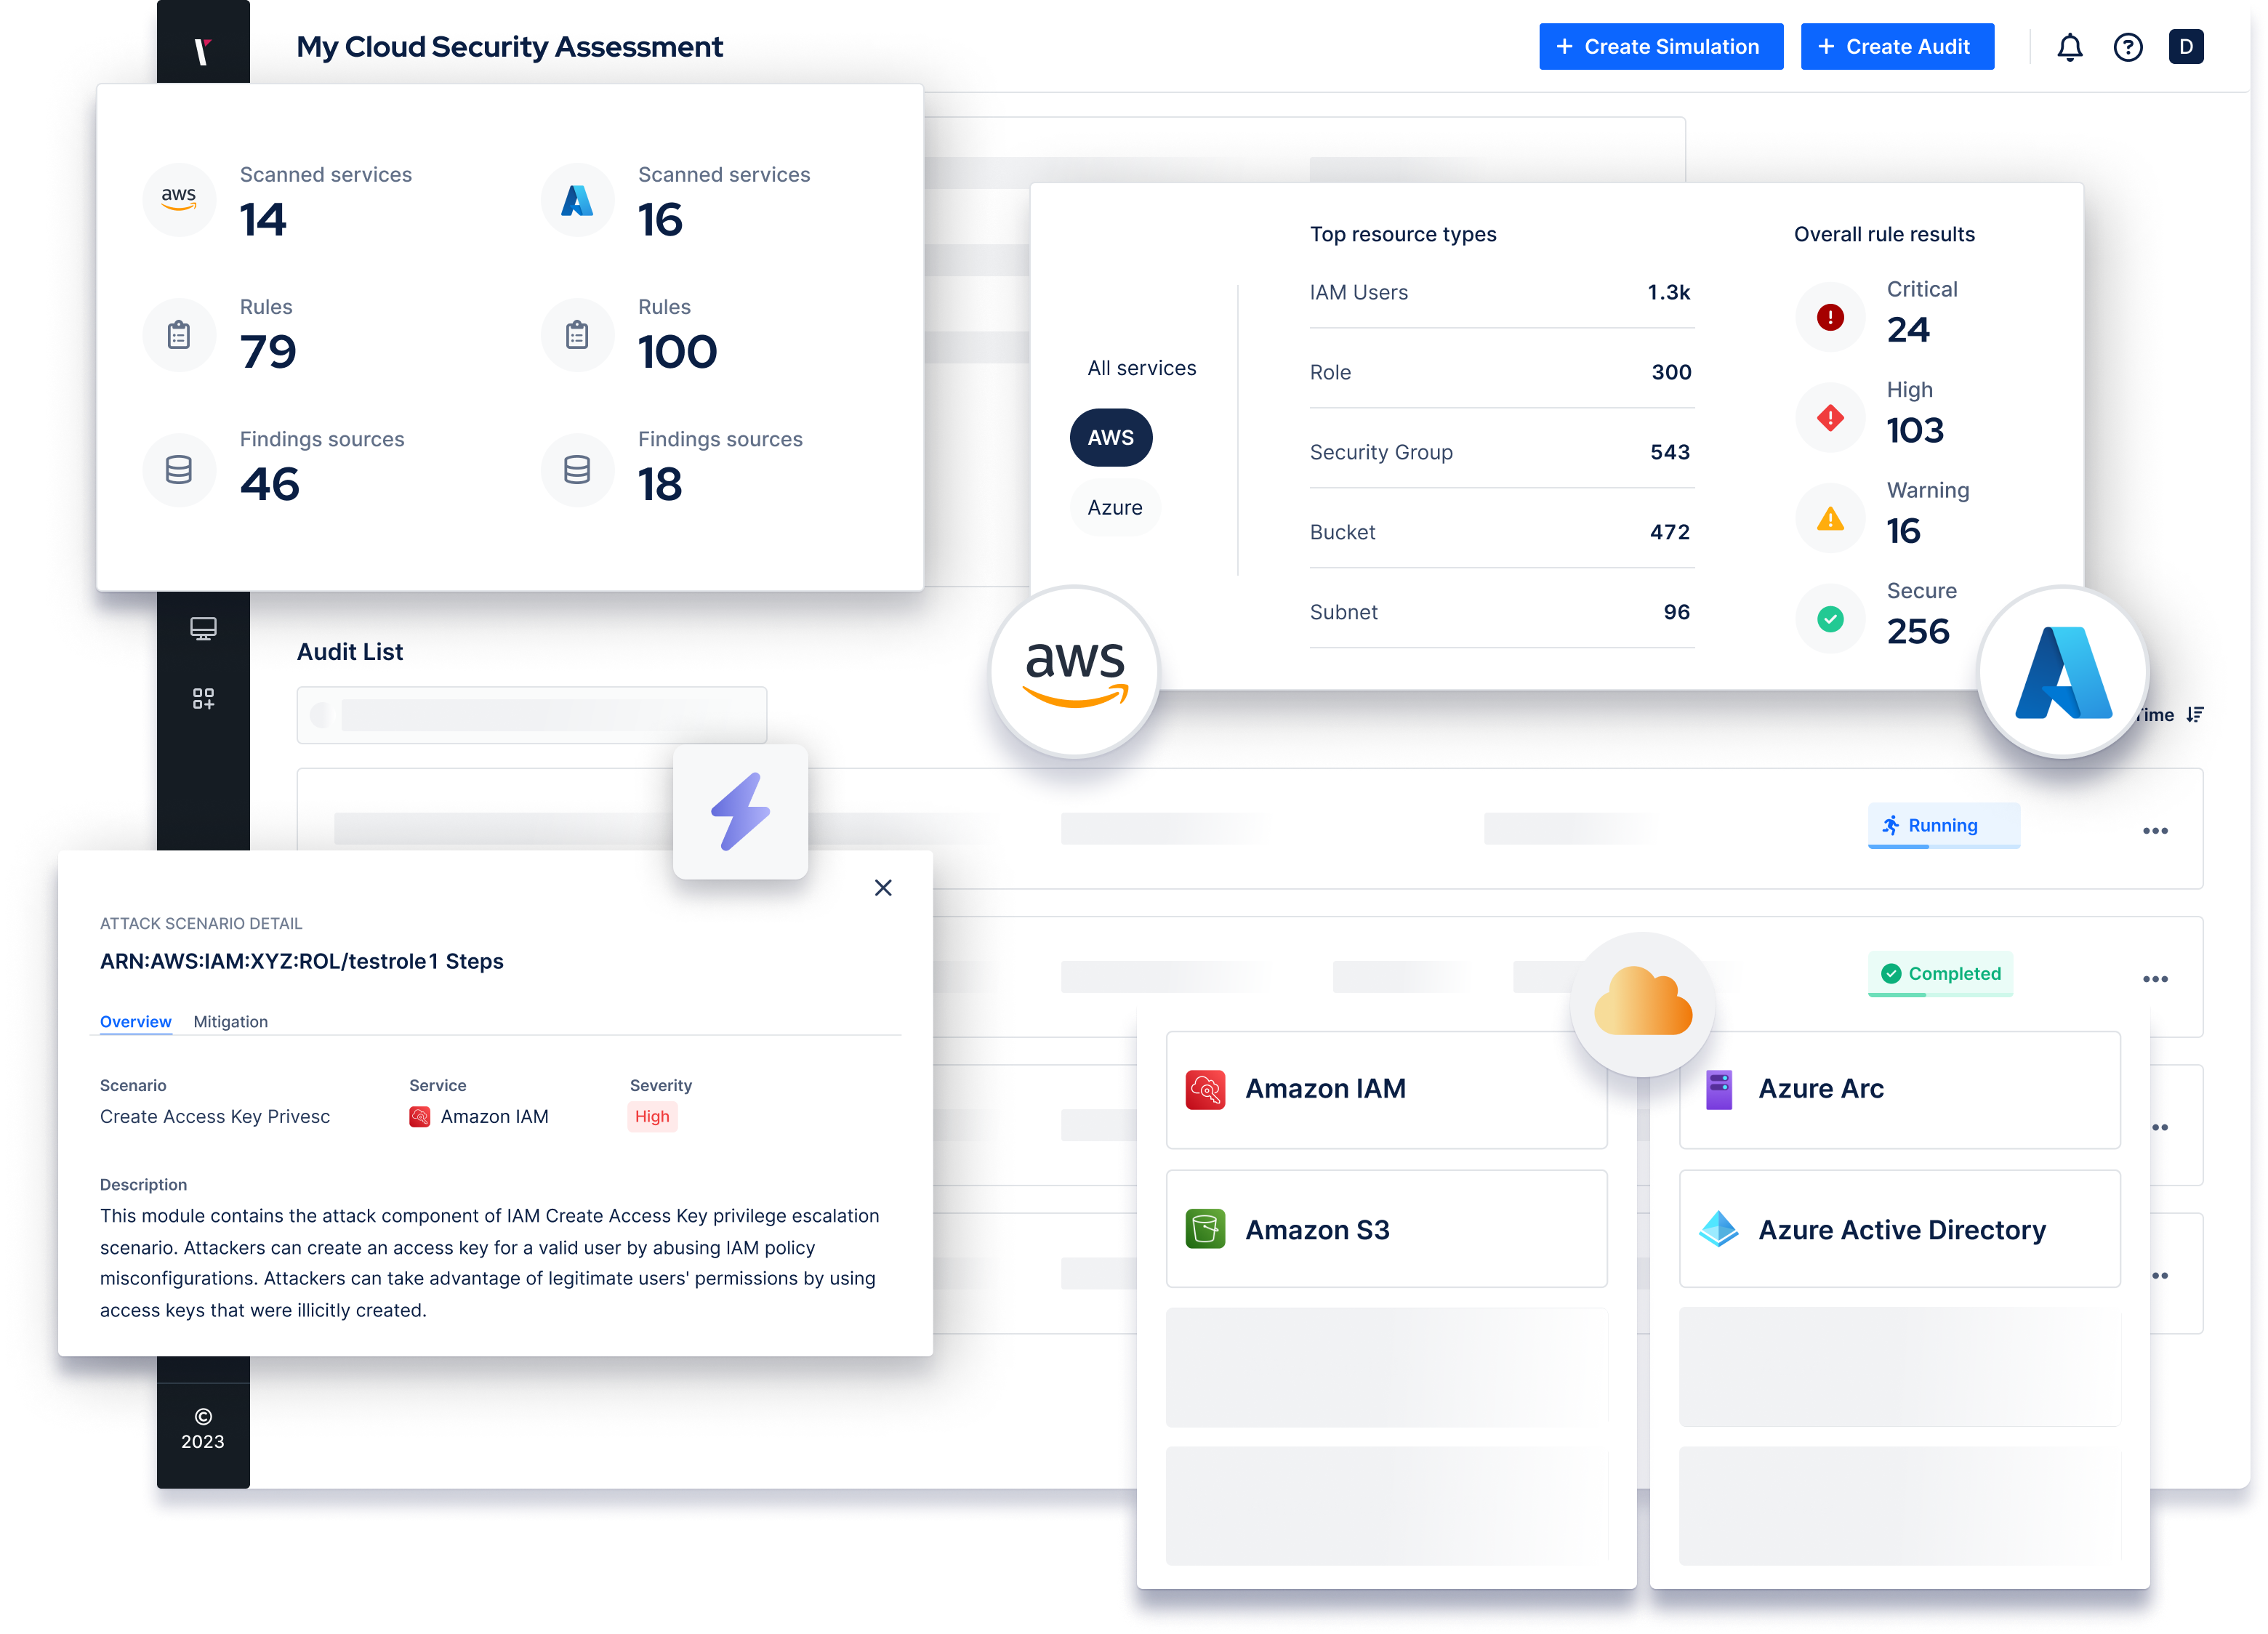
Picus does not just identify cloud risks. Built-in dashboards show scanned services, rules, findings sources, and top resource types at a glance, alongside overall rule results scored from Secure to Critical.
Track your posture over time and prove your maturity, with the severity and mitigation detail your team needs to respond sooner.
Built-in dashboards and scheduled audits with a full result timeline.
How it works
Audit, simulate, decide, re-validate
Picus Cloud Security Validation runs a continuous loop across your cloud, so proof keeps pace with how fast the environment actually moves.
-
01
Cloud Auditing
Inspects core cloud and Kubernetes resources against best practice with read-only permissions, surfacing misconfigurations.
-
02
Attack Simulation
The Policy Decision Engine runs gathered identities through a local policy simulator to map possible escalation techniques.
-
03
Mitigation Insights
Returns result, severity, affected resources, and policy-level mitigation guidance, so you fix one policy and close many exposures at once.
-
04
Re-Validation
Schedule audits weekly or run them on demand after any change, and track the result timeline to prove your posture is improving.
Integrations
Unlock Your Security Stack’s Full Power
Picus integrates with the controls you already run, so simulation results turn directly into tuning and remediation.
- Identify what your NGFWs, WAFs, EDRs, SIEMs, and other security controls are missing.
- Fine-tune controls using vendor-specific and agnostic mitigation guidance and detection rules.
-
99% of cloud security of cloud security failures through 2025 will be the customer’s fault, mainly cloud resource misconfiguration.
What Sets It Apart
Built for Evidence, Not Another List of Findings
-
Proof, not just posture.
Most tools stop at flagging misconfigurations. Picus goes further, simulating real attacks against what it finds to confirm which exposures are genuinely reachable, so you act on evidence instead of a longer list of "critical" labels.
-
Identity paths, not just settings.
Picus runs your cloud identities through a local policy simulator to reveal which roles and permissions can actually be abused for privilege escalation. You fix the policy, not the symptom.
-
One platform, one loop.
Validated cloud findings feed the broader Picus loop, joining exposure, identity, and control-effectiveness data across your whole environment, so cloud risk is measured the same way as everything else you defend.
Proof
Trusted by Security Teams, Recognized by the Industry
-
Customers' Choice
Gartner Peer Insights Voice of the Customer Adversarial Exposure Validation
-
BAS Category Leader
#1 Breach and Attack Simulation
(BAS) Solution
-
#1 Leader Frost Radar
The Innovation Leader in
Automated Security Validation
-
Outstanding Experience with Picus – A Game-Changer in Security Validation. The platform is intuitive, the reporting is clear, and the actionable insights significantly enhance our overall security posture.
Cyber Security Team Lead, Mid Market
Read more -
It allows me to test current cyber attack scenarios within my own environment, which is extremely valuable for improving our security posture.
Manager, IT Security and Risk Management, IT Services
Read more
The Picus Platform
One Platform Validates Your Whole Security Program
Cloud Security Validation is one part of the Picus Platform. Together, these capabilities converge into one continuous validation loop, from attack surface to controls to exploitable exposures.
-
Picus BAS
Breach & Attack Simulation
Continuously tests what your EDR, SIEM, firewall, and WAF actually block and detect against the newest attacker techniques, then ships the fixes and re-validates that the gap closed.
-
Picus APV
Autonomous Pentesting
Executes real exploit chains against reachable assets, showing what an attacker can actually reach and do, not what a CVSS or EPSS score predicts. Live validation, run safely in production.
-
Picus EXV
Exposure Validation
Proves exploitability without firing an exploit, covering the restricted assets no live test can touch and the CVEs with no public or safe exploit, for a defensible verdict on day one of disclosure.
FAQ
Frequently Asked Questions
About Cloud Security Validation
What is Cloud Security Validation?
Cloud security validation safely emulates attacker behavior against your cloud environment to confirm which misconfigurations and identity exposures are actually exploitable, and what an attacker could reach with them. Instead of assuming a finding is a risk, it produces evidence of real exploitability.
Is Cloud Security Validation the same as Cloud Security Posture Management (CSPM)?
No. CSPM identifies misconfigurations and policy violations, telling you what might be wrong. Cloud security validation proves which of those findings are actually exploitable given your real controls. Posture management produces a list; validation produces evidence. The two are complementary, posture data is a useful input, and validation tells you which inputs need your attention.
What’s the Difference Between CSV and a CNAPP?
A CNAPP provides broad cloud security coverage, from posture management to workload protection. Cloud Security Validation tells you whether cloud exposures can actually be exploited. Picus complements your CNAPP by validating real-world exploitability and feeding evidence back into prioritization, so teams focus on the exposures that create real risk.
Does Cloud Security Validation replace CIEM?
No. CIEM maps and manages cloud entitlements. Cloud Security Validation tests those entitlements against real privilege-escalation and lateral-movement attempts, proving which over-permissioned identities are genuinely abusable. CIEM tells you what permissions exist; validation tells you which ones an attacker could exploit.
Does Picus Support AWS, Azure, and GCP?
Does Picus Support AWS, Azure, and GCP. Yes. Picus validates cloud configurations, controls, and identity across AWS, Azure, and GCP from a single platform, so multi-cloud environments don't fragment into separate, inconsistently validated estates. It works with read-only permissions to avoid changing your environment.
What Is Container and Kubernetes Security Validation?
It's the testing of container and Kubernetes controls, such as cluster configuration, pod policies, and control-plane exposure, against real attacker techniques rather than a static checklist. Picus audits Kubernetes against CIS benchmarks across the control plane, nodes, pods, and policies.
How Often Should Cloud Security Be Validated?
Cloud environments change daily, so point-in-time audits leave windows of unvalidated exposure. Powered by Picus Swarm, validation runs on the affected surface in real time when a configuration or identity policy changes, on signal rather than on a calendar, so it keeps pace with how fast the cloud actually moves.
See How Picus Platform Works
-
See Picus Run on Your Environment
In a live demo, watch Picus validate a real exposure end to end, from exploit to fix to re-test.
-
Discover the Platform
Simulate real-world cyber threats in minutes and see a holistic view of your security effectiveness.