
Cyber threat intelligence (CTI) is evidence-based knowledge about adversaries, including who they are, what they want and how they operate, that has been collected, analyzed and put in context so defenders can make better decisions. Unlike raw threat data, intelligence answers a specific question for a specific audience, from a detection engineer tuning a rule to a CISO setting budget.
Key Takeaways
- Data is not intelligence. Hashes, IPs and domains become intelligence only when someone adds context and judgment about what they mean for your organization and what to do next.
- You need both IOCs and TTPs. IOCs keep known-bad files out at the perimeter; TTPs stop the behavior inside. In Picus Labs' Blue Report 2026, based on more than 338 million attack simulations, IOC-based prevention of malware downloads fell to 50%, and controls that blocked Mimikatz's LSASS dump 94% of the time stopped the same tool's registry route only 3% of the time.
- Attacker behavior outlasts its artifacts. Picus Labs' Red Report 2026, based on 1.15 million files and 15.5 million attacker actions from 2025, found Process Injection (T1055) at #1 for the third year in a row, while noisy credential dumping fell out of the top ten in favor of quieter routes.
- Intelligence must end in a tested control. Mapping a threat to ATT&CK shows what should be covered; simulating it shows whether your defenses actually stop it.
Threat Data vs. Threat Intelligence: What's the Difference?
Most "threat intelligence" feeds are really threat data: lists of IP addresses, domains, file hashes and URLs. Data becomes information when it is enriched with context, such as the malware family a hash belongs to. It becomes intelligence only when an analyst adds judgment about what it means for this organization and what to do next. Figure 1 shows how this looks on a real threat in the Picus Threat Library.
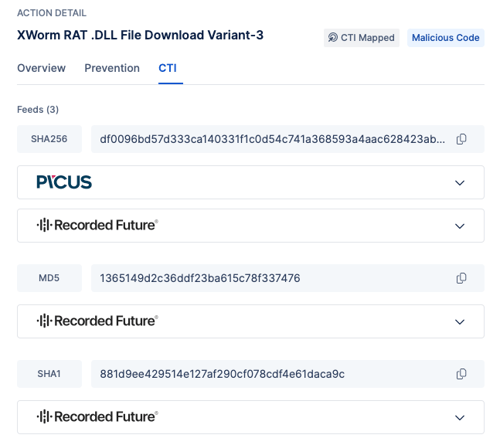
Figure 1. Example CTI mapping from the Picus BAS
Figure 1 breaks down into three layers:
- Data: The MD5, SHA-1 and SHA-256 hashes from CTI feeds. On their own, they only identify a file.
- Information: Picus maps those hashes to a known threat in its library, a .DLL download variant of XWorm. XWorm is a modular remote access trojan sold as malware-as-a-service since 2022 and used for remote control, keylogging and credential theft.
- Intelligence: Because the mapped threat is a ready-to-run simulation, you can test it against your own controls right away. If the XWorm .DLL gets past your web gateway and next-generation firewall, you know exactly what to fix: the missing vendor signatures and configuration settings on those two controls.
That is the "so what?" test in practice: real intelligence names a threat, shows it applies to you, proves the gap and points to the fix.
What Are the Four Types of Threat Intelligence?
CTI is usually split by who consumes it and how long it stays useful.
|
Type |
Audience |
Question it answers |
Typical format |
Shelf life |
|
Strategic |
CISO, board, risk leaders |
Which threats matter to our business, and where should we invest? |
Briefings, risk assessments |
Months to years |
|
Operational |
Incident responders, threat hunters |
Who is behind this campaign, and what will they do next? |
Actor profiles, campaign reports |
Weeks to months |
|
Tactical |
Detection engineers, SOC, red teams |
Which techniques should we detect and test? |
TTPs mapped to MITRE ATT&CK, detection rules |
Months |
|
Technical |
Firewalls, EDR, SIEM, SOAR |
What should we block or alert on right now? |
Indicators delivered over STIX/TAXII |
Hours to days |
The boundaries blur in practice, but every intelligence product should name its consumer.
How Does the Threat Intelligence Lifecycle Work?
CTI teams run a repeating cycle borrowed from government intelligence practice, in which feedback restarts the loop.
- Direction. Stakeholders set priority intelligence requirements (PIRs), such as "Which ransomware groups target European manufacturers, and how do they get in?" Without PIRs, teams collect everything and answer nothing.
- Collection. Analysts gather internal telemetry (SIEM, EDR, incident cases), open sources, commercial feeds, sandbox output, dark-web sources and sharing communities such as ISACs.
- Processing. Raw data is parsed, deduplicated, translated and normalized, usually into STIX 2.1, the OASIS standard for threat data, so machines and analysts can both use it.
- Analysis. Analysts link indicators to actors and techniques, grade source reliability and confidence (for example with the Admiralty Code) and test competing hypotheses to limit bias.
- Dissemination. Each audience gets its own format: a one-page brief for executives, ATT&CK-mapped TTPs for detection engineers, indicators over TAXII for controls. Traffic Light Protocol (TLP) 2.0 labels set how far each report may travel.
- Feedback. Consumers report what helped and what was missing, which reshapes the next set of requirements.
Sharing extends the loop beyond one company, but its legal footing is uneven. US protections under the Cybersecurity Information Sharing Act of 2015 have survived only on short-term extensions since lapsing in September 2025, and 55% of organizations in the 2026 SANS CTI Survey lack legally reviewed sharing processes.
Which Frameworks Do Threat Intelligence Analysts Use?
Frameworks give analysts a shared language, so one team's findings can be acted on by another without translation.
MITRE ATT&CK
ATT&CK is a knowledge base of adversary behavior, organized into tactics (the attacker's goal), techniques (how they reach it) and procedures (specific implementations). Version 19, released in April 2026, covers 15 Enterprise tactics, 222 techniques and 475 sub-techniques, and it split the old Defense Evasion tactic into Stealth and Defense Impairment. Mapping every report to ATT&CK tells detection engineers exactly which behaviors to cover.
The Diamond Model and the Cyber Kill Chain
The Diamond Model describes each intrusion through four linked features: adversary, capability, infrastructure and victim. Pivoting between them, for example from one command-and-control server to every domain on the same hosting, turns a single indicator into a campaign. Lockheed Martin's Cyber Kill Chain adds sequence, splitting an intrusion into seven stages from reconnaissance to actions on objectives so defenders can see where to break it.
The Pyramid of Pain: IOCs vs. TTPs
David Bianco's Pyramid of Pain ranks indicators by how much it costs an attacker when defenders act on them. Hash values sit at the bottom, followed by IP addresses, domain names, network and host artifacts, tools and, at the top, TTPs. A hash changes with a single recompile; changing behavior means retooling the whole operation.
That does not make IOCs expendable. Indicators are cheap to share, fast to deploy and exactly what perimeter controls are built to act on: firewalls, web proxies and secure email gateways should stop known-bad files at the edge. The two layers answer different questions, so a mature program tests both.
|
IOC-based testing |
TTP-based testing |
|
|
Question it asks |
Does the control recognize known bad? |
Does the control stop the behavior, by any route? |
|
Controls it fits |
Firewalls, web proxies, WAFs, secure email gateways |
EDR, IDS, SIEM detection content |
|
What a pass proves |
The edge blocks a known malicious sample |
The attacker's objective is blocked, whatever the tool |
|
Blind spot |
New hashes, repacked or recompiled samples |
Only meaningful when every route to the technique is tested |
Both layers are slipping, in different ways. In Picus Labs' Blue Report 2026, based on more than 338 million attack simulations in customer environments, the IOC-based prevention rate for malware downloads fell to 50%, from 60% a year earlier and 71% in 2024. Indicators now churn faster than signature updates can follow.
The behavioral layer fails more quietly: controls learn the famous procedure, not the technique. When Picus Autonomous Penetration Testing ran Mimikatz three ways toward the same goal, OS Credential Dumping (T1003), the results split sharply. Dumping credentials from LSASS memory, the classic and heavily signatured path, was blocked in 94% of attempts. Pulling RDP credentials from other memory locations was blocked in 17%, and reading LSA Secrets from the registry in just 3%. Same tool, same outcome for the attacker; only the route changed.
Attackers have drawn the same conclusion. Picus Labs' Red Report 2026, which mapped 15.5 million malicious actions from 2025 to MITRE ATT&CK, found that noisy credential dumping (T1003) has dropped out of the top ten techniques, while quieter theft from password stores (T1555) holds third place. Process Injection (T1055) stayed first for the third year running, seen in 30% of samples, even as the hashes behind it changed constantly. That is the Pyramid of Pain at scale: the artifacts rotate, the behavior stays.
For CTI teams, the lesson is to hand detection engineers the technique and every known route to it, not just the hashes from last week's report, and to keep IOC feeds flowing to the perimeter at the same time.
How Is AI Changing Threat Intelligence in 2026?
- Adversaries are operationalizing AI. In May 2026, Google Threat Intelligence Group reported a cybercrime actor using a zero-day exploit it believes was developed with AI assistance. Its September 2026 tracker describes a shift toward more autonomous, agentic attack workflows.
- Endpoint behavior is still classic. The Red Report 2026 found no notable uptick in AI-driven malware techniques in 2025 samples. AI speeds up the attacker's workflow, but the techniques that land on endpoints remain well known, so TTP-based defenses still apply.
- Defenders use AI for the heavy lifting. LLMs now summarize reports, translate sources, extract indicators and draft ATT&CK mappings, while analysts keep the judgment calls on confidence and attribution.
The Threat Intelligence Toolkit
No single product covers the whole lifecycle, so mature teams combine platforms, sources and detection languages.
|
Lifecycle stage |
Category |
Common tools |
What it does |
|
Processing and analysis |
Threat intelligence platforms (TIPs) |
MISP, OpenCTI, ThreatConnect (Dataminr), Anomali ThreatStream |
Store, correlate and share indicators, actors and reports as STIX objects |
|
Collection |
Commercial intelligence |
Google Threat Intelligence, Recorded Future, CrowdStrike, Intel 471 |
Finished reporting, actor tracking and enrichment at scale |
|
Collection |
Open and community sources |
abuse.ch (URLhaus, ThreatFox, MalwareBazaar), AlienVault OTX, CISA KEV, ISAC feeds |
Free indicators, malware samples and exploited-vulnerability lists |
|
Collection |
Infrastructure search |
Shodan, Censys, passive DNS, WHOIS history |
Map adversary infrastructure and pivot from one server to the rest |
|
Analysis |
Malware analysis |
VirusTotal, ANY.RUN, CAPE Sandbox, Ghidra |
Detonate and reverse samples to extract behavior and configuration |
|
Dissemination |
Detection languages |
Sigma, YARA, Suricata rules, KQL and SPL queries |
Turn intelligence into portable detections for SIEM, EDR and network sensors |
|
Feedback |
Coverage and validation |
MITRE ATT&CK Navigator, DeTT&CT, breach and attack simulation |
Show which techniques are covered, then prove the controls actually work |
The last row is where many programs stop short. An ATT&CK map shows what should be covered; only testing shows what is.
How Does Picus Turn Threat Intelligence into Security Validation?
Picus approaches this from two directions. Picus CTI works continuously: it curates intelligence from hundreds of sources and your own feeds, builds a threat profile for your organization and maps indicators to ready-to-run simulations. Smart Threat works on demand: give it a single campaign report, and AI agents turn the adversary’s TTPs into an emulation plan. Either way, the result is a simulation you can run against your own controls.
From Hundreds of Feeds to One Threat Profile
Picus CTI aggregates hundreds of public and private sources, from vendor research and malware repositories to ISACs, CERTs and government advisories. A generative AI pipeline removes noise, normalizes and analyzes the data, then links threat actors, malware, CVEs and TTPs in a knowledge graph, with analyst review where needed. The output is a threat profile built around your sector, region and the actors most likely to target you.
From Intelligence to Simulation in One Step
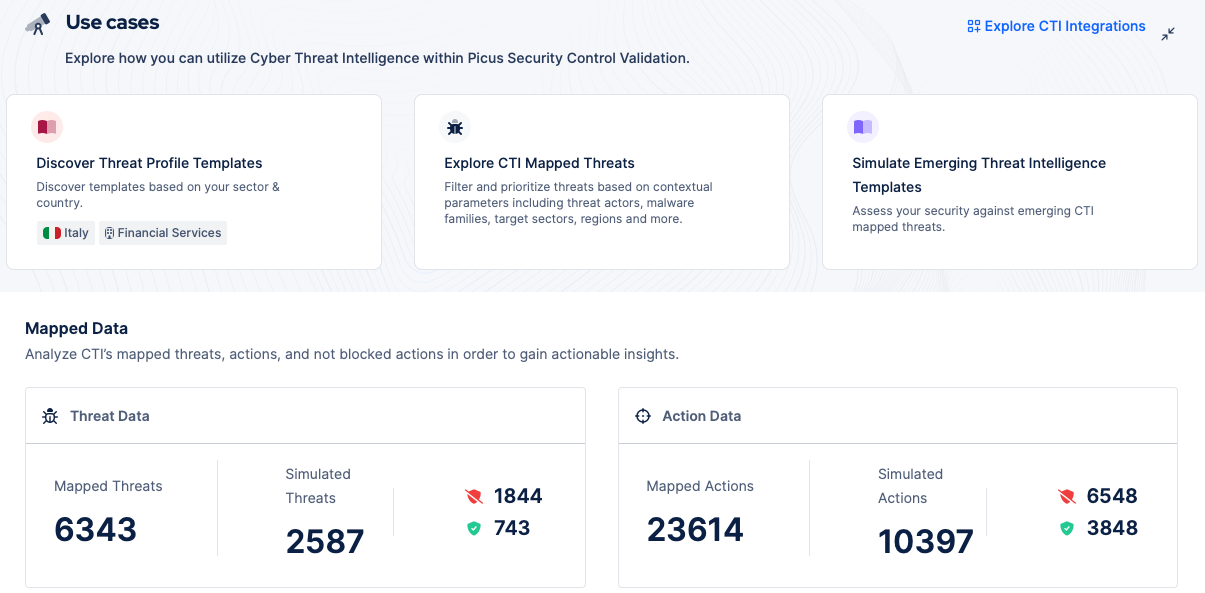
- Mapped to the Threat Library. Indicators are matched to ready-to-run attack simulations and enriched with threat actor, malware family, targeted sector and region.
- Dynamic threat templates. Templates by threat actor, sector and country, plus weekly and monthly templates, keep testing aligned with the newest intelligence.
- Your feeds, validated. Native integrations with CrowdStrike, Recorded Future, Dataminr (ThreatConnect) and Palo Alto Networks Cortex XSOAR TIM turn the intelligence you already buy into simulations, with file-hash and CVE lookups and score-based prioritization where available.
- Gaps first. Results surface the intelligence-mapped actions your controls missed, with vendor-specific mitigation guidance for the products you run.
As one Picus customer, a red team manager, puts it: enter the indicators, launch a simulation "and have a full report in about an hour."
From Headline to Emulation Plan with Smart Threat
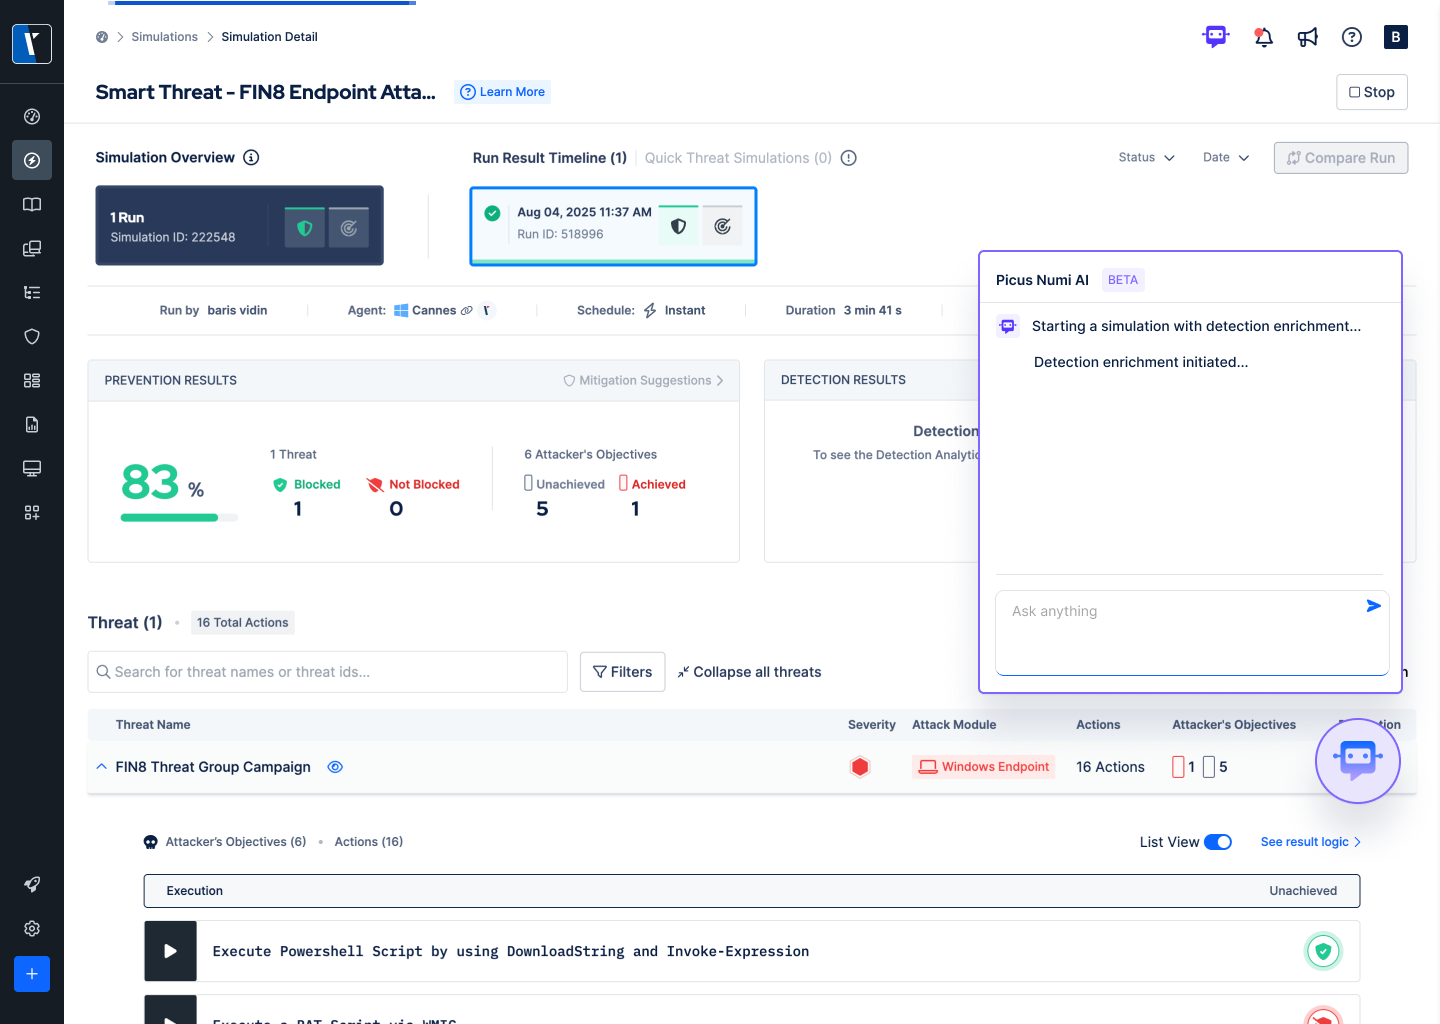
Feeds deliver indicators, but much of the most useful intelligence arrives as a campaign report or a news article. Picus Smart Threat turns that narrative into a test. Paste a single URL, such as a fresh report on a FIN8 campaign, and four AI agents take over:
- Planner Agent runs the workflow.
- Researcher Agent gathers related sources and checks that they are trustworthy.
- Threat Builder Agent extracts the adversary's TTPs and maps each one to a safe, pre-validated action in the Picus Threat Library through the Picus MCP server.
- Validation Agent reviews the mapping so no step is hallucinated.
The AI never writes payloads; it orchestrates simulations that already exist. The output is a ready-to-run emulation profile, mapped to MITRE ATT&CK, within hours of the headline.
See it against your own threat profile. Book your free demo to watch Picus CTI turn the threats targeting your sector into simulations and show which ones your defenses would actually stop.
