Key Takeaways
- The MiniPlasma zero-day exploit allows attackers to obtain SYSTEM-level privileges.
- Fully patched Windows 11 systems remain vulnerable to this specific attack.
- This exploit leverages an older vulnerability originally identified as CVE-2020-17103.
- The attack uses thread token impersonation to successfully trigger a race condition.
- The Picus Security Validation Platform simulates MiniPlasma attacks to test security controls.
MiniPlasma, a high-severity zero-day exploit based on CVE-2020-17103, grants SYSTEM access on Windows 11 and Server 2022/2025.
Recently, an independent security researcher named Chaotic Eclipse (Nightmare-Eclipse), who usually posts on GitHub, published his proof-of-concept for a new zero-day attack called MiniPlasma.
What makes this exploit stand out is the fact that it allows an attacker to obtain SYSTEM-level privileges even on Windows 11 systems that were patched recently. However, the bug that this exploit is using is not new either: it has been around for almost six years, and it first appeared in CVE-2020-17103, which was found by Google Project Zero researcher James Forshaw back then.
So, what does this attack do? Let’s take a closer look at the attack and see how Picus validates your defenses against this exploit.
Part 1: Understanding CVE-2020-17103: The Original Vulnerability
Background: What is the Cloud Filter Driver?
Cldflt.sys, referred to as the Cloud Files Mini Filter Driver, is a core component of the Windows operating system, responsible for various features, including OneDrive's "Files On-Demand," where files appear in the user directory while not being downloaded. In other words, they serve as placeholders. Upon opening one of such placeholders, it is being hydrated by pulling the actual content down from the cloud.
What is the Windows Registry and Why Should We Care?
Windows Registry can be regarded as the central storage of all settings related to the Windows operating system. This data is grouped in hives, which represent separate directories used by different users or, in some cases, belong to the system itself.
Of particular interest is the HKEY_USERS.DEFAULT hive, related to the SYSTEM account (highest privilege). It is normally impossible for a normal user to write into it.
Vulnerable Function: HsmOsBlockPlaceholderAccess
HsmOsBlockPlaceholderAccess enables cloud filter driver to block hydration of particular files for an app. More specifically, it creates so-called "block entries" in the registry on a per-user basis. This procedure consists of several kernel-mode operations:
- It calls another function called HsmiOsOpenAppPolicyKey, which in turn creates (opens) corresponding registry keys.
- Function HsmiOsOpenAppPolicyKey uses RtlOpenCurrentUser kernel API, which tries to get a handle to the user's hive by searching for his/her Security Identifier (SID).
The problem here is that there is no OBJ_FORCE_ACCESS_CHECK option specified when creating registry objects. To put it simply, the standard safety practice is to verify if the user really has the right to create the object. However, in this case, this check is bypassed, and the operation is performed directly within the kernel.
Additionally, RtlOpenCurrentUser performs a check for user's existence in the registry: it attempts to open the hive corresponding to their SID. And if such open failed with the error STATUS_OBJECT_NAME_NOT_FOUND, it switches to opening .DEFAULT hive automatically, which is the SYSTEM account hive.
So the question becomes: how do you make your own user hive appear "not found"?
The Race Condition: Winning the Timing Game
The key part of the vulnerability lies in this detail: Windows supports token impersonation, so that one can pretend to be another user for a period of time, and after that, revert impersonation and return privileges to themselves.
The Anonymous token, which exists on any Windows machine, has the unique identifier of its own. Therefore, while impersonated, the call of RtlOpenCurrentUser will fail with the right "not found" error since there is no hive assigned to this SID. However, impersonation will be switched back before the fall-back is executed, and .DEFAULT hive opened successfully.
The exploit uses two threads to trigger the race condition: one thread is performing token impersonation, the other is calling the vulnerable function.
The result is: registry keys get written to .DEFAULT, even though a normal user has no business touching it.
Part 2: MiniPlasma: The 2026 Rediscovery
The CVE-2020-17103 vulnerability had been discovered and disclosed to Microsoft in December 2020. Recently, a mysterious researcher going by the name of Chaotic Eclipse has found out that either the patch never went through or was silently rolled out by Microsoft afterwards, and demonstrated how the original proof of concept still works on current versions of Windows.
|
Original (2020) |
MiniPlasma (2026) |
|
|
Researcher |
James Forshaw (Google Project Zero) |
Chaotic Eclipse / Nightmare-Eclipse |
|
CVE |
CVE-2020-17103 |
No new CVE yet |
|
Status at time |
Reported and "fixed" |
Re-disclosed as still present |
|
PoC result |
Creates a harmless demo registry key |
Spawns a full SYSTEM shell |
|
Affected systems |
Windows 10 2004 |
Windows 11 + Server 2025 (fully patched) |
In order to show off the seriousness of the problem, Chaotic Eclipse decided to take the original proof of concept further and made it work as a privilege escalation: instead of simply adding registry keys, the modified tool spawned a SYSTEM shell.
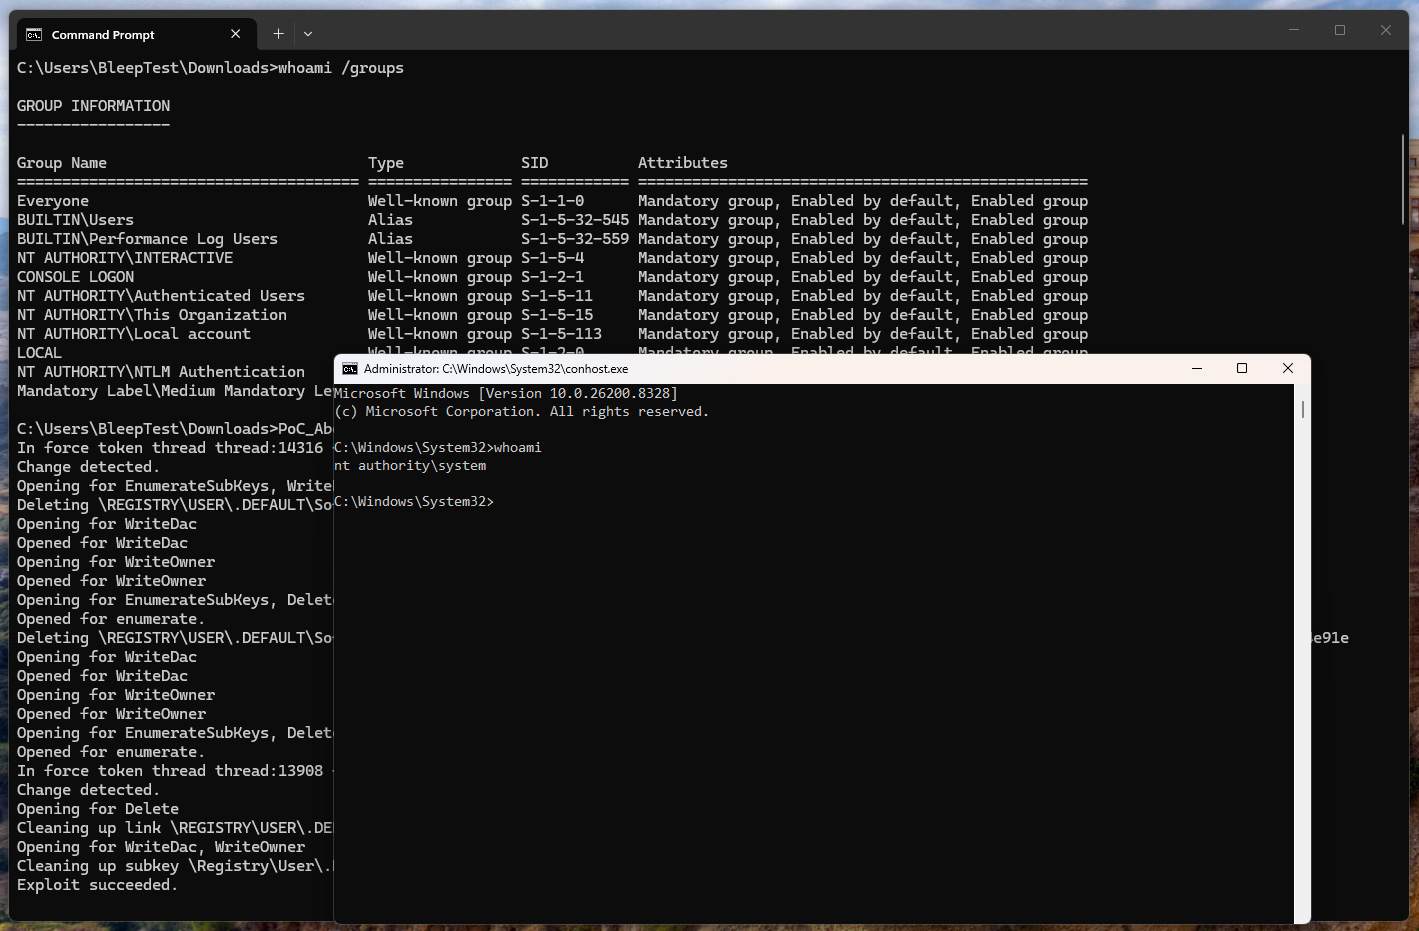
SYSTEM shell obtained using MiniPlasma (Source: BleepingComputer [1])
How to Mitigate MiniPlasma?
While there is currently no patch available for the MiniPlasma vulnerability, organizations should take immediate defensive actions. Below are three recommended mitigation strategies [2]:
- Apply Patches Urgently (Most Important): If and when a fix is released, applying the patch must be treated as an absolute priority.
- Enforce a Default-Deny Application Policy: This is currently the most effective mitigation strategy. A default-deny policy actively blocks the exploit payload at the point of execution, regardless of what the payload attempts to target.
- Monitor Specific Registry Paths via EDR: The MiniPlasma exploit manipulates specific registry locations during its execution, and alerts on these writes are strong indicators of malicious activity. You should configure your Endpoint Detection and Response (EDR) tools to monitor for modifications to the following paths:
-
\Registry\User\Software\Policies\Microsoft\CloudFiles\BlockedApp
- \Registry\User\.DEFAULT\Volatile Environment
-
How Picus Simulates MiniPlasma Attacks?
We also strongly suggest simulating MiniPlasma attacks to test the effectiveness of your security controls against real-life cyber attacks using the Picus Security Validation Platform. You can also test your defenses against other vulnerability exploitation attacks, such as regreSSHion, Citrix Bleed, and Follina, within minutes with a 14-day free trial of the Picus Platform.
Picus Threat Library includes the following threats for the MiniPlasma attacks:
|
Threat ID |
Threat Name |
Attack Module |
|
42850 |
Windows Cloud Filter MiniPlasma Elevation of Privilege Vulnerability Threat |
Network Infiltration |
|
24917 |
Windows Cloud Filter MiniPlasma Elevation of Privilege Vulnerability Threat |
E-mail Infiltration |
Start simulating emerging threats today and get actionable mitigation insights with a 14-day free trial of the Picus Security Validation Platform.
References
[1] L. Abrams, “New Windows ‘MiniPlasma’ zero-day exploit gives SYSTEM access, PoC released,” BleepingComputer. Accessed: Jun. 01, 2026. [Online]. Available: https://www.bleepingcomputer.com/news/microsoft/new-windows-miniplasma-zero-day-exploit-gives-system-access-poc-released/
[2] “MiniPlasma: Windows privilege escalation zero-day affects fully patched systems.” Accessed: Jun. 01, 2026. [Online]. Available: https://www.threatlocker.com/blog/miniplasma-windows-privilege-escalation-zero-day-affects-fully-patched-systems